Qilin (Agenda) Ransomware Deploys Linux Binaries on Windows via Remote Management Tools
Threat Actor Intelligence · 8 sources · Updated 5mo ago · First seen Oct 27, 2025
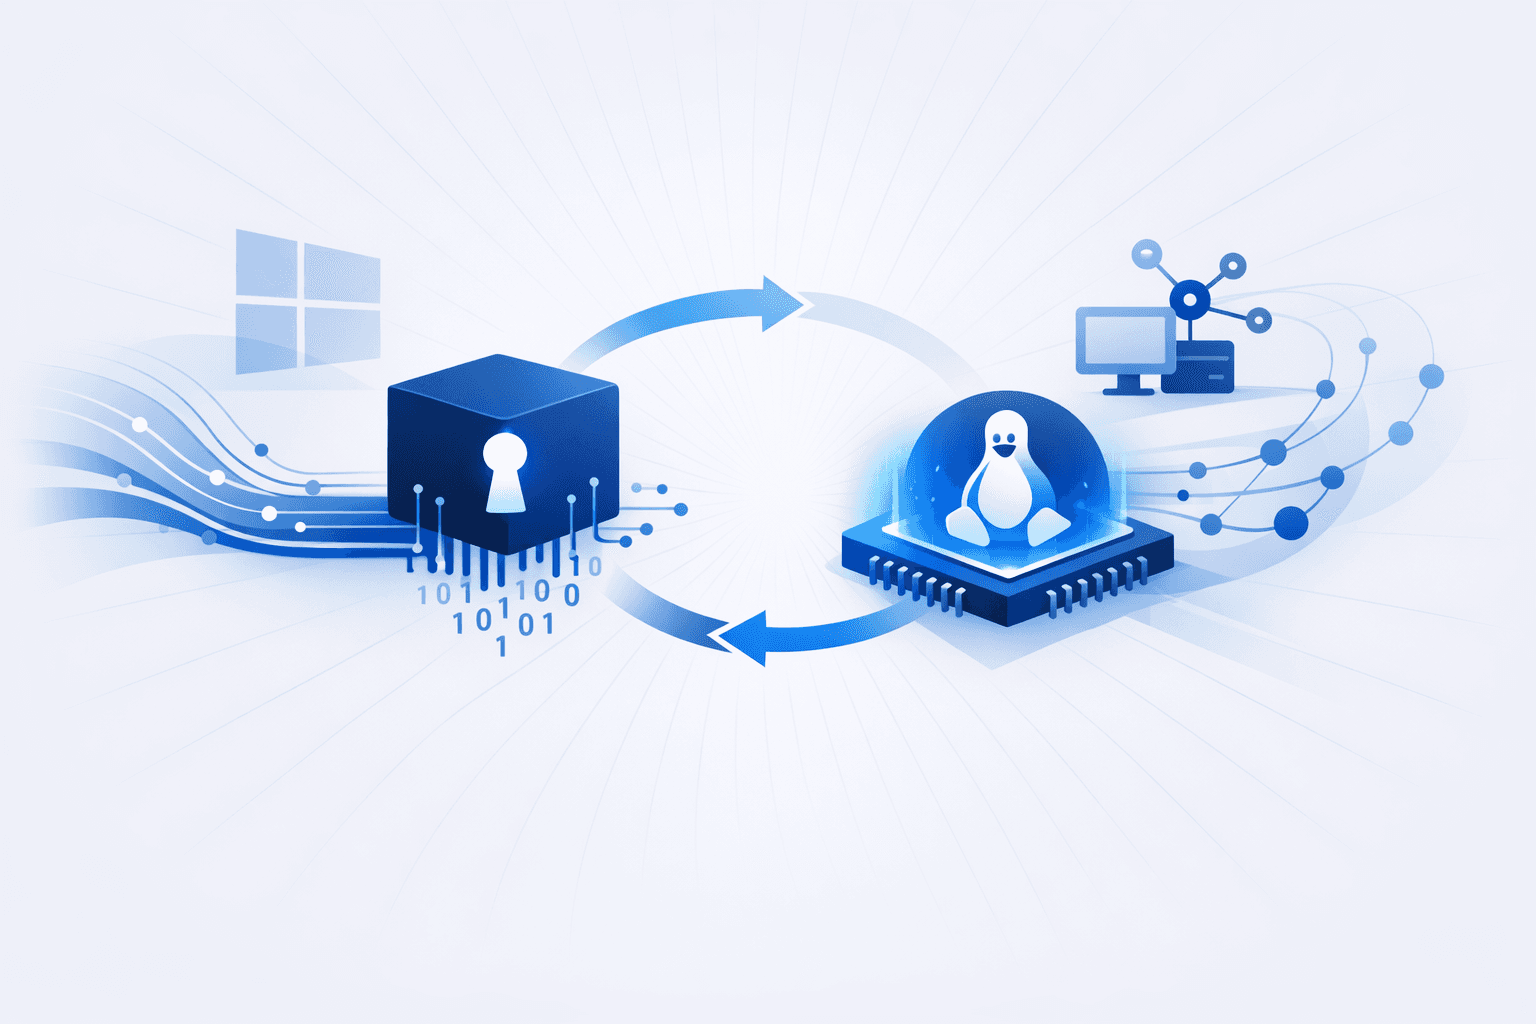
The Qilin ransomware group, also known as Agenda, has adopted a sophisticated cross-platform attack strategy by deploying Linux-based ransomware binaries on Windows systems. This technique leverages legitimate remote management and file transfer tools such as Splashtop, WinSCP, AnyDesk, ATERA RMM, ScreenConnect, and MeshCentral to bypass traditional Windows-centric endpoint detection and response (EDR) solutions. Attackers gain initial access through social engineering, including fake CAPTCHA pages, and use credential theft to facilitate lateral movement and privilege escalation. The group also employs Bring Your Own Vulnerable Driver (BYOVD) attacks to disable security defenses and steals backup credentials, particularly from Veeam, to prevent recovery and maximize extortion leverage.
Qilin's operations have impacted over 700 victims globally since January 2025, with a focus on sectors such as manufacturing, professional and scientific services, and wholesale trade. The group uses a double-extortion model, exfiltrating sensitive data with tools like Cyberduck before encrypting files and threatening public disclosure. Qilin's affiliates have been observed using a variety of post-exploitation tools, including Mimikatz and custom scripts, to harvest credentials and exfiltrate data. The group's rapid evolution and ability to evade detection highlight the growing sophistication of ransomware-as-a-service (RaaS) operations targeting organizations worldwide.