Solution Brief
8 min readHow Mallory helps you prioritize vulnerabilities
Rank findings by what a real adversary is doing right now, not by CVSS alone.
Read
Everything Mallory publishes, in one place. Browse by content type.
Showing all 43 resources
Rank findings by what a real adversary is doing right now, not by CVSS alone.
ReadMallory over MCP in both directions, plus Bring Your Own Key.
ReadMallory correlates nearly 9,000 intelligence sources with your attack surface, ranks exposures by what attackers are doing, and routes the work into your stack.
ReadMallory Agents investigate across your environment and hand your team completed findings, ranked in one queue.
Read
Patching your own nginx is the easy part. NGINX2Root also lives in gateways, NAS boxes, ingress controllers, and forks that ship on someone else's clock.
Read
We analyzed 859 public PHP2Shell repos and 290 exploitation reports, then checked concrete targets and prerequisites for mod_php, PHP-FPM and application-level exploit chains.
Read
The Binance theft in context: a year of North Korean developer targeting, from interview projects to malicious providers, and the controls crypto companies need.
Read
PHP, GitLab, and Node.js shipped security fixes on the same day. Four questions your CTEM program should help answer when urgent exposures pile up.
Read
Final update, November 1: CISA lists Node2Shell / HTTP2Shell as exploited. Reviewed attack reports, released fixes and remaining vendor gaps for CVE-2026-111497, with continuing coverage in Mallory's stories and CVE page.
Read
Final update, November 1: PHP2Shell exploitation is confirmed, both CVEs are in CISA KEV, and more vendors have shipped fixes. Updated remediation guidance, with continuing coverage in Mallory's stories and CVE pages.
Read
Mallory Agents investigate alerts and advisories, then file findings with evidence, severity, and remediation steps your team can triage, route, and track.
Read
Jace Davis, Mallory's first sales hire, on what drives him, why he wanted to build from a blank page, and the impact he wants to have.
Read
The Mallory App for Splunk imports Mallory's threat intelligence into Splunk ES, matches it against your telemetry, and reports every confirmed match back to Mallory as a sighting, automatically.
Read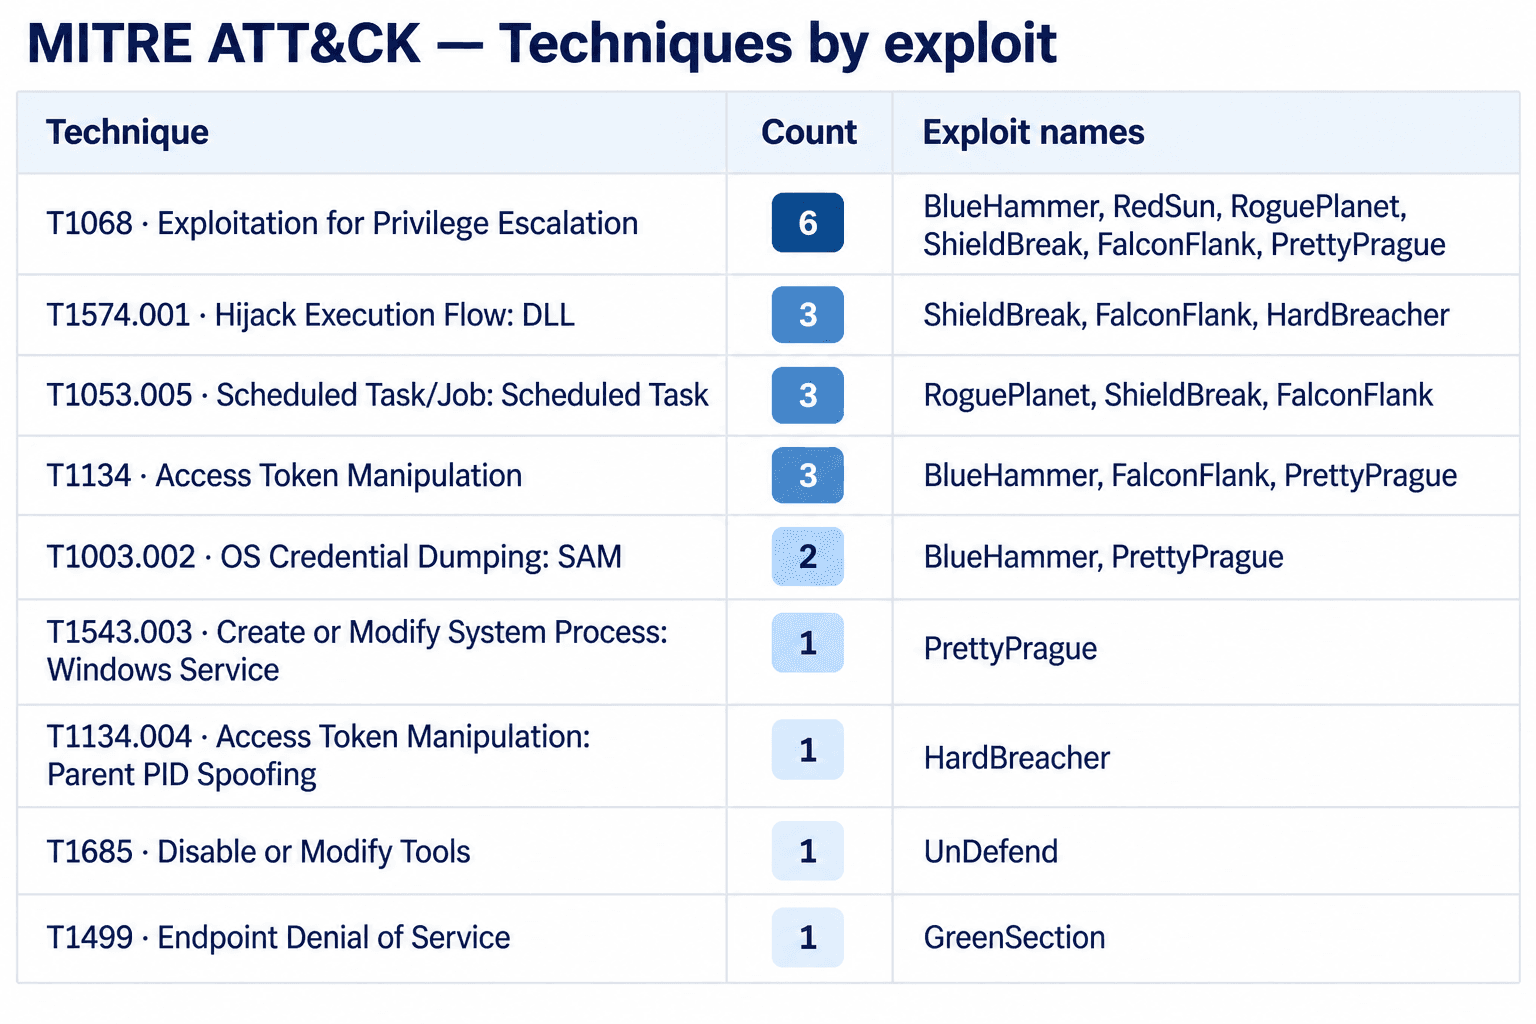
Nightmare-Eclipse expanded past Windows Defender to CrowdStrike, Avast, Kaspersky, and NVIDIA this year. Here's what's patched, confirmed, and still just a claim.
ReadWhy I joined Mallory as Founding Marketing Lead, and why this team is finally building exposure management right instead of bolting it on.
Read
At Black Hat USA 2026, Mallory researcher Maxim Gofnung traces Mortex from a one-off Claude Code result through a coordination failure, a runtime gap static analysis cannot see, and a sealed case landing in Mallory.
Read
BYOK lets the Mallory Agent reason on the AI provider your organization already vetted and contracted, instead of Mallory's own model account.
Read
AI has cut disclosure-to-exploitation to hours. Mallory's new architecture unifies context, reasoning, and policy so agents can act safely, under your rules.
Read
Six cybersecurity agency heads signed one statement on AI and cyber risk. Their answer is not more tools. It is the basics, done faster, because the gap between disclosure and exploitation is shrinking to months.
Read
CISA's new directive replaces fixed KEV deadlines with risk-based timelines. The bigger change: for the highest-risk vulnerabilities, agencies must now determine whether the asset was already compromised, within 72 hours.
Read
From an overnight supply chain compromise to a scheduled audit of your own GitHub org. A live stream of compromised packages, an agent that checks whether you're running any of them, and a daily 6am email with the answer.
Read
Our SOC 2 Type 2 examination is complete, less than 60 days after GA. The report is available to security teams under NDA.
Read
Vuln-ops gets talked about like a mythology. Here's what five minutes of it actually looks like in Mallory, from a Slack ping on Bleeding Llama (CVE-2026-7482) to on-demand Suricata rules.
Read
Cyber defense starts with situational awareness. Mallory Stories cluster millions of references into one coherent view, tailored to your environment.
Read
The Mallory team has built a modern cyber-security platform that sits at the intersection of AI-Native Operations and Exposure Management. Mallory's agentic capabilities serve several use cases, builders, and operators alike.
Read
Jonathan Cran joins Daniel Miessler on Unsupervised Learning for a full walkthrough of Mallory — from real-time threat stories and entity resolution to scheduled monitoring, asset context, and agent integration.
Read
The runZero co-founder on how his team uses Mallory to get ahead of new vulnerabilities — often notifying customers before the first news article drops.
Read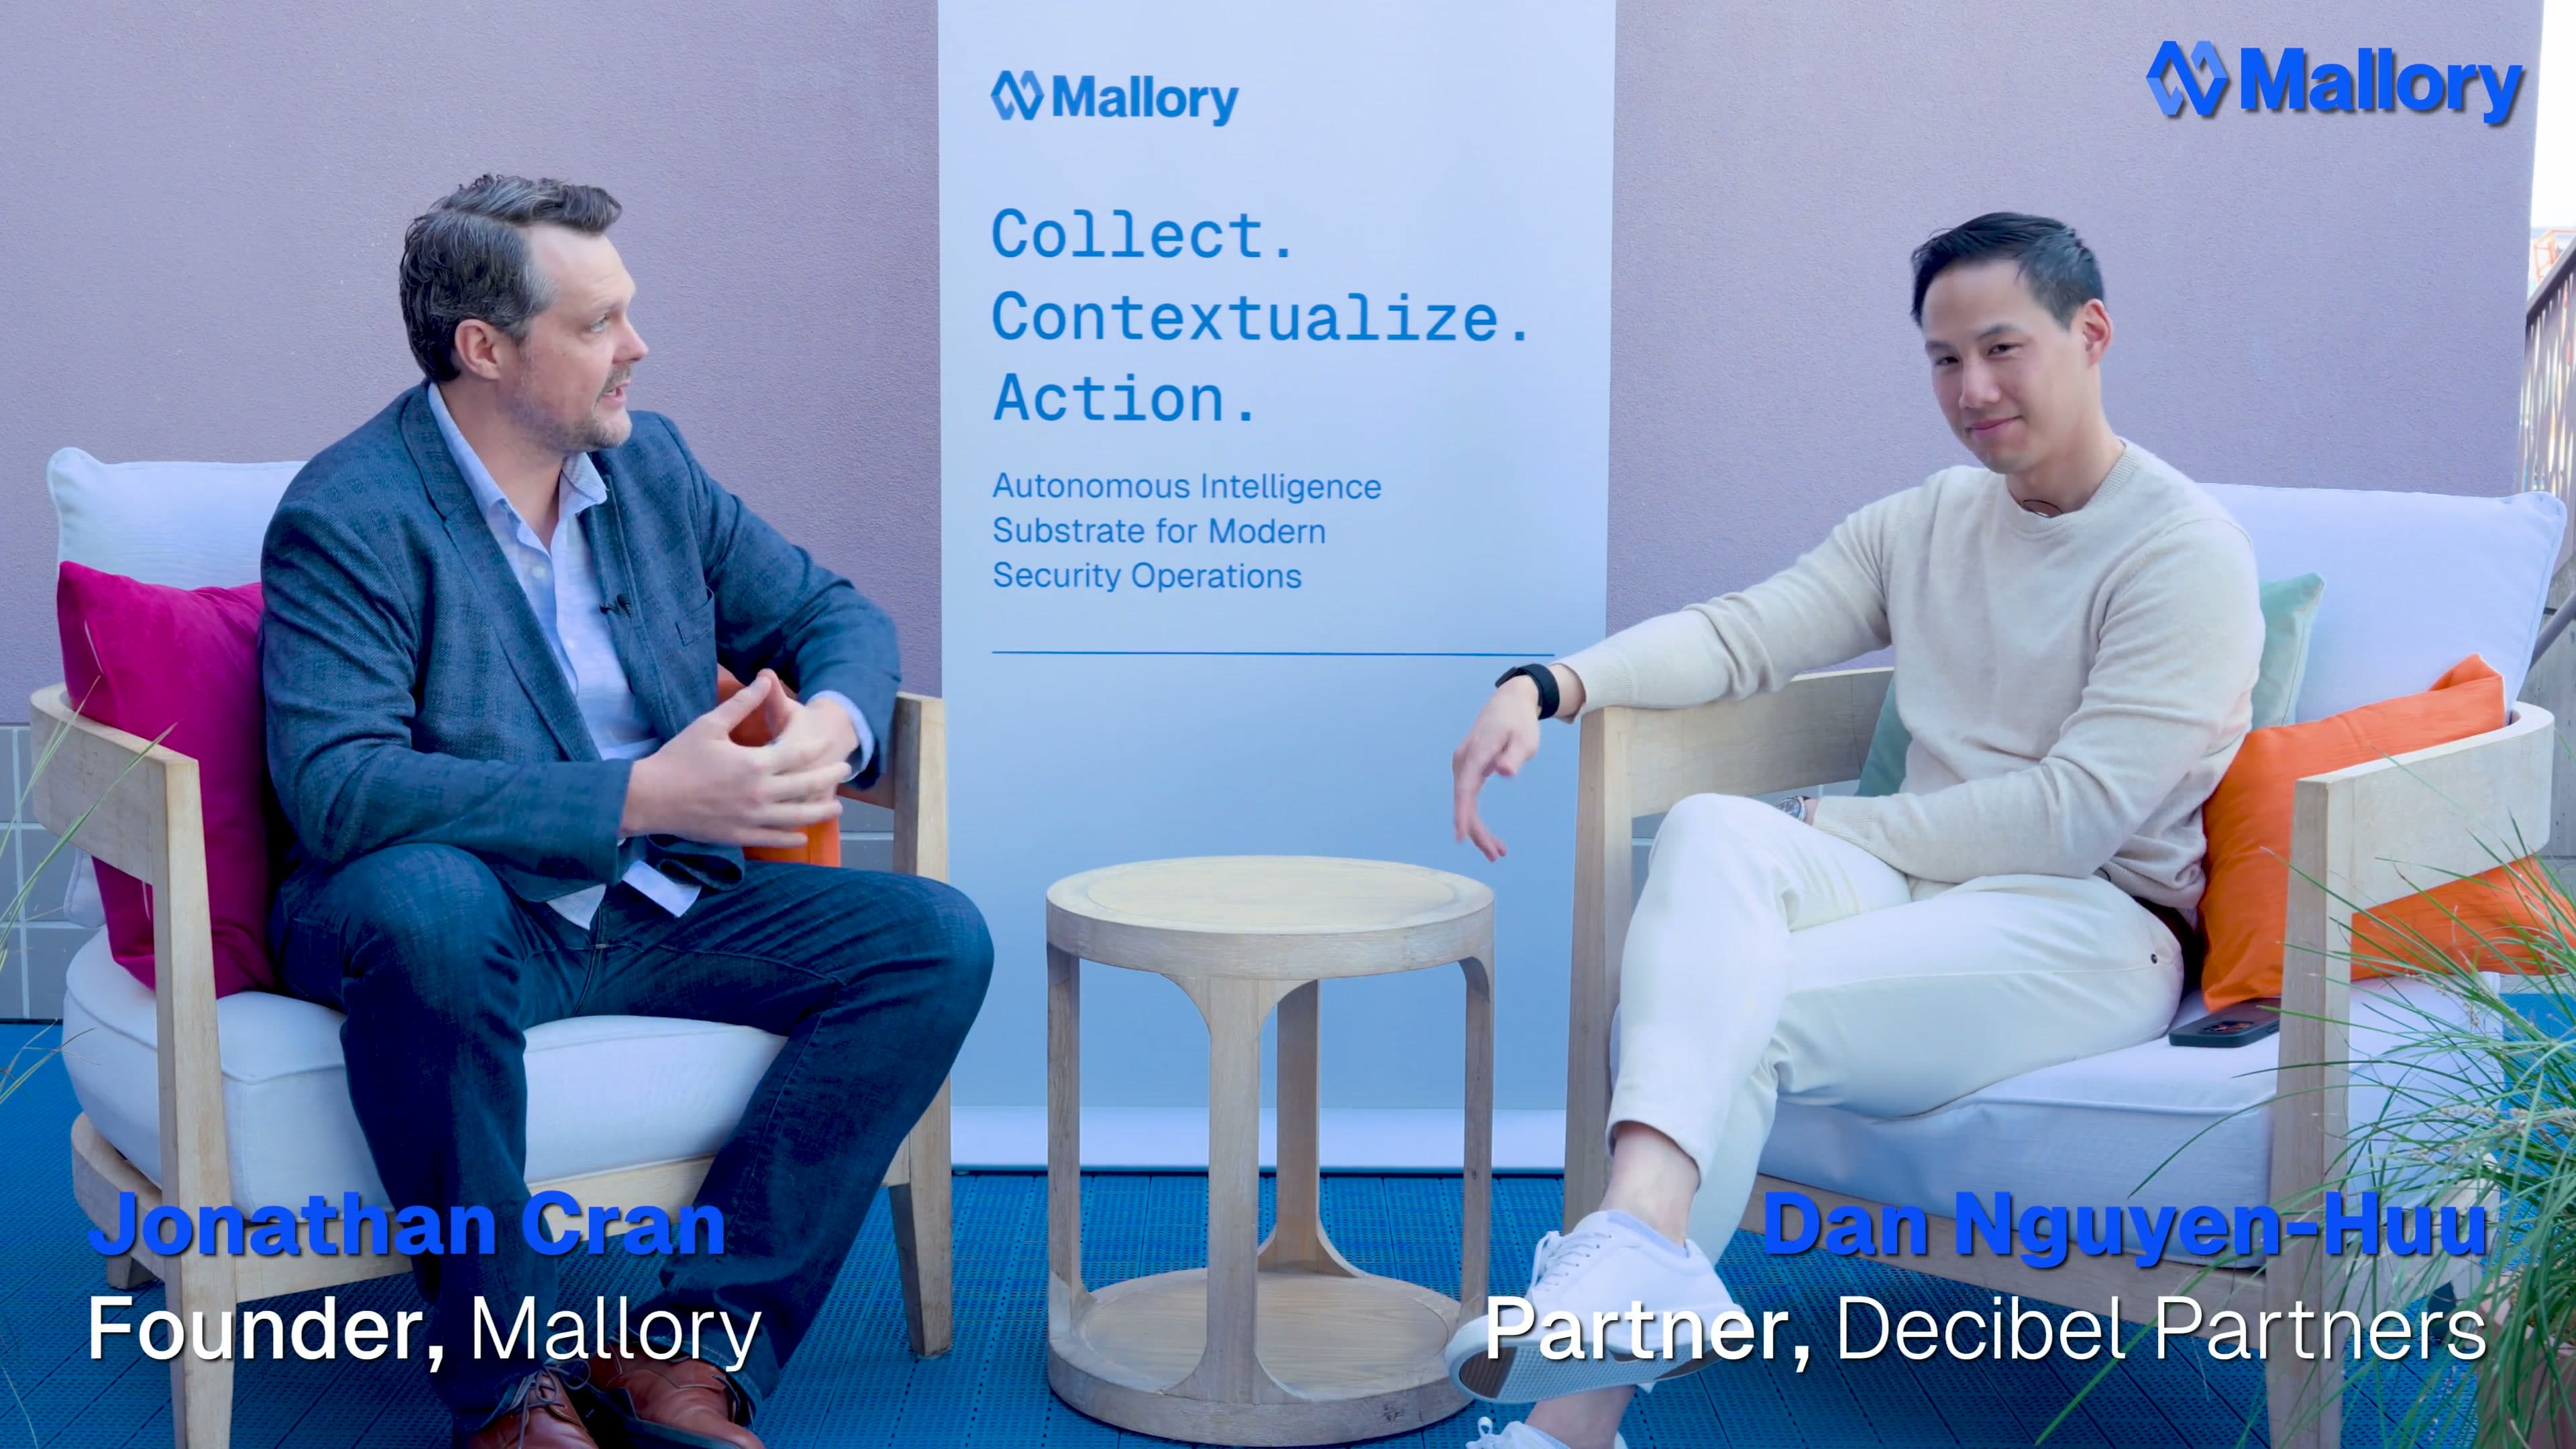
Decibel partner Dan Nguyen-Huu on the evolution of threat intelligence — from raw data feeds to contextualized, actionable insight delivered in the context of your environment.
Read
Longtime security practitioner Matt Johansen on why LLMs change everything for threat intelligence — from natural language queries to agents that act on intel autonomously.
Read
John Sapp runs dual managed services to triage alerts down to true positives. From there, Mallory is the force multiplier that enables his analysts to investigate deeply and respond fast.
Read
Our CEO Jonathan Cran on the problem Mallory was built to solve: helping security teams figure out if they're affected and take action, fast.
Read
Today, we're launching Mallory, our AI-Native Threat Intelligence Platform built for exposure investigation. Here's why we built it, what it does, and what's next.
Read
We're excited to introduce Mallory, a stealth-mode startup focused on supporting security operations teams through high quality and operationally efficient cyber threat intelligence.
Read
Our CEO Jonathan Cran on the problem Mallory was built to solve: helping security teams figure out if they're affected and take action, fast.
Watch
Jonathan Cran joins Daniel Miessler on Unsupervised Learning for a full walkthrough of Mallory — from breaking news and entity resolution to scheduled threat monitoring, asset context, and Claude Code integration.
Watch
John Sapp on running dual managed services to reduce alert fatigue, and using Mallory as a force multiplier for deep investigations once his SOC has triaged alerts down to true positives.
Watch
HD Moore on how runZero uses Mallory to get ahead of new vulnerabilities — often before the first news article is published.
Watch
Matt Johansen on why LLMs change everything for threat intelligence — from natural language queries to agents that consume and act on intel autonomously.
Watch
Dan Nguyen-Huu, Partner at Decibel, on why they backed Mallory and what makes the approach different from anything else in the market.
WatchGeorge V. Hulme features Mallory as an exemplar of the emerging VulnOps model — ingesting thousands of threat intel sources, mapping vulnerabilities to assets, and enabling human-AI collaboration through threads instead of traditional case management.
ReadMatt Johansen features Mallory on the Vulnerable U weekly livestream, walking through real-time threat stories and exposure investigation.
Read