Mallory
← Back to News
proof-of-concept-releasewidely-deployed-product-advisoryrapid-weaponizationinternet-facing-service-vulnerability

Remotely Exploitable Cache Poisoning Vulnerability in BIND 9 (CVE-2025-40778)

Patch & Detection Intelligence · 2 sources · Updated 5mo ago · First seen Oct 28, 2025

Remotely Exploitable Cache Poisoning Vulnerability in BIND 9 (CVE-2025-40778)

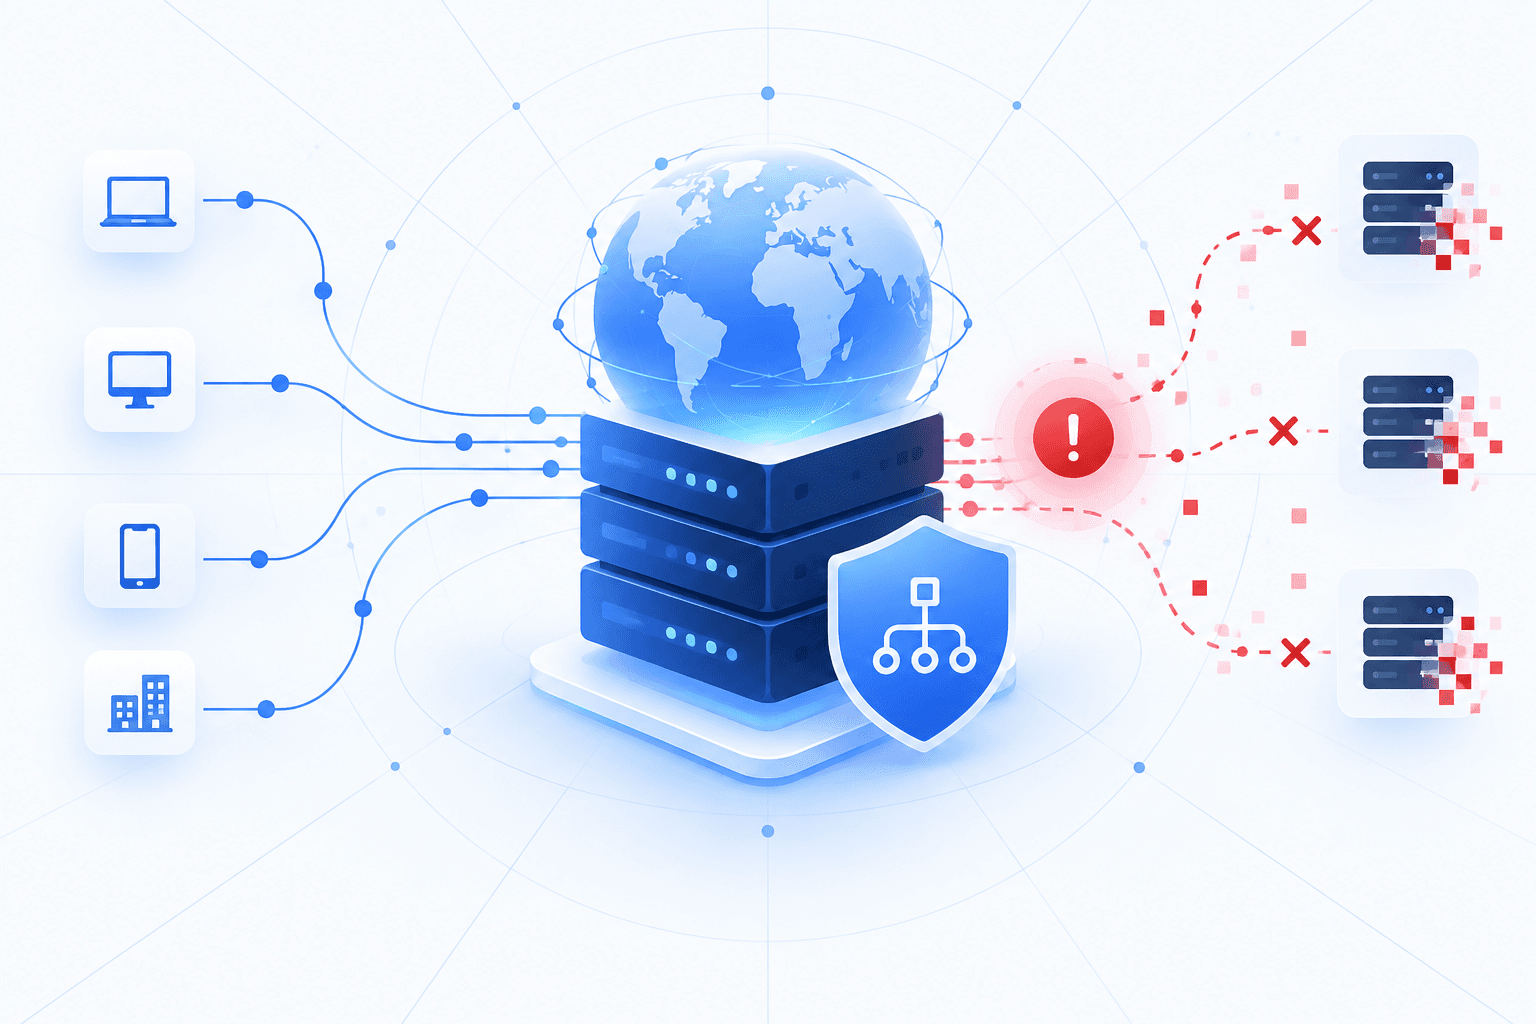
A high-severity vulnerability, CVE-2025-40778, has been identified in BIND 9 DNS resolvers, exposing over 706,000 servers worldwide to cache poisoning attacks. The flaw, which carries a CVSS v3.1 score of 8.6, allows remote, unauthenticated attackers to inject forged DNS records into resolver caches by exploiting BIND's overly permissive acceptance of certain DNS records in responses. This manipulation can redirect internet traffic to malicious sites, facilitate malware distribution, or enable interception of network communications, posing a significant risk to global DNS infrastructure.

The Internet Systems Consortium (ISC) has released advisories and patches addressing the vulnerability in multiple supported and preview versions of BIND 9, including versions 9.18.41, 9.20.15, and 9.21.14, as well as corresponding Supported Preview Edition releases. The publication of proof-of-concept exploit code has heightened the urgency for administrators to patch affected systems, particularly those running recursive DNS servers. While no active exploitation has been observed yet, the widespread use of BIND 9 and the critical nature of DNS services make prompt remediation essential to prevent large-scale attacks.
Patch this, or something else?See real exploitation activity before you spend the cycle.
Triage this advisory
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

5 events · Oct 27, 2025 – Oct 28, 2025
  1. Oct 28, 20251y ago

    BSI and Linux distributors issue follow-on mitigation guidance

    Germany's BSI published additional recommendations for securing recursive DNS servers, while multiple Linux distributions had already integrated or were preparing patches. These follow-on actions reflected broader ecosystem response to the vulnerability disclosure.

  2. Oct 28, 20251y ago

    PoC exploit code published for CVE-2025-40778

    Proof-of-concept exploit code for CVE-2025-40778 was published, increasing the urgency of patching despite no active exploitation being observed at the time. The publication lowered the barrier for attackers to attempt DNS cache-poisoning attacks.

  3. Oct 27, 20251y ago

    Researchers report broad internet exposure from vulnerable BIND 9 servers

    Reporting on the disclosure said the flaw threatened global DNS infrastructure and exposed roughly 706,000 internet-facing servers. The scale of exposure elevated concern over potential widespread abuse if exploitation began.

  4. Oct 27, 20251y ago

    Fixed BIND 9 versions released for CVE-2025-40778

    Fixes for CVE-2025-40778 were made available in BIND 9 versions 9.18.41, 9.20.15, 9.21.14 and corresponding Supported Preview Edition releases. Administrators were advised to upgrade immediately because no workaround was available.

  5. Oct 27, 20251y ago

    ISC discloses BIND 9 cache-poisoning flaw CVE-2025-40778

    A high-severity vulnerability, CVE-2025-40778, was disclosed in BIND 9 DNS resolvers that allows remote, unauthenticated attackers to poison DNS cache by injecting forged records. The issue also affects authoritative DNS servers when recursion is enabled.

Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.

Open in app →
Do you run this?See real exploitation activity behind this advisory so you can triage it against everything else in the queue.
Prioritize This Patch
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.