ClickFix Social Engineering Attacks Targeting European Hospitality Sector
Social Engineering & Fraud · 11 sources · Updated 5mo ago · First seen Jan 5, 2026
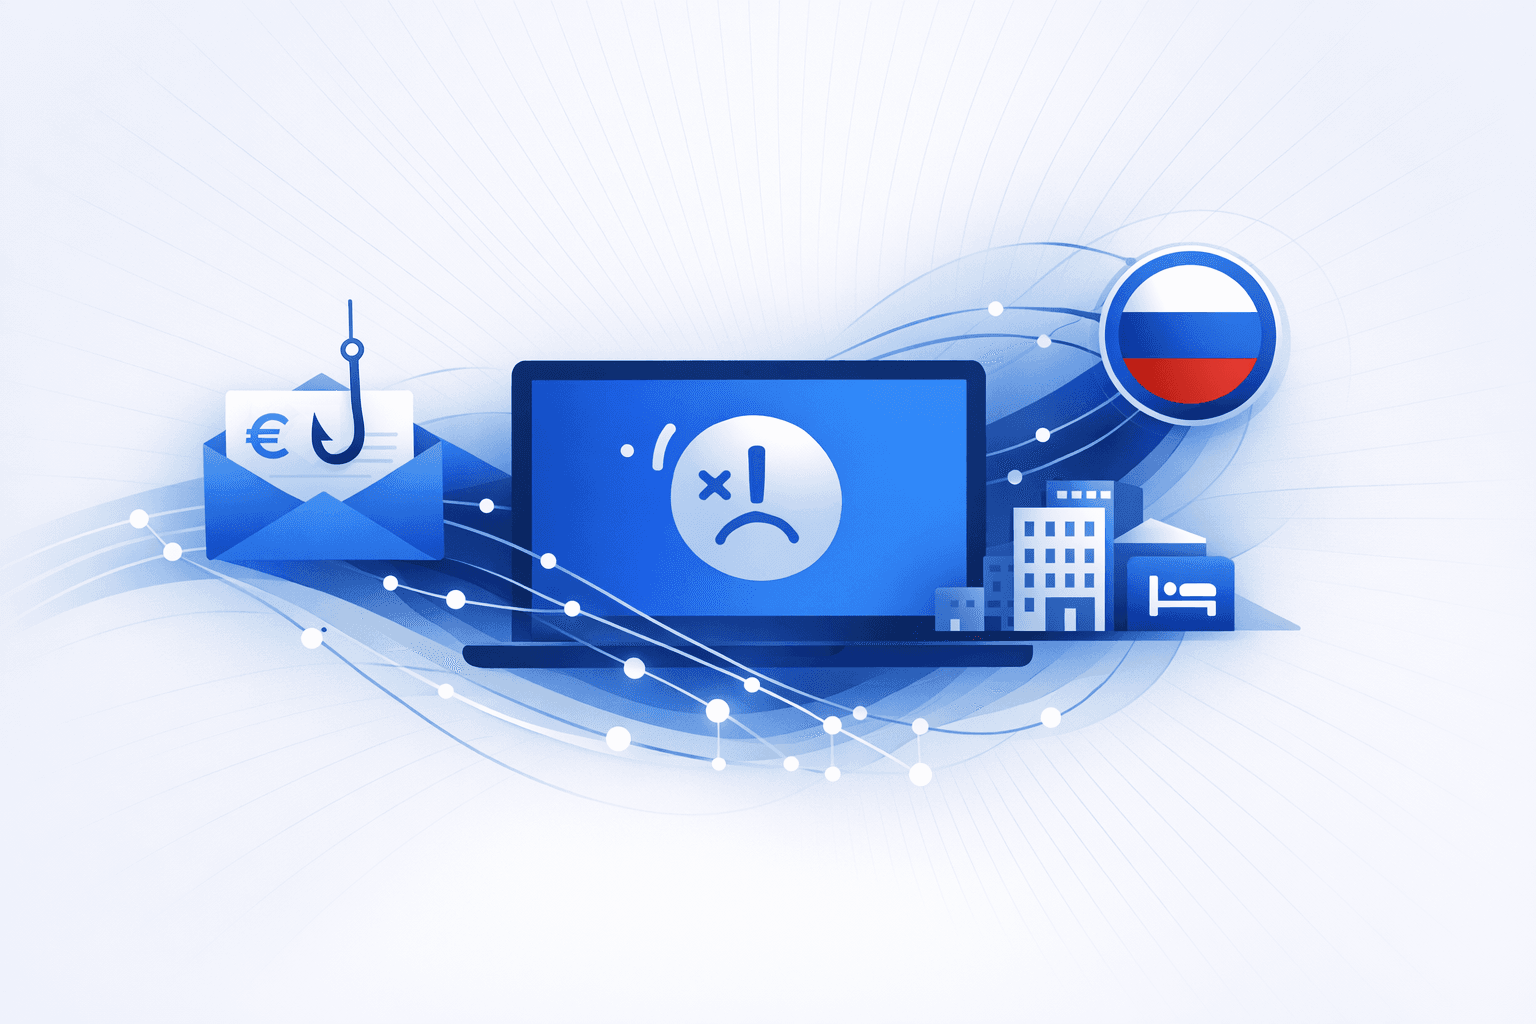
Suspected Russian cybercriminals have launched a sophisticated phishing campaign targeting the European hospitality industry, leveraging fake Windows Blue Screen of Death (BSOD) pages to distribute malware. The attack, tracked as "PHALT#BLYX" by Securonix researchers, begins with phishing emails impersonating popular booking platforms such as Booking.com, often using reservation cancellation lures with details in Euros to specifically target hotels, hostels, and inns in Europe. Victims are directed to high-fidelity cloned websites that mimic legitimate booking services, where they encounter fake error messages and BSOD screens designed to prompt them into executing malicious commands.
The campaign employs the "ClickFix" technique, which manipulates users into manually running PowerShell or shell commands under the guise of resolving system errors. This process ultimately results in the installation of the DCRat malware, a remote access trojan capable of keylogging and other malicious activities. Technical indicators, including Russian-language debug strings and infrastructure geolocated to Russia, suggest a strong Russian connection. The campaign demonstrates a blend of social engineering and technical deception, exploiting human problem-solving instincts to compromise systems within the hospitality sector during its busiest season.