Void Blizzard (Laundry Bear) Charity-Themed Lures Deliver PluggyApe Backdoor to Ukraine’s Defense Forces
Sector Threat Intelligence · 7 sources · Updated 5mo ago · First seen Jan 14, 2026
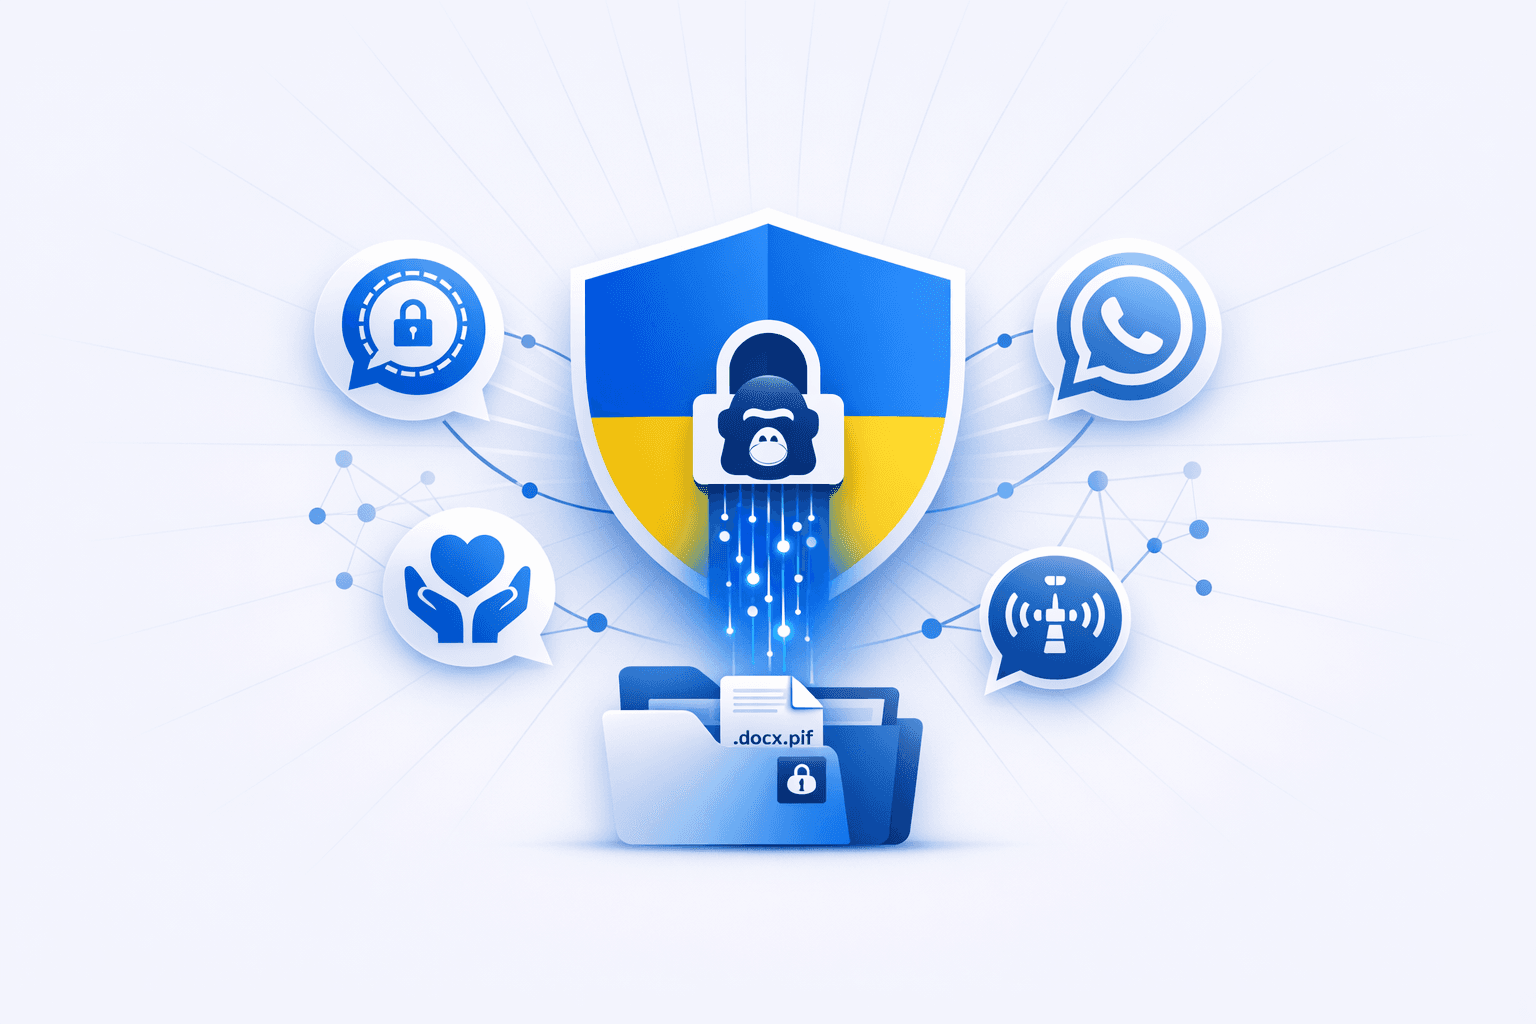
Ukraine’s CERT (CERT-UA) reported a cyber-espionage campaign targeting representatives of Ukraine’s Defense Forces between October and December 2025, using social-engineering lures themed around charitable foundations. Victims were contacted via Signal and WhatsApp and directed to charity-impersonation websites or sent password-protected archives that purported to contain documents but instead delivered executable payloads (including *.docx.pif), sometimes sent directly through the messaging apps.
The activity was attributed with medium confidence to the Russia-aligned threat actor Void Blizzard (also tracked as Laundry Bear and UAC-0190). The campaign deployed a previously undocumented backdoor dubbed PluggyApe, built as a Python executable packaged with PyInstaller, which profiles infected hosts, establishes persistence via Windows Registry modification, and enables remote command execution. CERT-UA noted an evolution in late 2025 from earlier loader naming patterns (e.g., *.pdf.exe) to PIF-based delivery and an updated PluggyApe v2 featuring stronger obfuscation, MQTT-based command-and-control, and additional anti-analysis checks.