Turla Deploys Upgraded Kazuar v3 Loader Using COM, ETW, and AMSI Evasion
Threat Actor Intelligence · 2 sources · Updated 5mo ago · First seen Jan 16, 2026
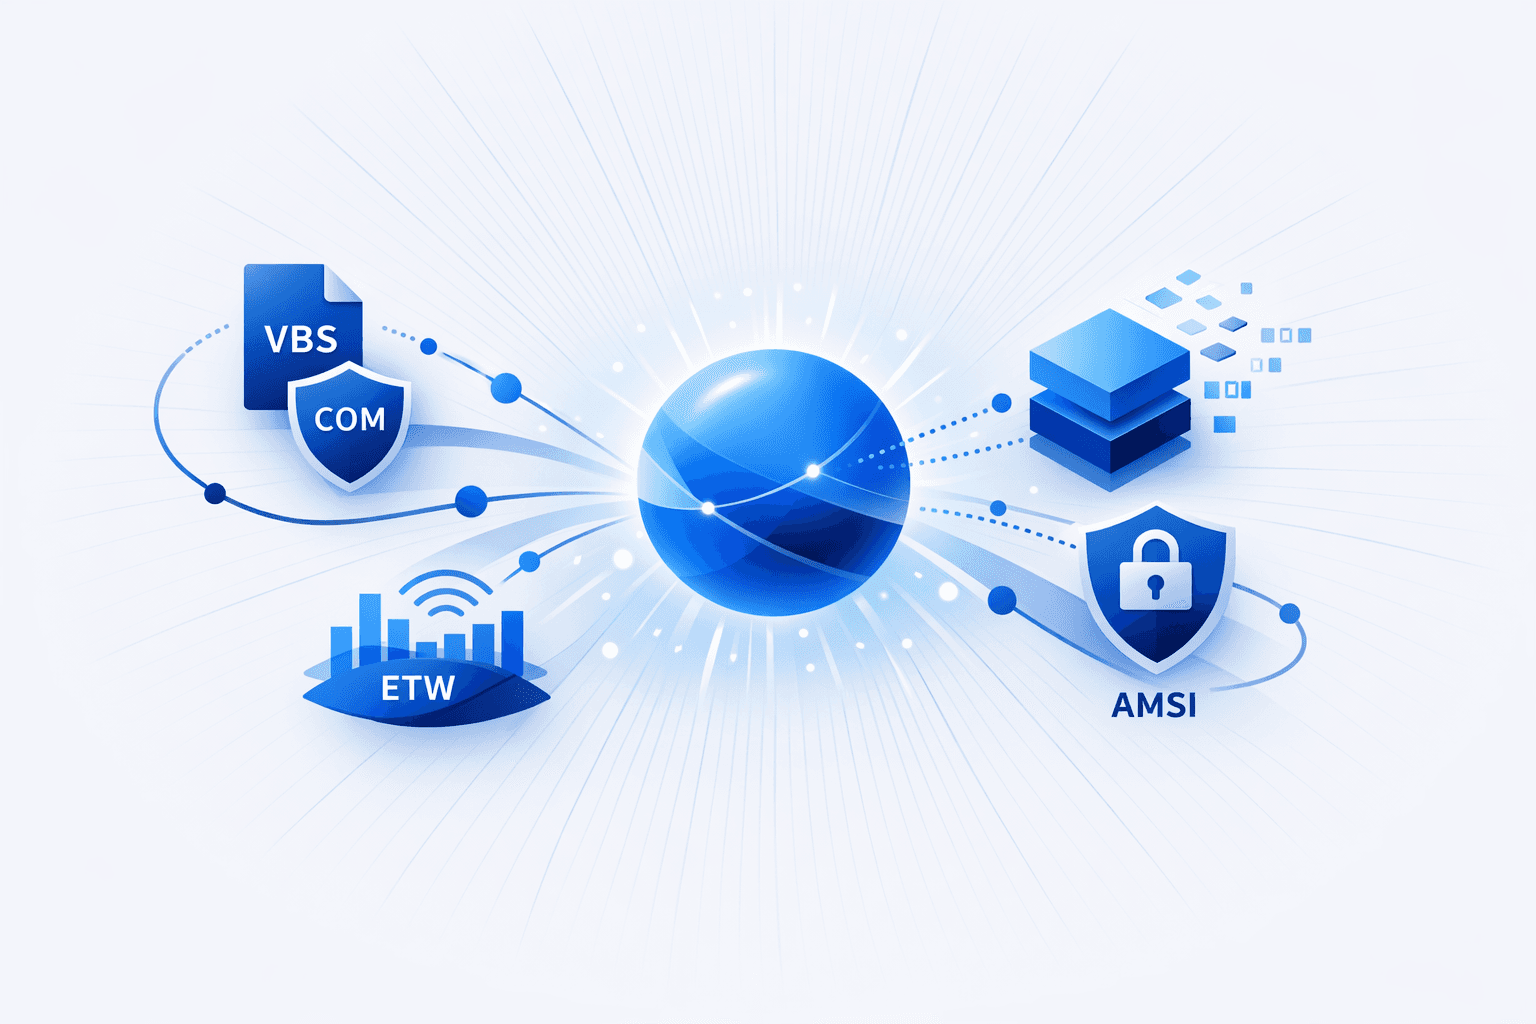
Researchers reported an upgraded Turla Kazuar v3 loader that uses advanced Windows-native evasion and execution techniques, including heavy use of Component Object Model (COM), patchless Event Tracing for Windows (ETW) manipulation, and AMSI bypass methods. The observed multi-stage chain begins with a VBScript (8RWRLT.vbs) that retrieves additional components from attacker infrastructure and stages multiple encrypted Kazuar payloads; analysis indicates the loader can embed execution logic into the Windows COM subsystem to blend into legitimate system activity and increase defender analysis time.
Technical reporting tied the activity to infrastructure and tradecraft consistent with prior reporting on Gamaredon–Turla operational overlap. The VBScript was observed downloading from https://185.126.255[.]132 and creating an HP-themed directory structure under %LOCALAPPDATA%\Programs\HP\..., then deploying a legitimate Hewlett-Packard installer alongside a malicious DLL for DLL sideloading, before decrypting and launching Kazuar payloads. The combination of COM-based execution, ETW/AMSI evasion, and staged encrypted payload delivery indicates a continued focus on stealthy post-compromise tooling rather than opportunistic commodity malware delivery.