MacSync macOS Infostealer Using ClickFix-Style Terminal Paste Lure to Steal Cryptocurrency Data
Malware Intelligence · 2 sources · Updated 4mo ago · First seen Jan 23, 2026
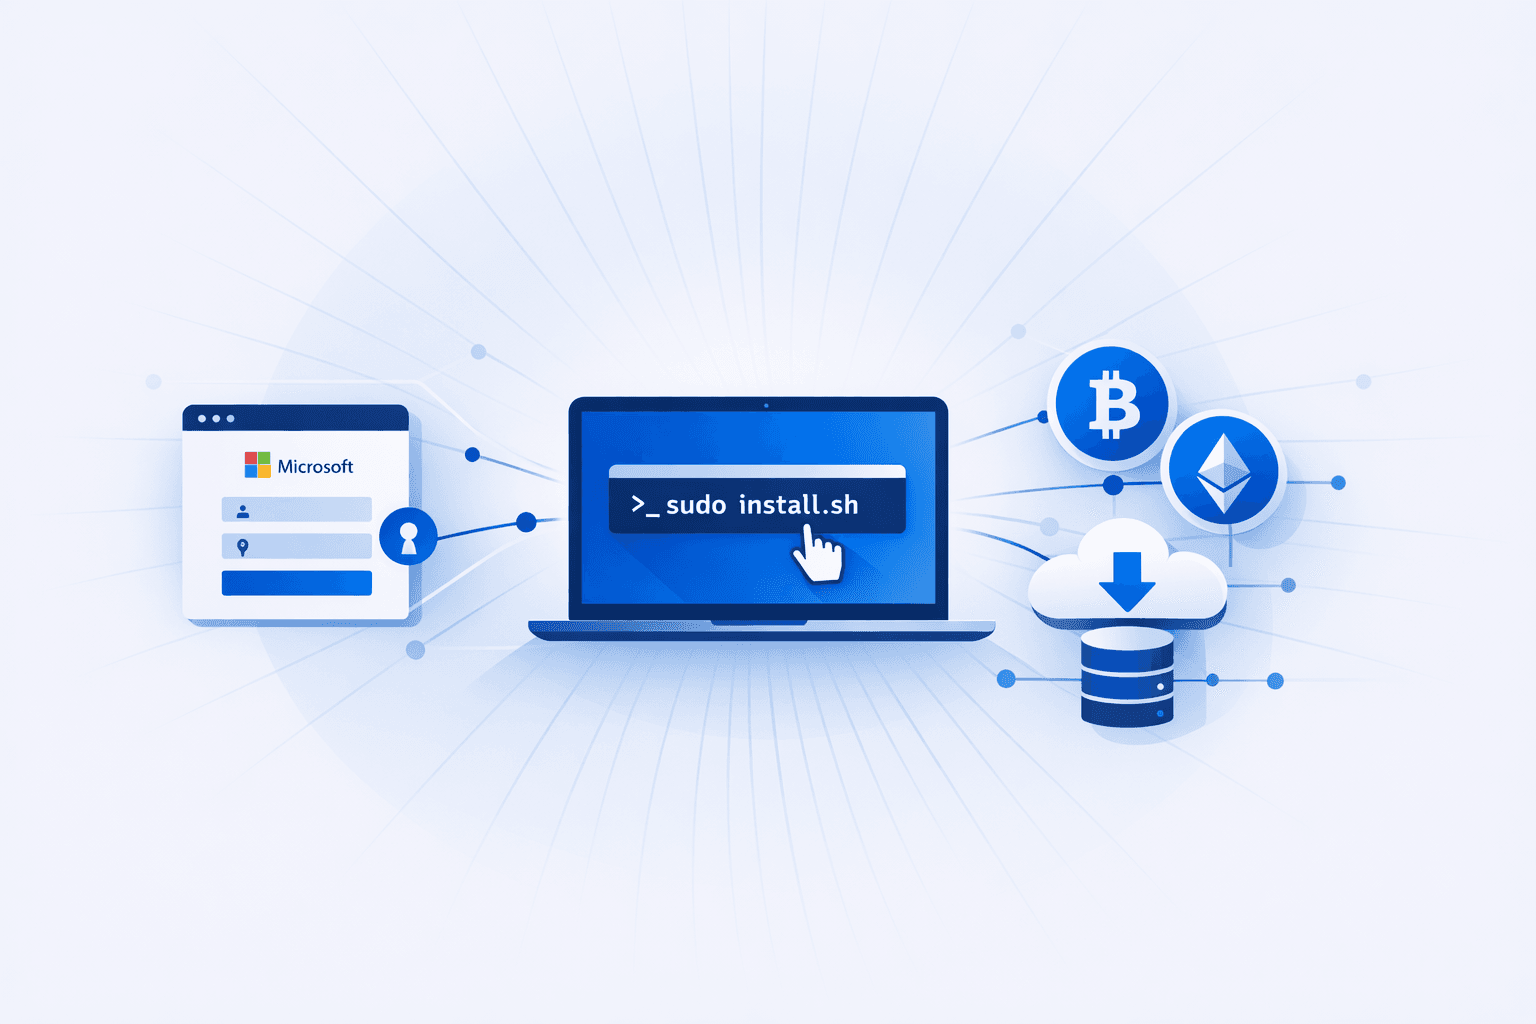
Security researchers reported a macOS infostealer dubbed MacSync being distributed as a low-cost Malware-as-a-Service (MaaS), primarily targeting cryptocurrency users via a ClickFix-style social engineering lure. The campaign uses phishing infrastructure (including domains mimicking Microsoft login pages) to redirect victims to a fake macOS cloud storage installer site that instructs users to “install” by copying and pasting a single Terminal command. This approach relies on user execution rather than a signed app package, allowing the infection chain to bypass macOS protections such as Gatekeeper and notarization.
Technical analysis describes a script-based, multi-stage infection chain: the pasted one-liner fetches a remote script that installs a daemonized Zsh loader which detaches from the Terminal session and runs in the background, then retrieves additional payloads (including AppleScript) to perform data theft. Beyond credential and wallet data harvesting, reporting indicates MacSync can persist and expand impact by trojanizing Electron-based cryptocurrency applications (e.g., Ledger Live and Trezor Suite) by overwriting components to present convincing phishing flows designed to capture PINs and recovery phrases, potentially triggering theft well after the initial compromise.