Regulatory Enforcement and Penalty Updates for Privacy Violations
Regulatory & Policy · 3 sources · Updated 4mo ago · First seen Jan 29, 2026
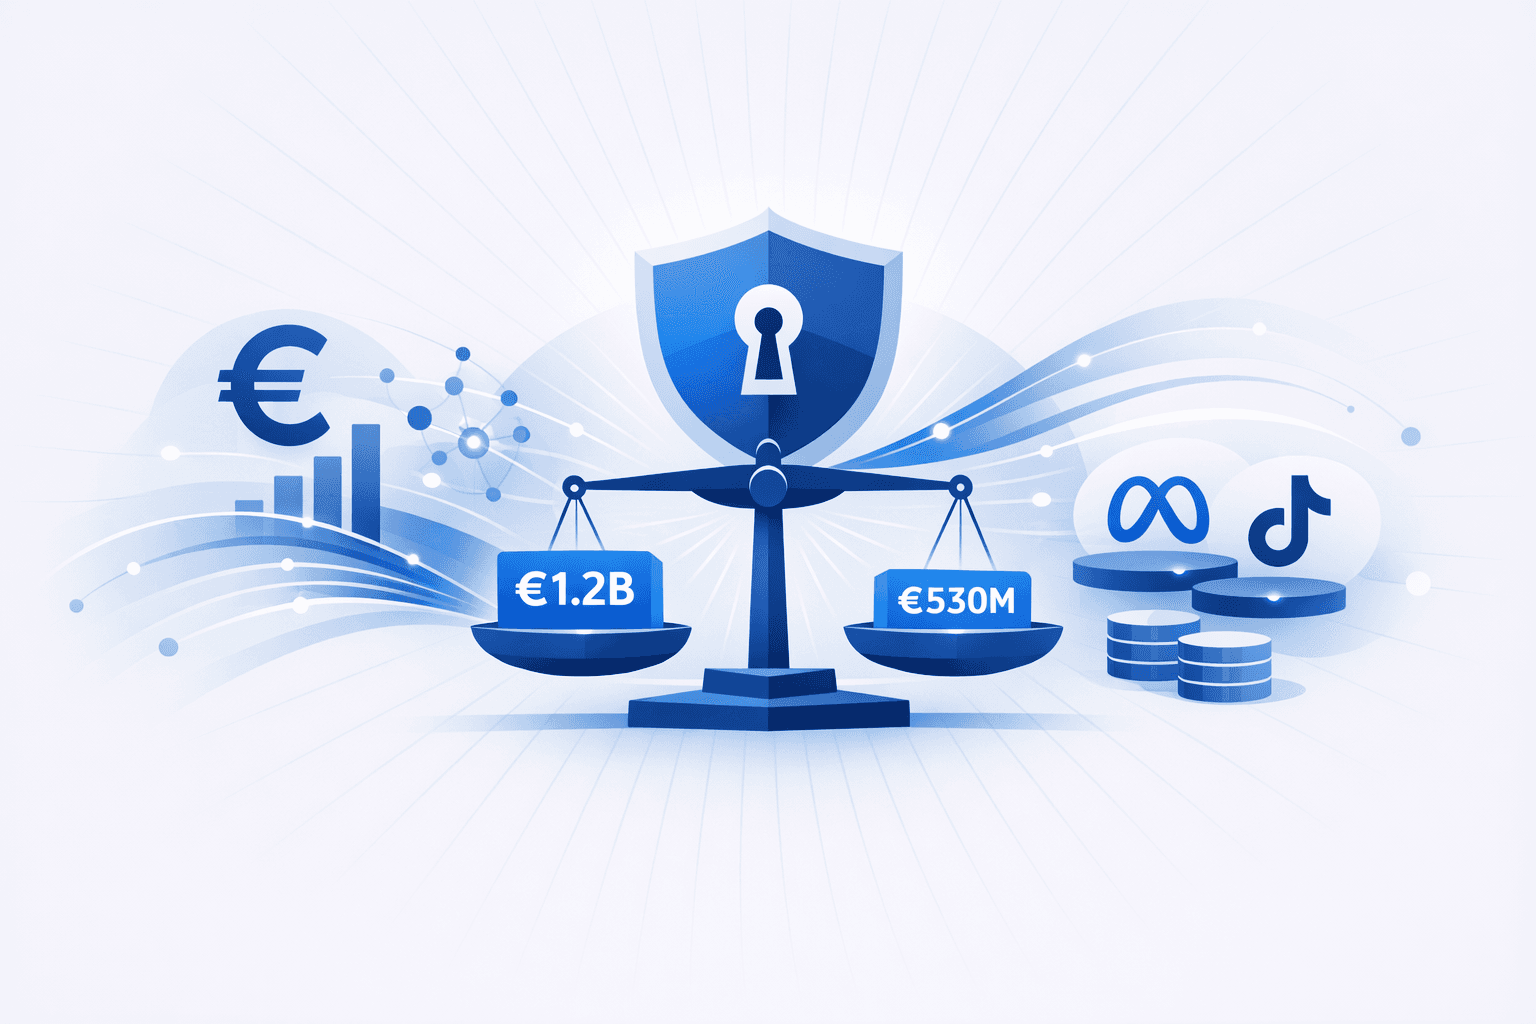
Regulators and courts continued to impose and update financial consequences for privacy violations across major regimes. In the EU, GDPR enforcement remained significant, with cumulative fines since 2018 reaching €7.1B and annual totals around €1.2B, while Ireland’s Data Protection Commission continued to lead enforcement totals due to the EU headquarters of major US tech firms; notable penalties cited include €1.2B against Meta Platforms Ireland Ltd. and €530M against TikTok for alleged transfers of EU user data to China.
In the US, Apple began issuing payments under a $95M settlement tied to allegations that Siri captured private conversations and that data was used for advertising, with per-device payouts reported as variable and capped (up to five devices per claimant). Separately, the US Department of Health and Human Services’ Office for Civil Rights implemented an inflation-based increase to HIPAA civil monetary penalties effective immediately, updating tiered per-violation minimums and maximums and noting the adjustment was applied later than the statutory schedule required under the federal inflation adjustment framework.