Malicious Google Search Ads and Forged Apple Pages Trick macOS Users Into Running Terminal Commands
Social Engineering & Fraud · 2 sources · Updated 4mo ago · First seen Jan 31, 2026
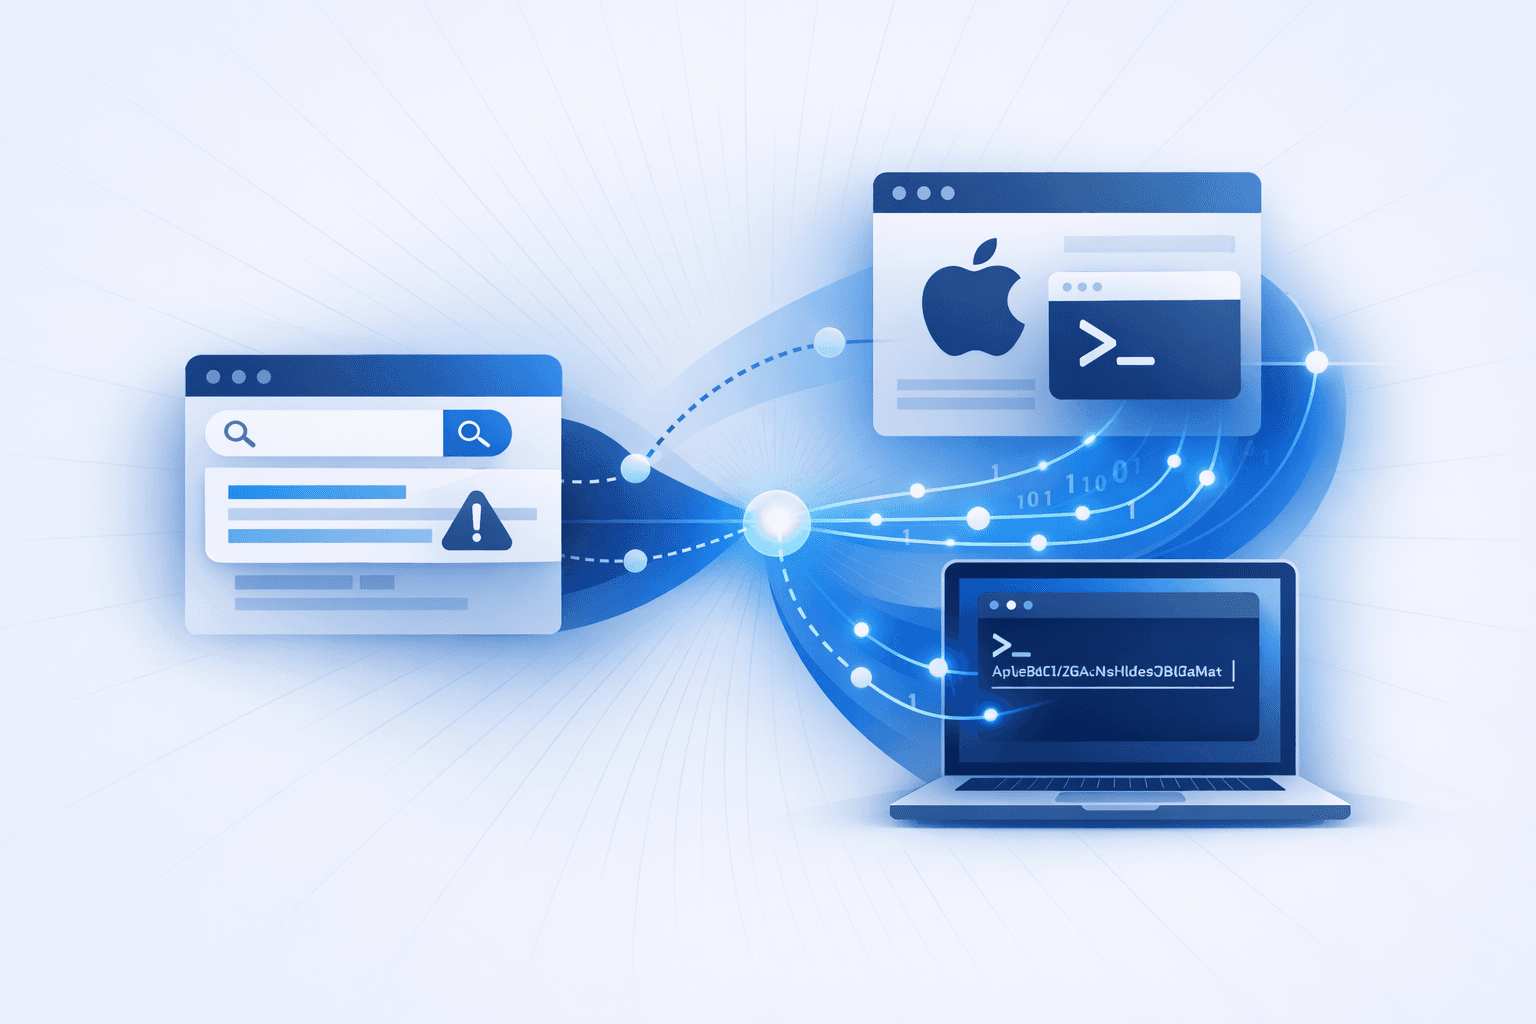
Security researchers reported an active macOS social-engineering campaign that abuses Google Search sponsored results and Google-hosted content (notably docs.google.com, and also business.google.com) to funnel users to forged Apple Support-like pages and other lookalike content (including Medium posts). The pages instruct victims—often searching for “mac cleaner” tools or macOS maintenance tasks like clearing cache—to copy/paste an obfuscated Base64 command into Terminal, which then downloads and executes a follow-on script with the user’s permissions.
Once executed, the payload can enable remote access and data theft, including harvesting sensitive files and SSH keys, and may also deploy additional malware or cryptomining. One report ties the activity to delivery of the AMOS (aka SOMA) stealer, which was observed creating artifacts such as .agent (AppleScript used to run theft), .mainHelper (Mach-O binary), and .pass (password stored in plaintext), and attempting to access user data including Documents and Notes. Researchers also noted the apparent use of compromised, Google-verified advertiser accounts to place the malicious ads, helping the campaign bypass ad-platform trust checks.