Mallory
← Back to News
actively-exploited-vulnerabilitystate-sponsored-espionagephishing-campaign-intelligenceendpoint-software-vulnerability

APT28 Exploits Microsoft Office RTF Zero-Day (CVE-2026-21509) in Operation Neusploit

Active Exploitation · 7 sources · Updated 3mo ago · First seen Feb 3, 2026
APT28 Exploits Microsoft Office RTF Zero-Day (CVE-2026-21509) in Operation Neusploit

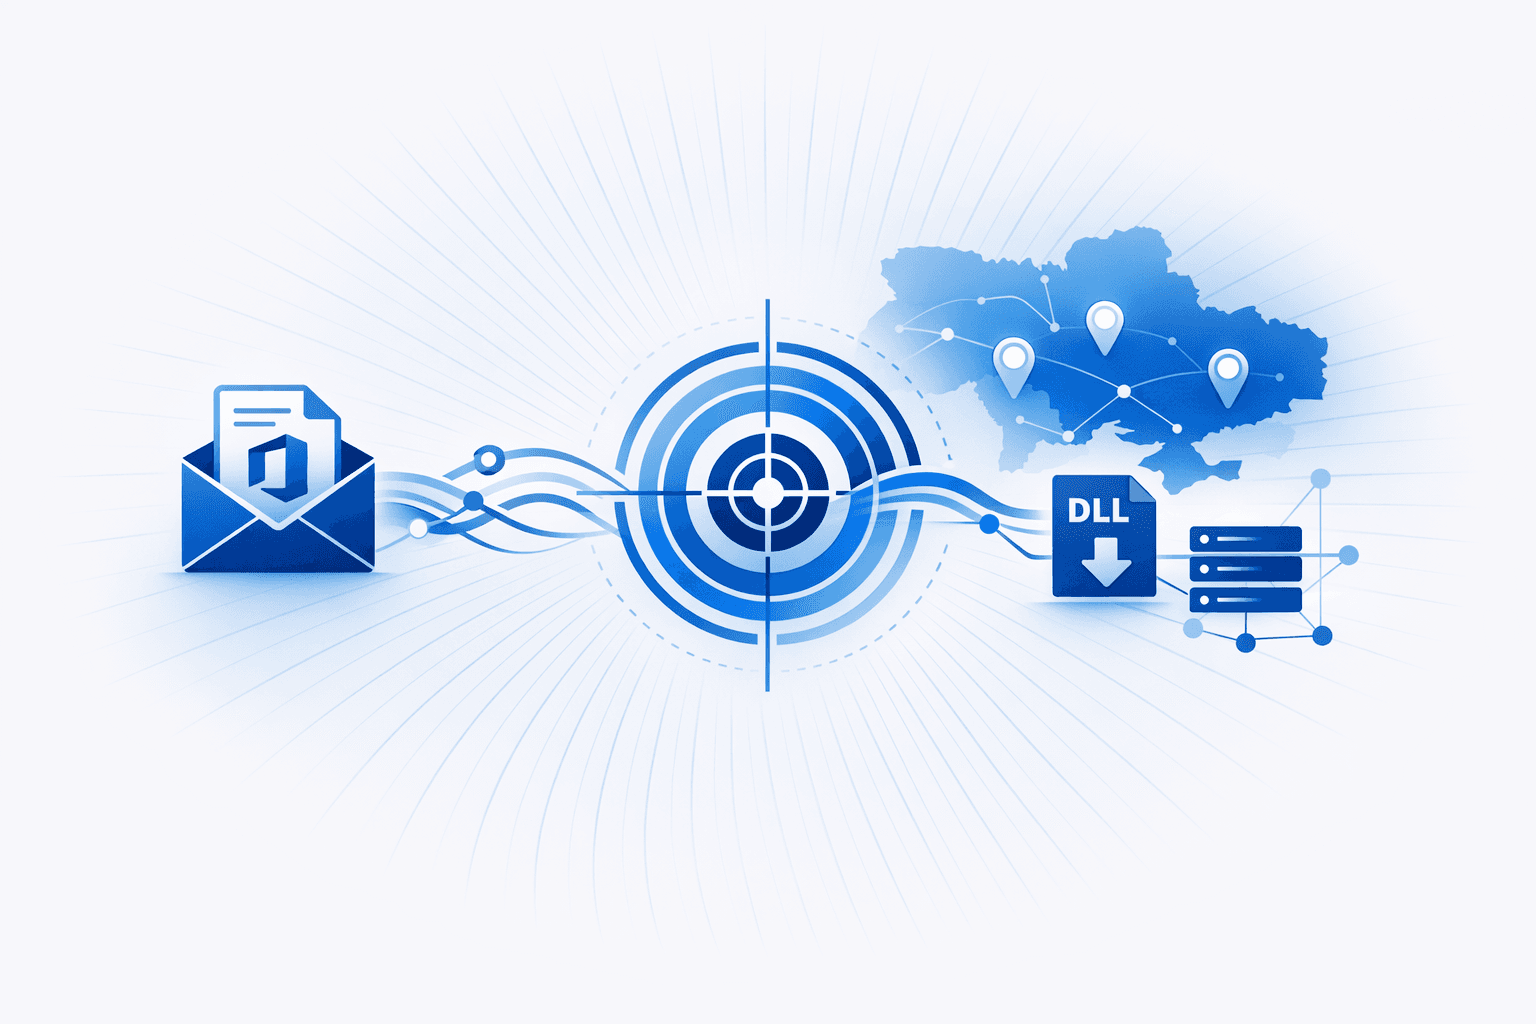
APT28 (Russia-linked) has been observed exploiting a Microsoft Office RTF zero-day, CVE-2026-21509, in a campaign dubbed Operation Neusploit targeting organizations in Central and Eastern Europe (including Ukraine, Slovakia, and Romania). The intrusion chain begins with socially engineered emails delivering weaponized RTF documents; opening the file triggers code execution and downloads a malicious dropper DLL from attacker-controlled infrastructure, enabling follow-on payload deployment and persistence.

Technical analysis describes two dropper variants that deploy different components, including MiniDoor, a malicious Microsoft Outlook VBA project designed to steal and forward emails. Observed behaviors include writing the VBA payload to %appdata%\Microsoft\Outlook\VbaProject.OTM, creating a mutex (adjgfenkbe), and modifying Windows Registry settings to weaken Outlook security so the malicious project loads automatically at Outlook startup; string decryption uses XOR routines (including a hardcoded 0x3a key and a rolling XOR key). Reporting attributes the activity to APT28 based on TTP overlaps and notes exploitation was seen in the wild shortly after Microsoft issued an emergency fix.

This is being exploited nowSee which actors are running it and whether you're in range.
Check your exposure
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

6 events · Sep 2025 – Feb 4, 2026
  1. Feb 4, 202610mo ago

    CISA adds CVE-2026-21509 to Known Exploited Vulnerabilities catalog

    CISA added Microsoft Office zero-day CVE-2026-21509 to its Known Exploited Vulnerabilities catalog following reports of active exploitation. The CSIRT.SK notice highlighted the KEV listing alongside patching guidance, mitigations, and indicators of compromise.

    Microsoft opravil aktívne zneužívanú zero-day zraniteľnosť v balíku Office | CSIRT.SK
  2. Feb 2, 202610mo ago

    ThreatLabz publishes technical analysis of Operation Neusploit

    Zscaler ThreatLabz publicly disclosed technical details of Operation Neusploit, including exploitation via crafted RTF files, selective payload delivery, and the two malware variants MiniDoor and PixyNetLoader. The report also described persistence, Outlook abuse, steganography, and use of Filen API as a command-and-control bridge.

  3. Jan 31, 202610mo ago

    Zscaler identifies and attributes Operation Neusploit to APT28

    In January 2026, Zscaler ThreatLabz identified the campaign and attributed it to APT28 based on overlaps in tools, techniques, and procedures. The operation used two attack-chain variants delivering either the MiniDoor Outlook email-stealing implant or the PixyNetLoader/Covenant Grunt path.

  4. Jan 29, 202610mo ago

    APT28 exploitation of CVE-2026-21509 observed in the wild

    Active exploitation of CVE-2026-21509 was observed on weaponized RTF documents used in socially engineered emails targeting Central and Eastern Europe. The campaign delivered malware through a multi-stage infection chain and was later dubbed Operation Neusploit.

  5. Jan 26, 202610mo ago

    Microsoft issues emergency patch for CVE-2026-21509

    Microsoft released an emergency patch for the Microsoft Office zero-day CVE-2026-21509. The flaw was later linked to APT28's Operation Neusploit campaign.

  6. Sep 2025

    Pawn Storm begins PRISMEX campaign against Ukrainian support infrastructure

    TrendAI reported that Pawn Storm/APT28 had been running campaigns since at least September 2025 using the PRISMEX malware suite against Ukrainian defense operations and Western military and humanitarian support infrastructure. The activity included PrismexSheet-based steganographic delivery and targeted sectors such as defense supply chains, meteorological services, transport hubs, and aid corridors.

    Pawn Storm Campaign Deploys PRISMEX, Targets Government and Critical Infrastructure Entities | TrendAI (US)
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Threat actors

1 linked

Affected products

1 linked
Microsoft Office

Organizations

1 linked
Microsoft Corporation

Observables

9 linked

Indicator values are masked on this page. View all 9 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Correlate live exploitation activity against the software you actually run, and see where you're exposed.
See Who's Exploiting This
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.