Spearphishing Campaigns Abuse PDF and Windows Screensaver Files to Install Legitimate RMM Tools
Social Engineering & Fraud · 3 sources · Updated 5mo ago · First seen Feb 6, 2026
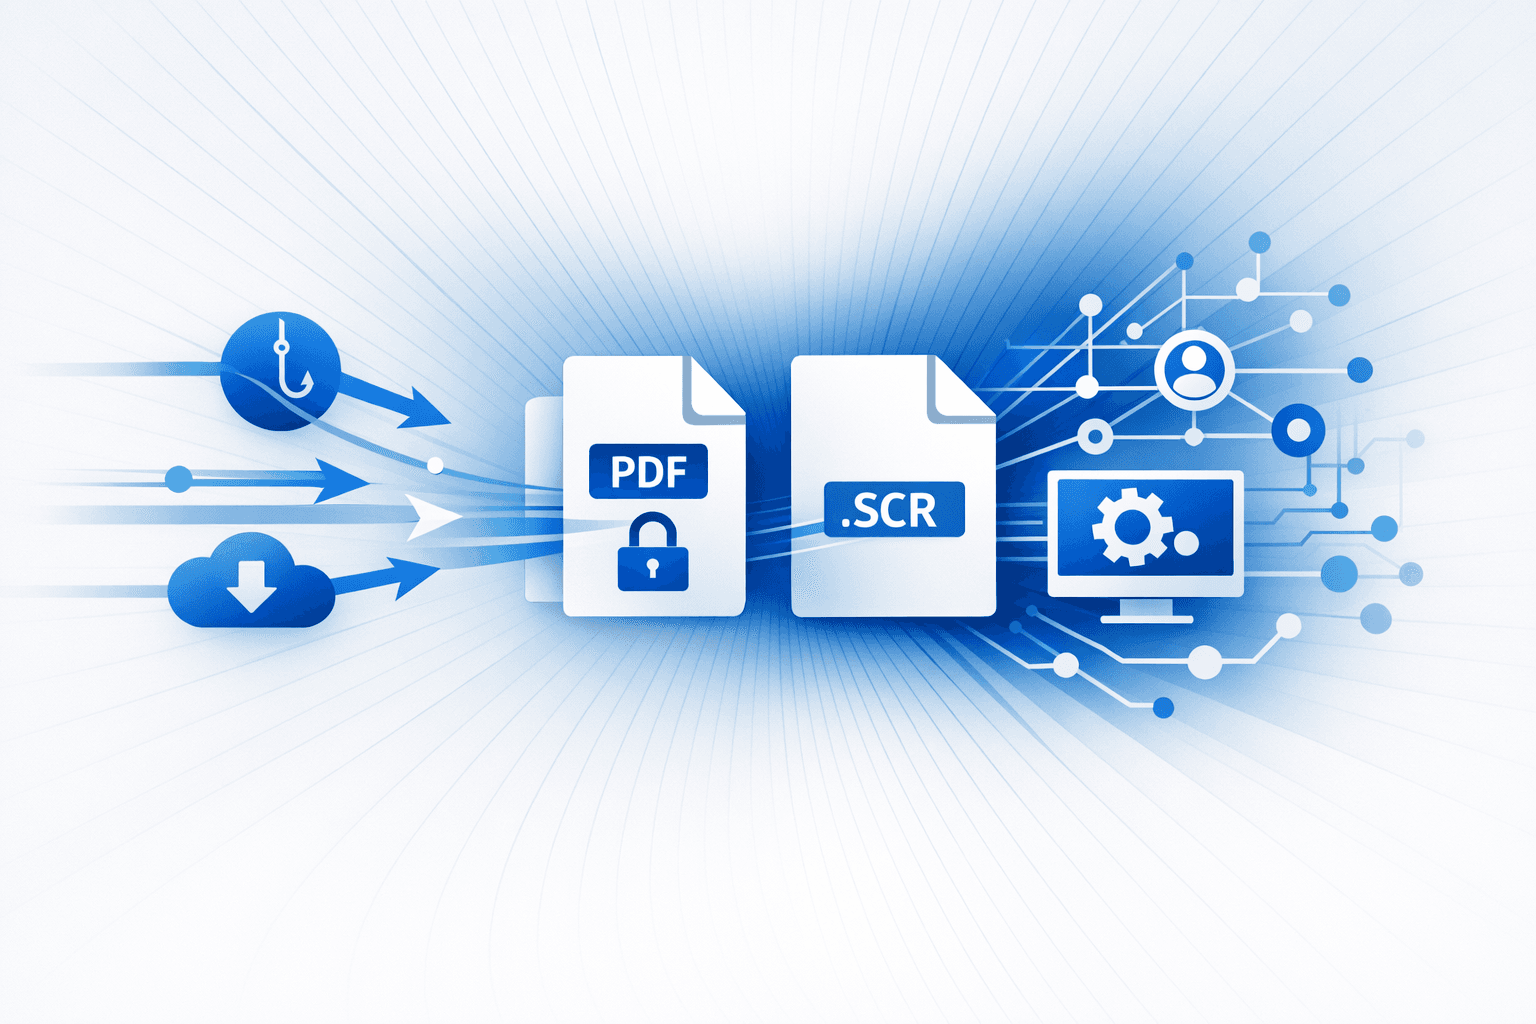
Threat actors have been observed using spearphishing lures and non-traditional attachment types—particularly Windows screensaver (.scr) executables—to trick users into running code that silently installs legitimate remote monitoring and management (RMM) agents (e.g., SimpleHelp). ReliaQuest research described business-themed filenames (e.g., InvoiceDetails.scr, ProjectSummary.scr) delivered via links hosted on legitimate cloud services (e.g., GoFile), with the .scr format helping bypass controls that don’t treat screensavers as executables. Once installed, the RMM tooling provides interactive remote access that can enable data theft, lateral movement, and follow-on payload deployment, including ransomware, while blending into normal IT administration traffic.
Separately, researchers also reported a spam operation using fake PDF attachments that display an error message and redirect victims to a lookalike Adobe Acrobat download flow, but instead installs trusted, digitally signed RMM software to establish persistent access. A different phishing campaign used a multi-stage PDF chain hosted on reputable infrastructure (e.g., Vercel Blob) to redirect victims to a credential-harvesting page and exfiltrate stolen data via a Telegram bot, emphasizing how attackers are increasingly abusing high-reputation cloud platforms and document-based lures to evade email and web filtering (including scenarios where the initial email contains no malicious link and can pass SPF/DKIM/DMARC checks).