Phishing Campaigns Abuse Digital Invites and Fake Meeting Pages to Steal Credentials and Deploy RMM Tools
Social Engineering & Fraud · 3 sources · Updated 4mo ago · First seen Feb 24, 2026
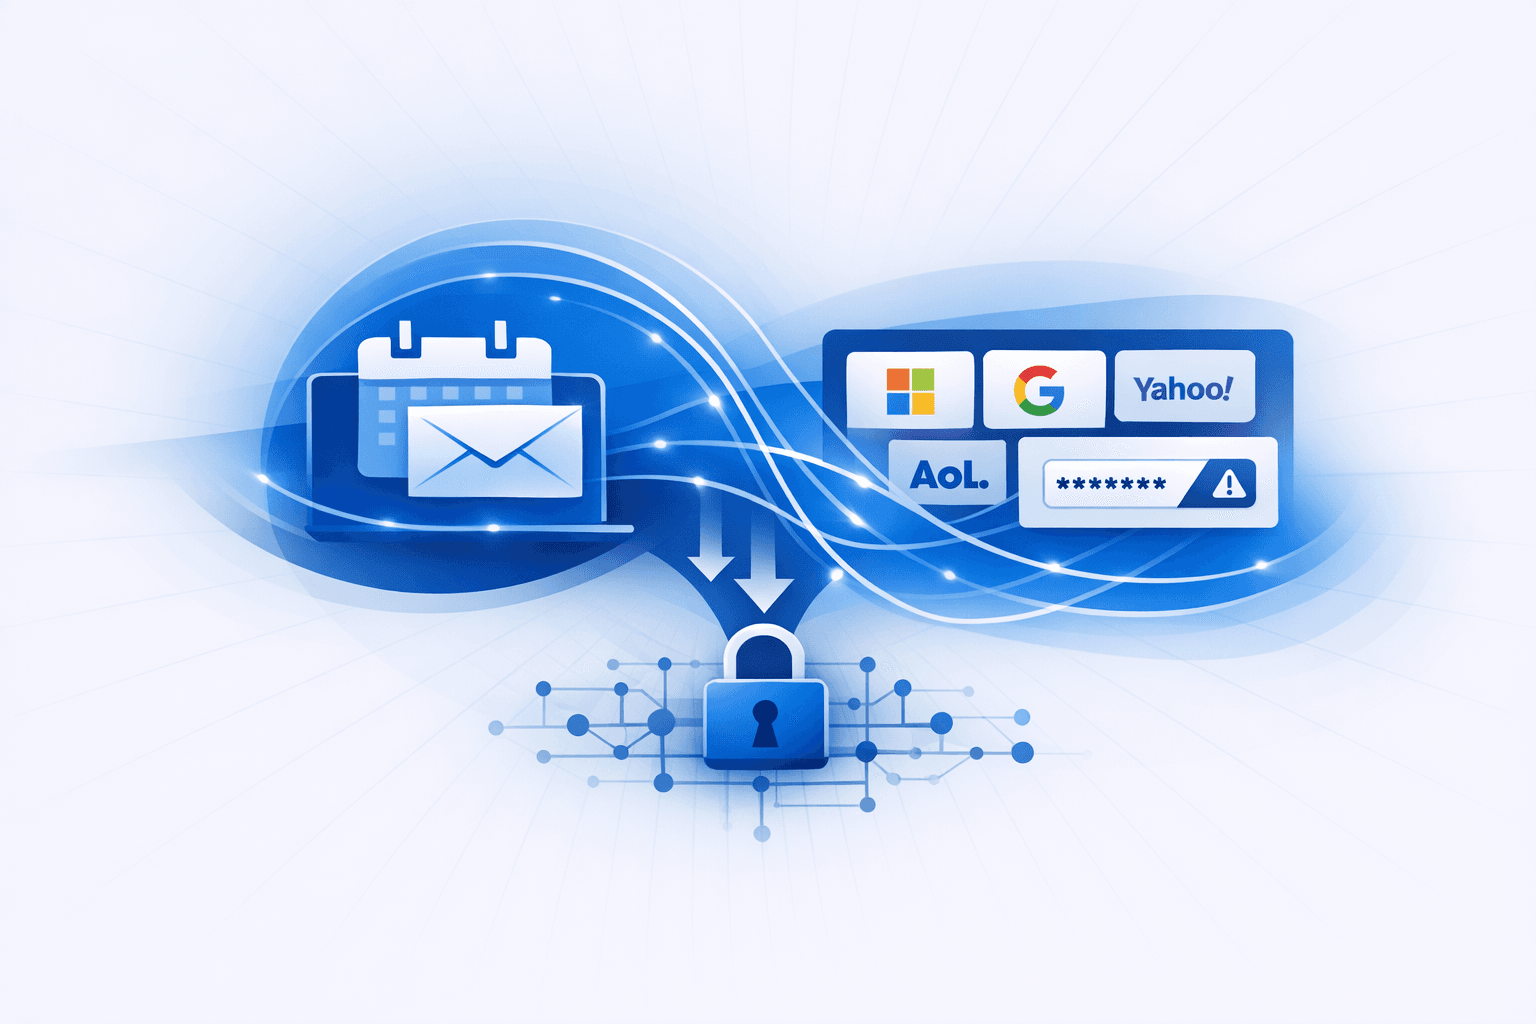
Threat actors are abusing the familiarity of digital invitation and meeting platforms to increase phishing success rates. Cofense reported malicious Punchbowl/Paperless Post-themed invitations that prompt recipients to “log in to view event details,” then redirect to phishing infrastructure offering branded sign-in options (e.g., Microsoft, Yahoo, AOL, Google, Dropbox) to harvest credentials. The phishing flow may solicit multiple credential sets by returning fake login errors and urging users to try alternate accounts; submitted credentials are exfiltrated to attacker-controlled domains, often leveraging newly registered domains to evade reputation-based defenses.
Separately, Netskope research (reported by KnowBe4) described fake video meeting invites for Zoom, Microsoft Teams, Google Meet, and similar services that lead to spoofed “join meeting” pages showing purported coworkers already on the call. Victims are instructed to install a required “update” to join; the payload is a digitally signed remote monitoring and management (RMM) tool such as Datto RMM, LogMeIn, or ScreenConnect, enabling remote access and potential follow-on activity including data theft or deployment of additional malware. The use of legitimate, signed RMM software can blend into normal enterprise traffic and may bypass controls where such tools are pre-approved.