Multi-stage malware delivery chains distributing XWorm and other RATs
Malware Intelligence · 2 sources · Updated 4mo ago · First seen Mar 6, 2026
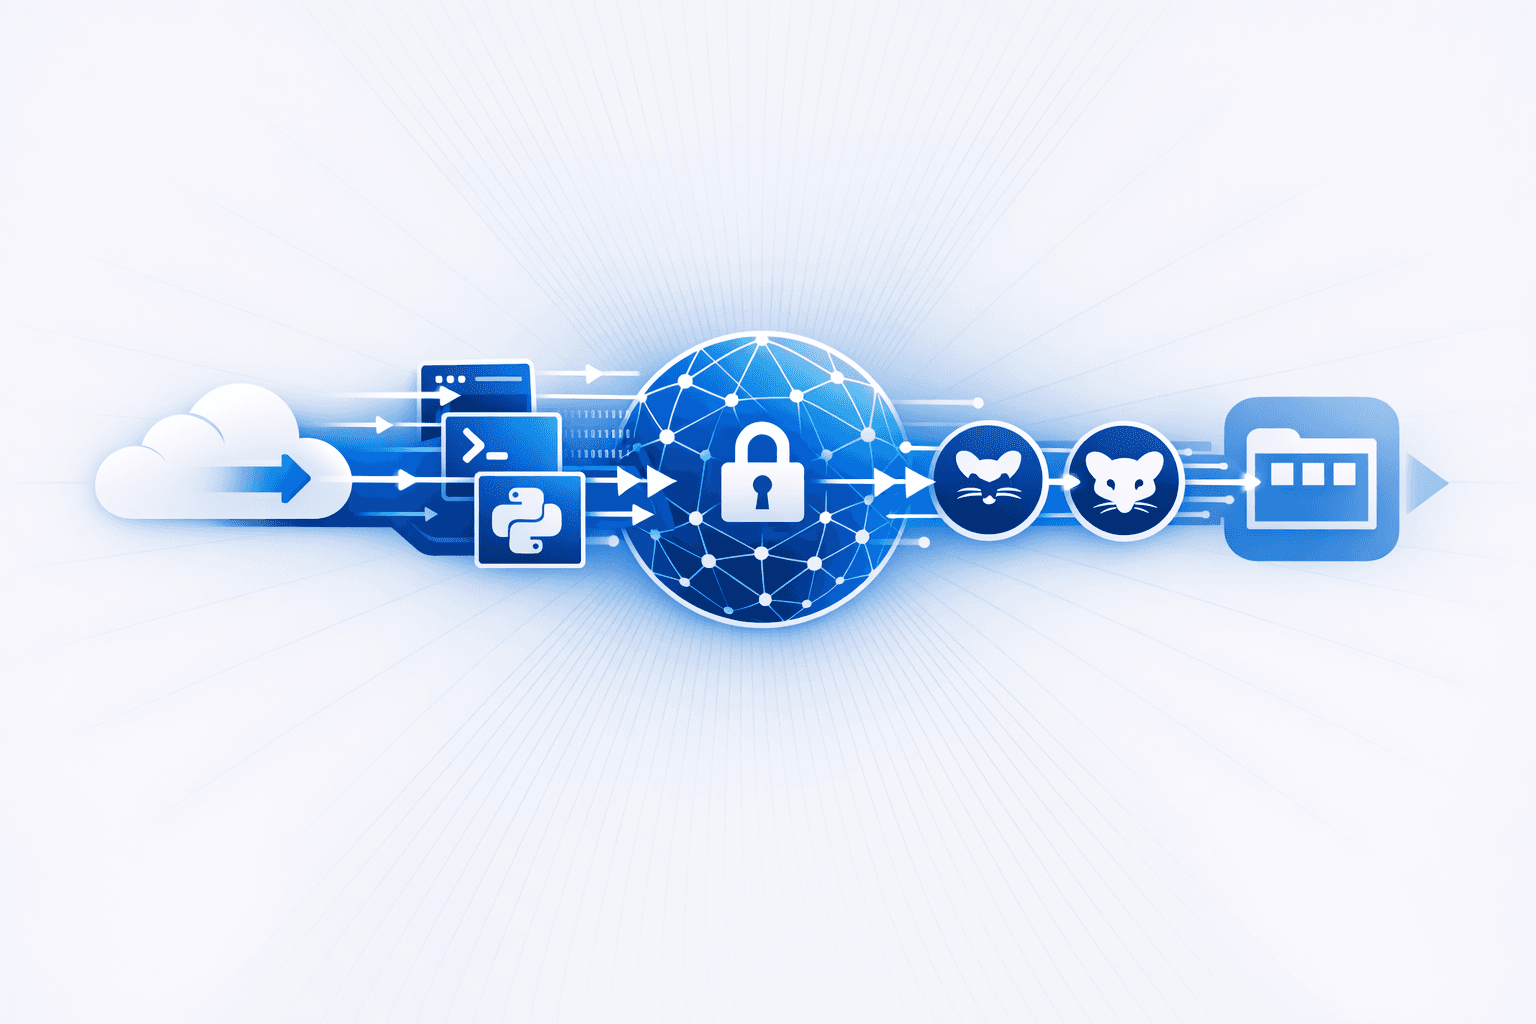
Researchers reported evolving multi-stage, script-heavy infection chains used to deliver remote access trojans, including XWorm, AsyncRAT, and Xeno RAT. Securonix described a campaign dubbed VOID#GEIST that starts from phishing-delivered batch scripts fetched from TryCloudflare infrastructure, then chains additional batch/PowerShell stages, deploys a legitimate embedded Python runtime, decrypts shellcode, and executes it filelessly by injecting into explorer.exe using Early Bird APC injection, reducing disk artifacts and making each stage appear benign in isolation.
Separately, SANS ISC documented another XWorm wave using an obfuscated JavaScript-to-PowerShell loader chain that drops a temporary PowerShell script (e.g., C:\Temp\ps_...ps1), decodes additional in-memory PowerShell, and uses a DLL exporting ProcessHollowing to inject the XWorm client into a .NET compiler process. The write-up included configuration and IOCs such as a C2 endpoint 204[.]10[.]160[.]190:7003, mutex Cqu1F0NxohroKG5U, and multiple SHA-256 hashes for the JavaScript, PowerShell, DLL loader, and XWorm payload, indicating continued high-volume distribution with frequently changing delivery techniques.