HR-targeted fake resume campaign delivers malware with EDR-killer module
Attack Tradecraft · 4 sources · Updated 4mo ago · First seen Mar 10, 2026
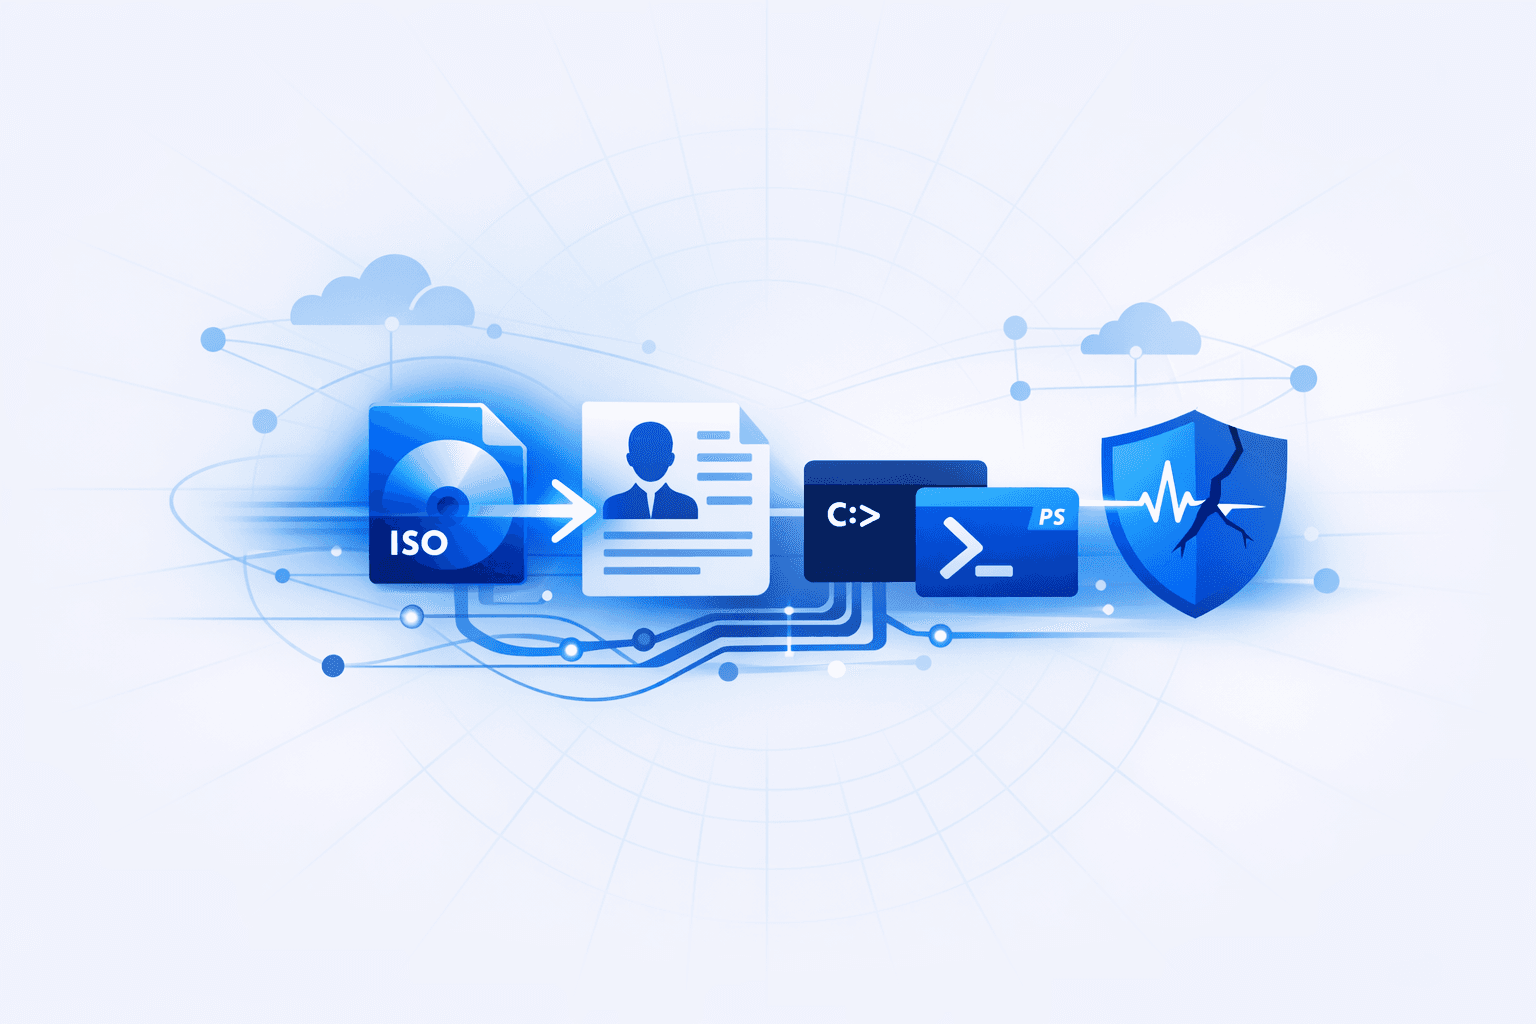
Aryaka researchers reported a Russian-speaking threat actor targeting corporate HR teams and recruiters with fake job applications that deliver malware via a resume-themed ISO file, likely distributed through spam and hosted on common cloud storage services. When the ISO is mounted, victims are tricked into executing a disguised Windows shortcut (.lnk) that launches cmd/PowerShell, extracts hidden data from an image file, and runs additional PowerShell in memory. The chain then downloads a decoy archive (e.g., SumatraPDF.zip) from attacker-controlled domains (including resumebuilders.us and thresumebuilder.com), leveraging DLL sideloading (e.g., SumatraPDF.exe loading DWrite.dll) to execute the next-stage payload while blending into normal user activity.
A key capability in the operation is an EDR/AV “killer” component (described as BlackSanta) intended to disable endpoint defenses before follow-on actions such as host profiling and data theft, with much of the activity occurring in memory to reduce forensic artifacts. Aryaka assessed the campaign as low-noise and potentially long-running (over a year), but noted limited telemetry on overall prevalence; the tradecraft is designed to exploit routine hiring workflows where recruiters rapidly open candidate materials and may not scrutinize ISO-mounted content or shortcut execution.