AiTM Phishing Campaign Hijacking AWS Console Sessions via Typosquatted Domains
Social Engineering & Fraud · 2 sources · Updated 4mo ago · First seen Mar 10, 2026
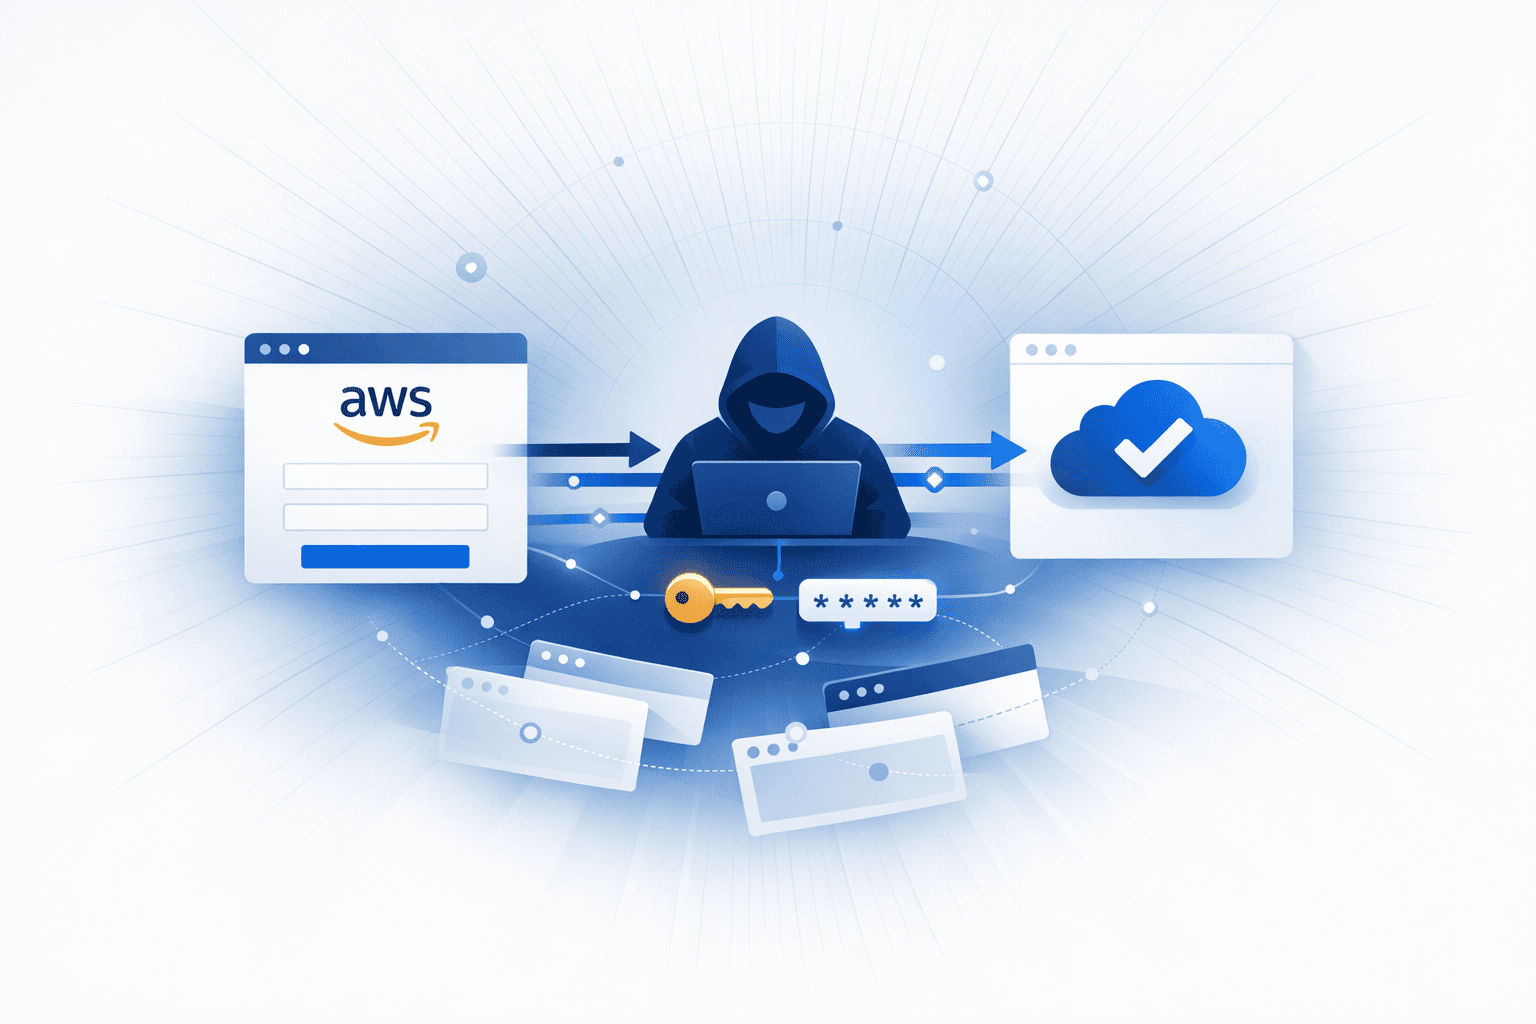
Datadog Security Labs reported an active adversary-in-the-middle (AiTM) phishing campaign targeting AWS Management Console users with high-fidelity cloned login pages hosted on typosquatted domains. The kit acts as a live proxy to the legitimate AWS sign-in flow, relaying authentication in real time to validate credentials and capture session material (and likely MFA/OTP codes) before redirecting victims, enabling rapid post-compromise access to cloud environments.
In an observed case, the threat actor accessed a compromised AWS account within ~20 minutes of credential submission, with console access originating from 185.209.196.132 (identified as a Mullvad VPN egress). Datadog identified two active infrastructure clusters and a third related domain, including cloud-recovery[.]net (IP 178.16.54[.]142), cloud-policy[.]com (IP 69.67.172[.]30), and cloud-recovery[.]us, with shared registrar metadata (Registrar ID 3254, CNOBIN INFORMATION TECHNOLOGY LIMITED) and signs of rapid infrastructure rotation. Reporting emphasized the activity is credential theft rather than exploitation of an AWS vulnerability or abuse of AWS infrastructure, and that the lure impersonates an “AWS Organization Security” alert with a likely spoofed sender noreply@security[.]aws.