Hardware-Level Android Chip Vulnerabilities Enable Device Compromise
Active Exploitation · 3 sources · Updated 4mo ago · First seen Mar 11, 2026
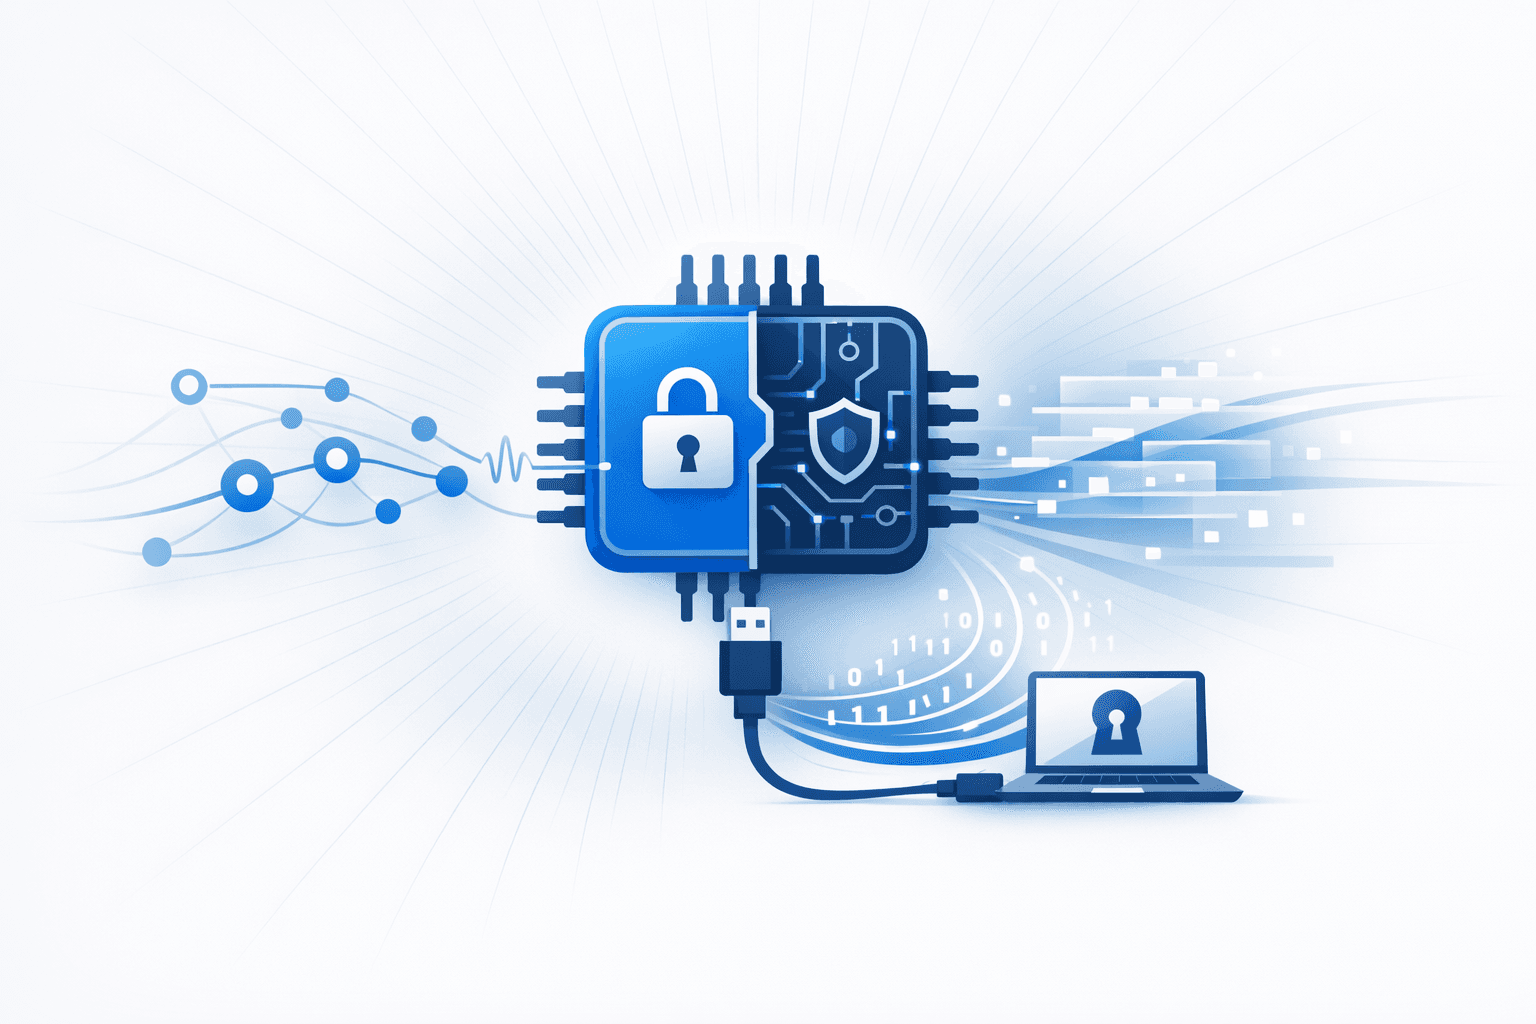
Security researchers and vendors reported hardware/firmware-level vulnerabilities in Android chip components that can enable deep device compromise beyond typical app-layer defenses. Ledger’s Donjon research described a flaw involving MediaTek chip boot-chain behavior and Trustonic’s trusted execution environment (TEE) that allowed rapid physical compromise: by connecting an affected phone to a laptop over USB, attackers could allegedly brute-force the PIN, decrypt storage, and extract sensitive data including messages and cryptocurrency wallet seed phrases (e.g., Kraken Wallet, Phantom). The researchers estimated the affected MediaTek chips appear in roughly one-quarter of Android phones, disproportionately in lower-cost devices.
Separately, Zimperium reported active exploitation of a Qualcomm graphics zero-day (CVE-2026-21385) in targeted Android attacks, describing a memory-corruption condition that could enable code execution or unauthorized access across “hundreds” of Qualcomm chipsets. A ZDNET article on Android’s Repair Mode primarily provides user guidance and anecdotal troubleshooting around a buggy March update/SIM recognition issue; it does not substantively address the chip-level vulnerabilities described in the other reporting and is best treated as tangential consumer advice rather than incident or vulnerability intelligence.