Malicious LNK Campaign Used GitHub and PowerShell for Fileless Malware Delivery
Malware Intelligence · 3 sources · Updated 4mo ago · First seen May 25, 2026
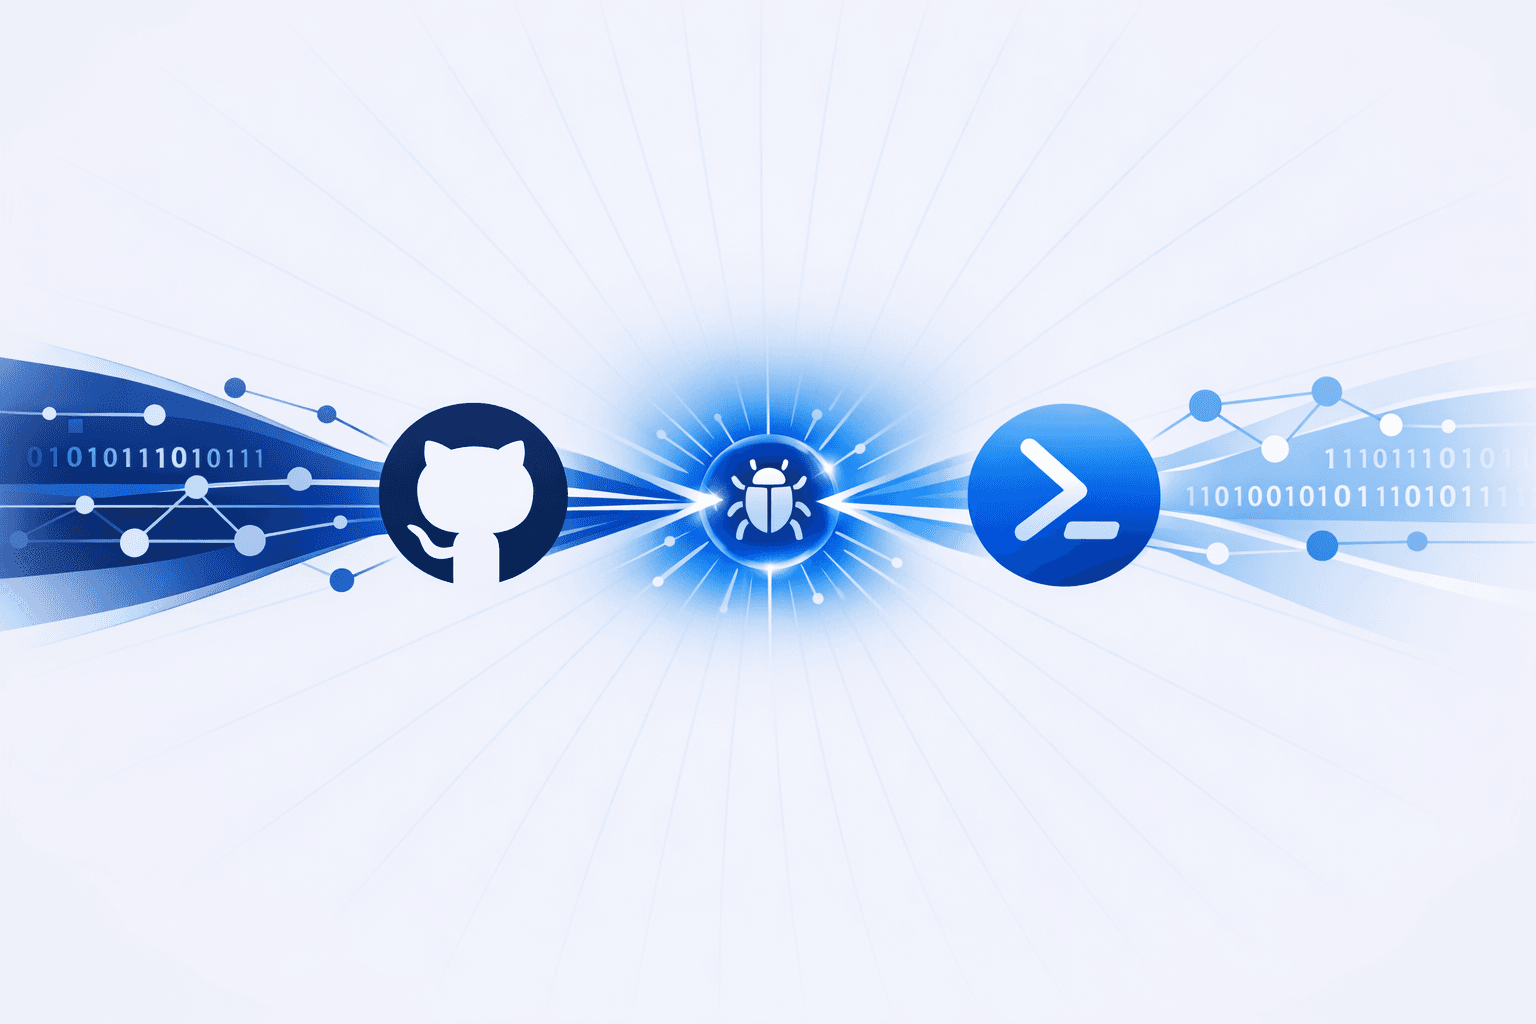
Attackers distributed malicious Windows shortcut (.LNK) files disguised as privacy consent forms and other work-related documents, tricking users into launching obfuscated PowerShell that fetched additional payloads from external infrastructure. Reporting indicates GitHub was used as a covert stage in the infection chain, helping operators blend malicious downloads and command retrieval into legitimate web traffic while keeping much of the activity fileless and in memory.
Once executed, the malware created downloader and loader scripts, established persistence through Windows Task Scheduler, opened decoy documents to reduce suspicion, and deleted the original shortcut to limit forensic artifacts. Observed follow-on payloads included an information stealer and a backdoor loader that decrypted and loaded malware into memory; the theft activity gathered host, security product, network, IP, drive, file, and process data, with behavior resembling prior Kimsuky-linked operations.