Attackers Abuse QEMU to Create Covert Network Tunnels Inside Enterprise Networks
Attack Tradecraft · 2 sources · Updated 4mo ago · First seen May 25, 2026
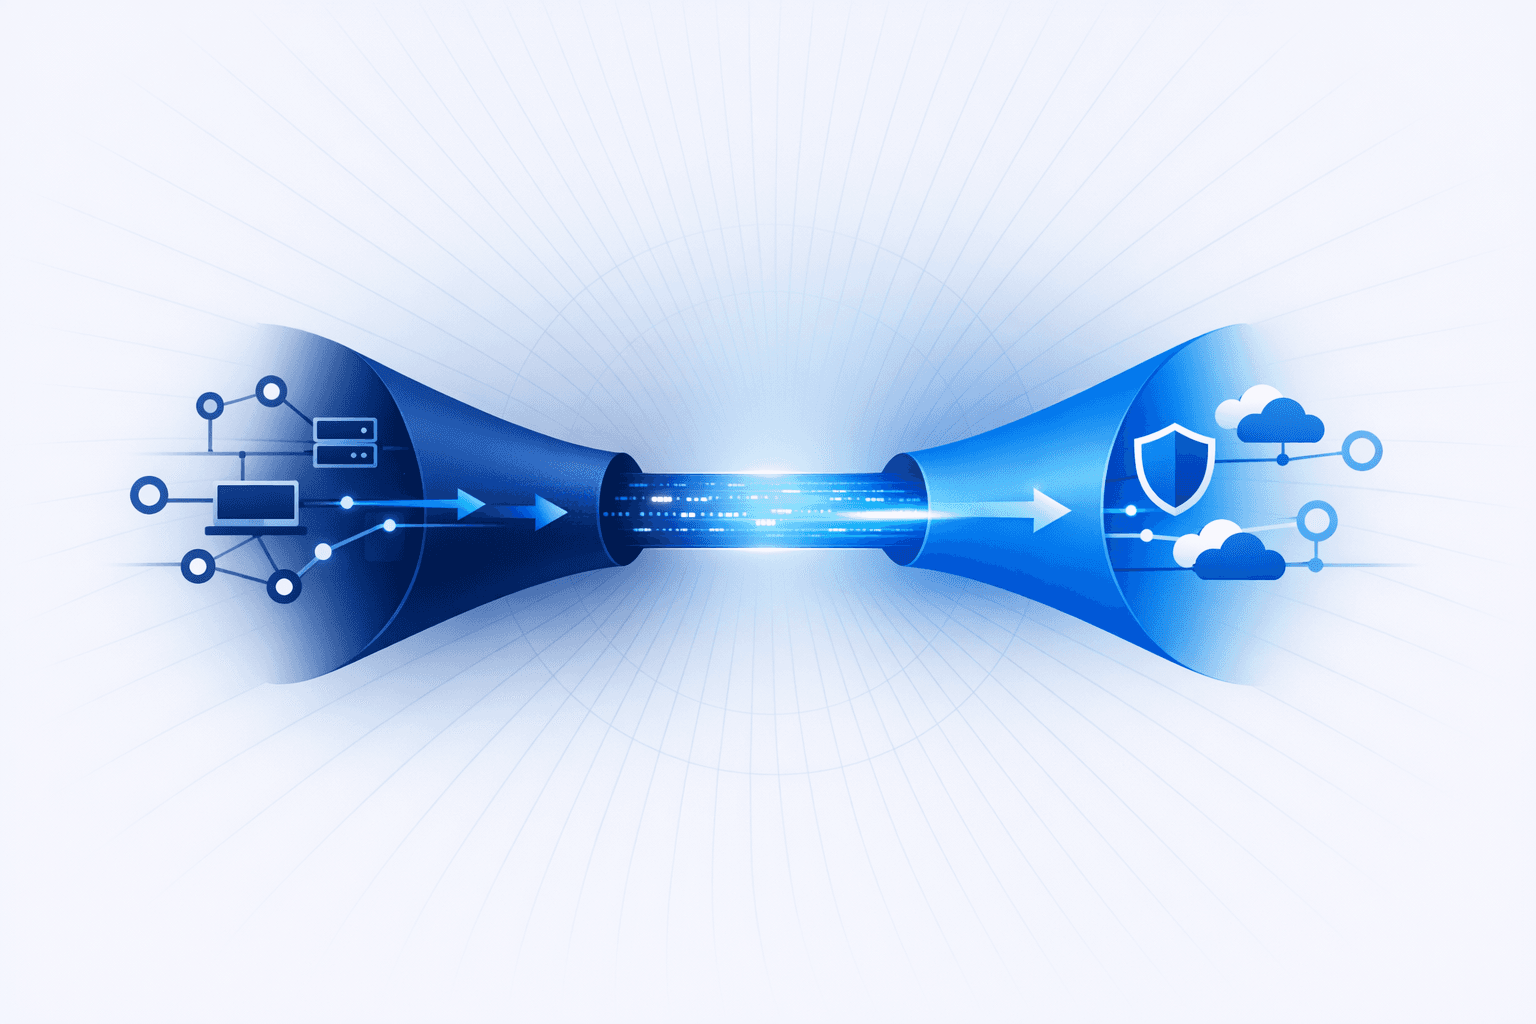
Kaspersky reported an intrusion at a large enterprise in which attackers repurposed the open-source hypervisor QEMU as a stealthy tunneling tool to move traffic across segmented systems. The operators launched a minimal virtual machine with about 1 MB of RAM, no disk image, and no graphical interface, then used QEMU to create virtual network interfaces and a socket-based network device that forwarded traffic from an internal host to attacker-controlled infrastructure. The tunnel linked a victim system without direct internet access to a pivot host that could reach the internet, and then on to a cloud server hosting a Kali Linux virtual machine.
The activity stood out because defenders more commonly watch for tunneling utilities such as FRP, ngrok, and Cloudflare Tunnel, while QEMU can blend into legitimate virtualization activity and attract less scrutiny. In the same compromise, the attackers also used Angry IP Scanner for internal reconnaissance and mimikatz for credential theft, showing how legitimate administration and offensive tools were combined for lateral movement and persistence. The reporting highlights the need for layered detection across endpoints and networks, including monitoring for unusual QEMU execution, unexpected virtual interfaces, and traffic paths that bridge isolated network segments.