DDrop Hardware Attack Undermines Intel TDX and AMD SEV-SNP Confidential VMs
Vulnerability Disclosure · 13 sources · Updated 2mo ago · First seen Sep 14, 2026
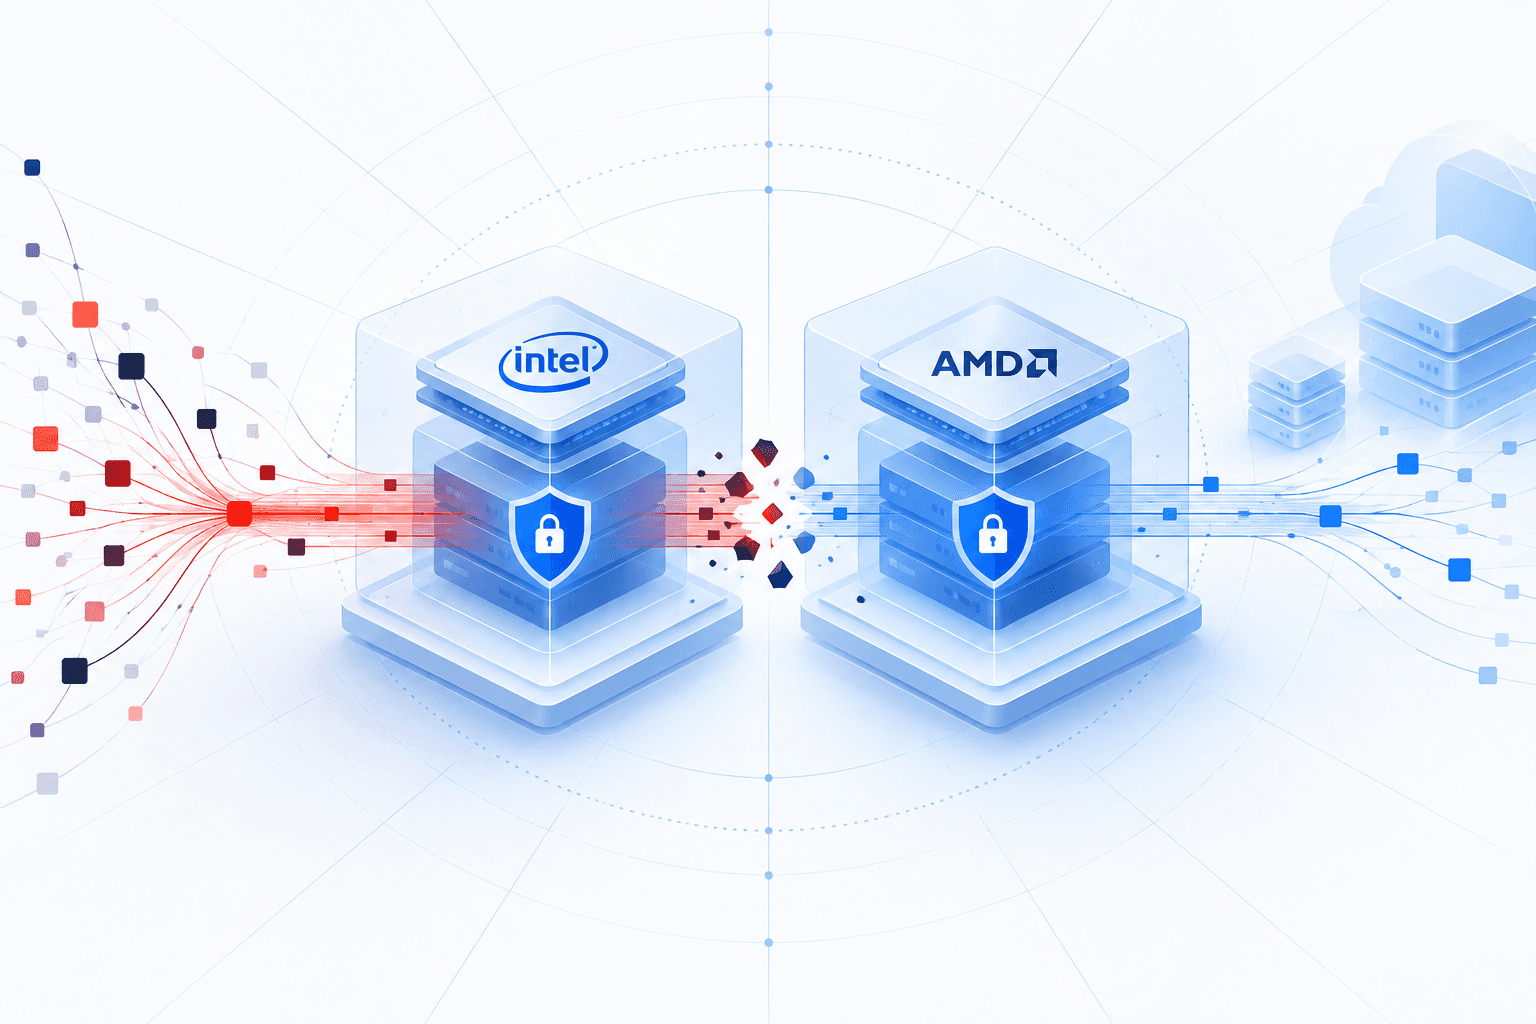
Researchers disclosed DDrop, an active DDR5 hardware-interposer attack that drops selected memory writes so stale encrypted memory values can be accepted as current. The flaw affects Intel TDX, Intel Scalable SGX, and AMD SEV-SNP because their scalable memory-encryption architectures do not provide memory-freshness protection. Demonstrated impacts include protected-VM memory disclosure, activation of Intel TDX debug mode, and forgery of launch-attestation measurements; on AMD SEV-SNP, researchers copied data between victim pages through page relocation.
Exploitation requires an attacker to already control software on the target and obtain brief physical access to install a sub-$200 interposer, and no exploitation beyond laboratory testing has been reported. Organizations using confidential-computing workloads, including confidential VMs, should assess physical-access controls and attestation trust assumptions: the issue is architectural, has no straightforward software patch, and may require configuration or software mitigations that increase attack difficulty.