Compromised Thai College Domain Redirects Google Users to Illegal Casino
Social Engineering & Fraud · 2 sources · Updated 2mo ago · First seen Sep 17, 2026
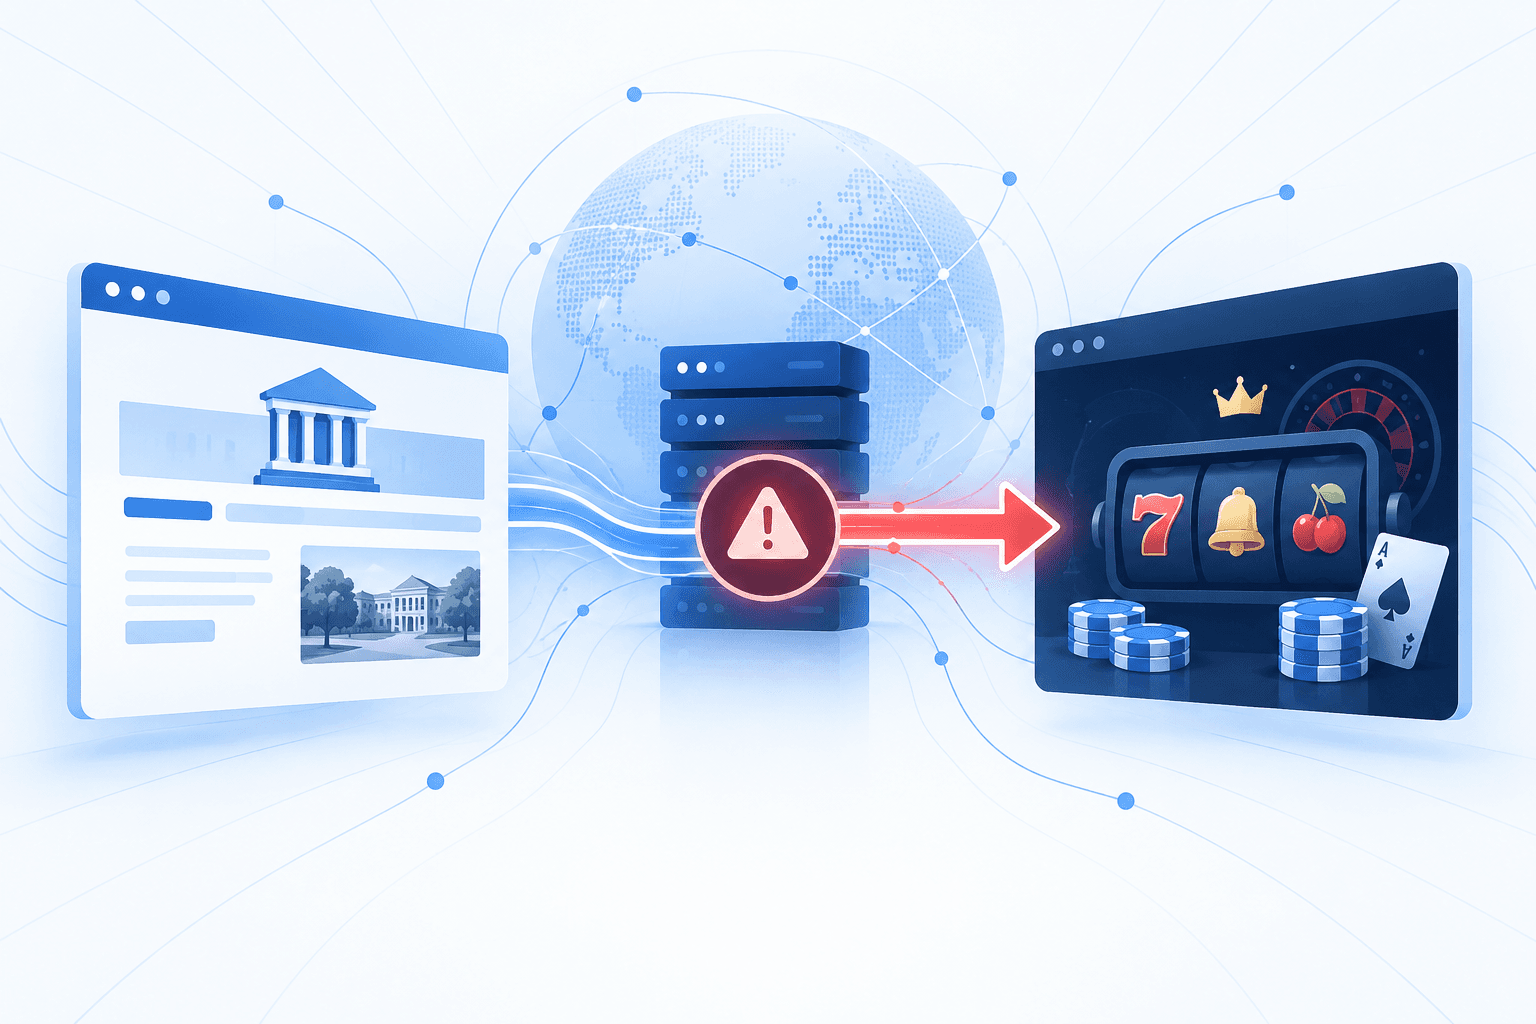
Attackers compromised the Thai educational domain km.chpc.ac.th, injected a casino-themed page, and leveraged the institution’s established search reputation to rank the page for targeted Google queries. Users who selected the Google result were routed through the legitimate-but-compromised college site before being redirected to an illegal online gambling operation.
ADEX described the technique as domain borrowing: abusing trusted government, educational, and country-code domains instead of relying on overtly malicious infrastructure. The Google-result-to-compromised-domain redirect chain can evade conventional advertising review and cloaking detection without custom cloaking code; defenders should inspect complete redirect paths and treat restricted institutional domains appearing in them as indicators requiring investigation and campaign reassessment.