Registry-Resident PowerShell Chain Deploys In-Memory XMRig Miner
Attack Tradecraft · 5 sources · Updated 2mo ago · First seen Sep 18, 2026
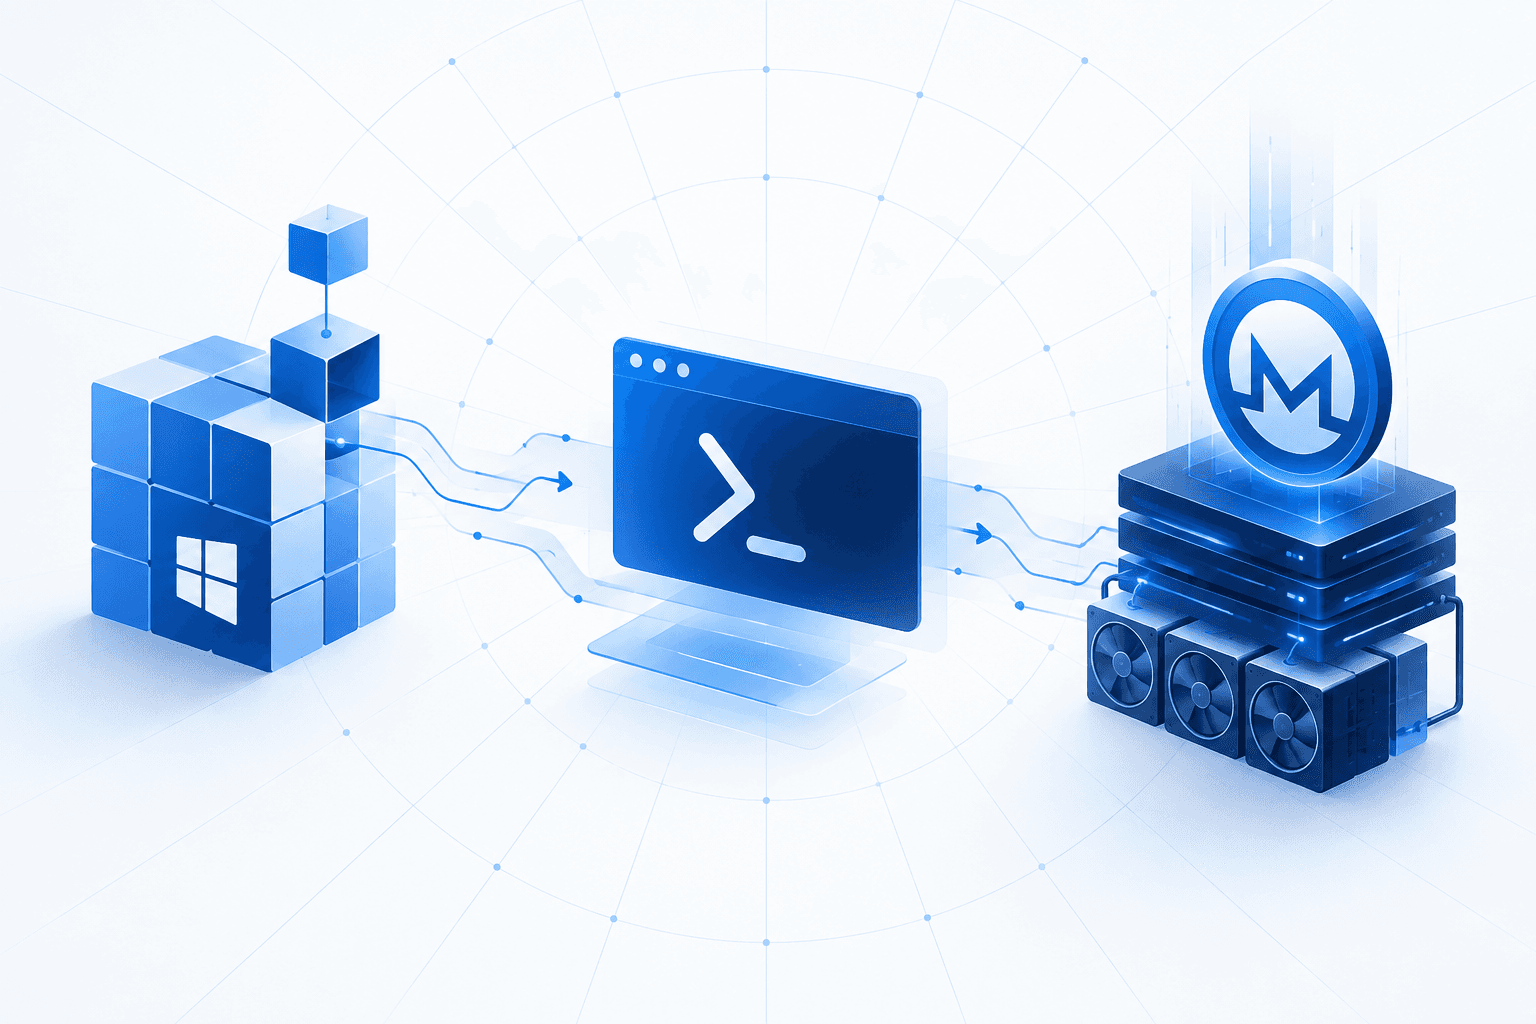
Researchers identified a multi-stage, fileless-leaning Windows malware chain that stores PowerShell payloads in the Registry and hides later stages in DNS TXT records, PNG images, ZIP archives, and WAV files. The malware reconstructs .NET assemblies and loads an XMRig cryptocurrency miner directly into memory, configured for RandomX mining with up to 40 CPU threads and a TLS-connected mining pool.
The infection establishes persistence through hidden scheduled tasks and a permanent WMI event subscription, while attempting to weaken Microsoft Defender controls and erase PowerShell history. It uses DNS-over-HTTPS via Google DNS alongside HTTP/HTTPS communications for command-and-control and host identification; researchers warned that this active C2 channel could also deliver commands or payloads beyond cryptomining.