Mallory
← Back to News
identity-impersonation-fraudendpoint-security-bypass

Apple Adds On-Device Impersonation Scam Detection to iOS 27

Social Engineering & Fraud · 2 sources · Updated 2mo ago · First seen Sep 21, 2026
Apple Adds On-Device Impersonation Scam Detection to iOS 27

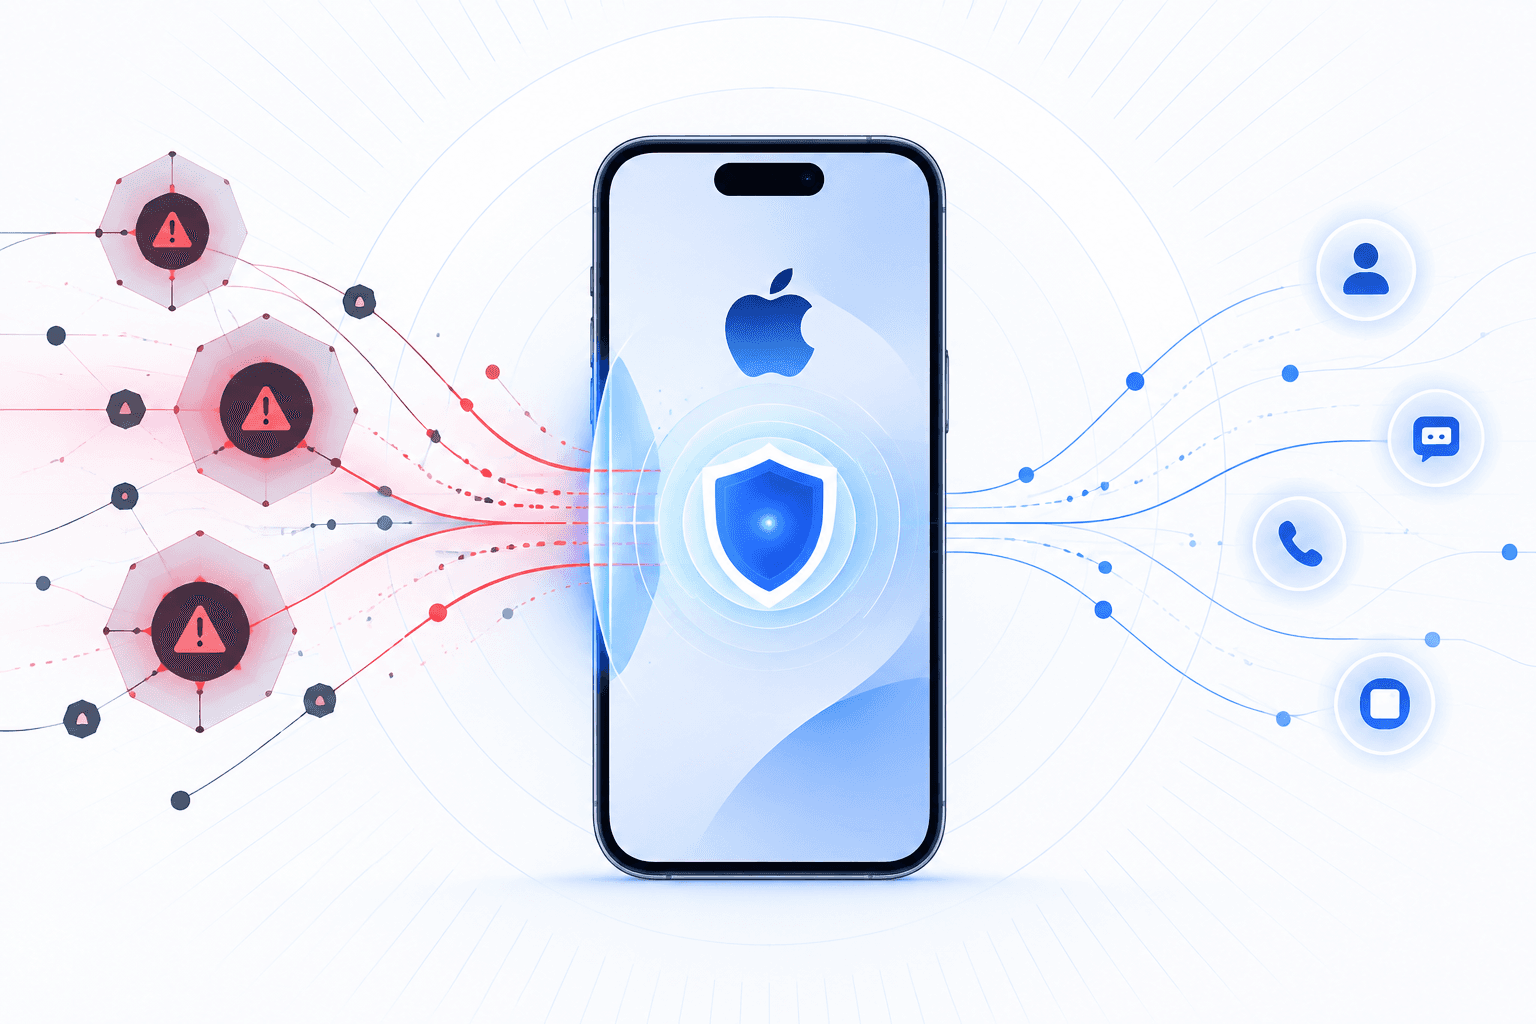
Apple introduced Impersonation Risk Detection in iOS 27 and iPadOS 27, an opt-in privacy feature that helps participating apps identify actions potentially tied to active social-engineering or impersonation scams. The operating system assesses device-use, Apple Account, interaction, timing, contextual, and limited sensor-data signals locally, while excluding the contents of Photos, Messages, and Mail.

Supported apps receive only an unknown, medium, or high risk assessment rather than the underlying data. Developers can use that result to display warnings, delay sensitive transactions, or require identity verification before actions such as account-security changes or large payments. Users can control global and per-app access in Privacy & Security settings, though setting changes may take up to 24 hours to take effect; effectiveness depends on both user opt-in and app adoption.
Is your org in this campaign?Get the infrastructure and lures behind it.
Hunt this campaign
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

1 event
  1. Reported Sep 21, 20262mo ago

    Apple introduces Impersonation Risk Detection in iOS 27 and iPadOS 27

    Apple introduced an opt-in, on-device feature enabling supported apps to request risk assessments for security-sensitive actions that may be associated with social-engineering impersonation scams. Apps receive only an unknown, medium, or high risk level and can independently warn users, require verification, or delay an action.

    iOS 27 Adds Impersonation Risk Detection to Help Protect Against Social Engineering Scams - gHacks Tech News
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.

Open in app →

Affected products

2 linked
IpadosIos

Organizations

1 linked
Apple
Do you run this?Get the infrastructure, lures, and IOCs behind this campaign, ready to push into your email and identity stack.
Hunt This Campaign
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.