Developer Documentation Placeholder Domain Delivers Windows ClickFix Malware
Social Engineering & Fraud · 6 sources · Updated 2mo ago · First seen May 2, 2026
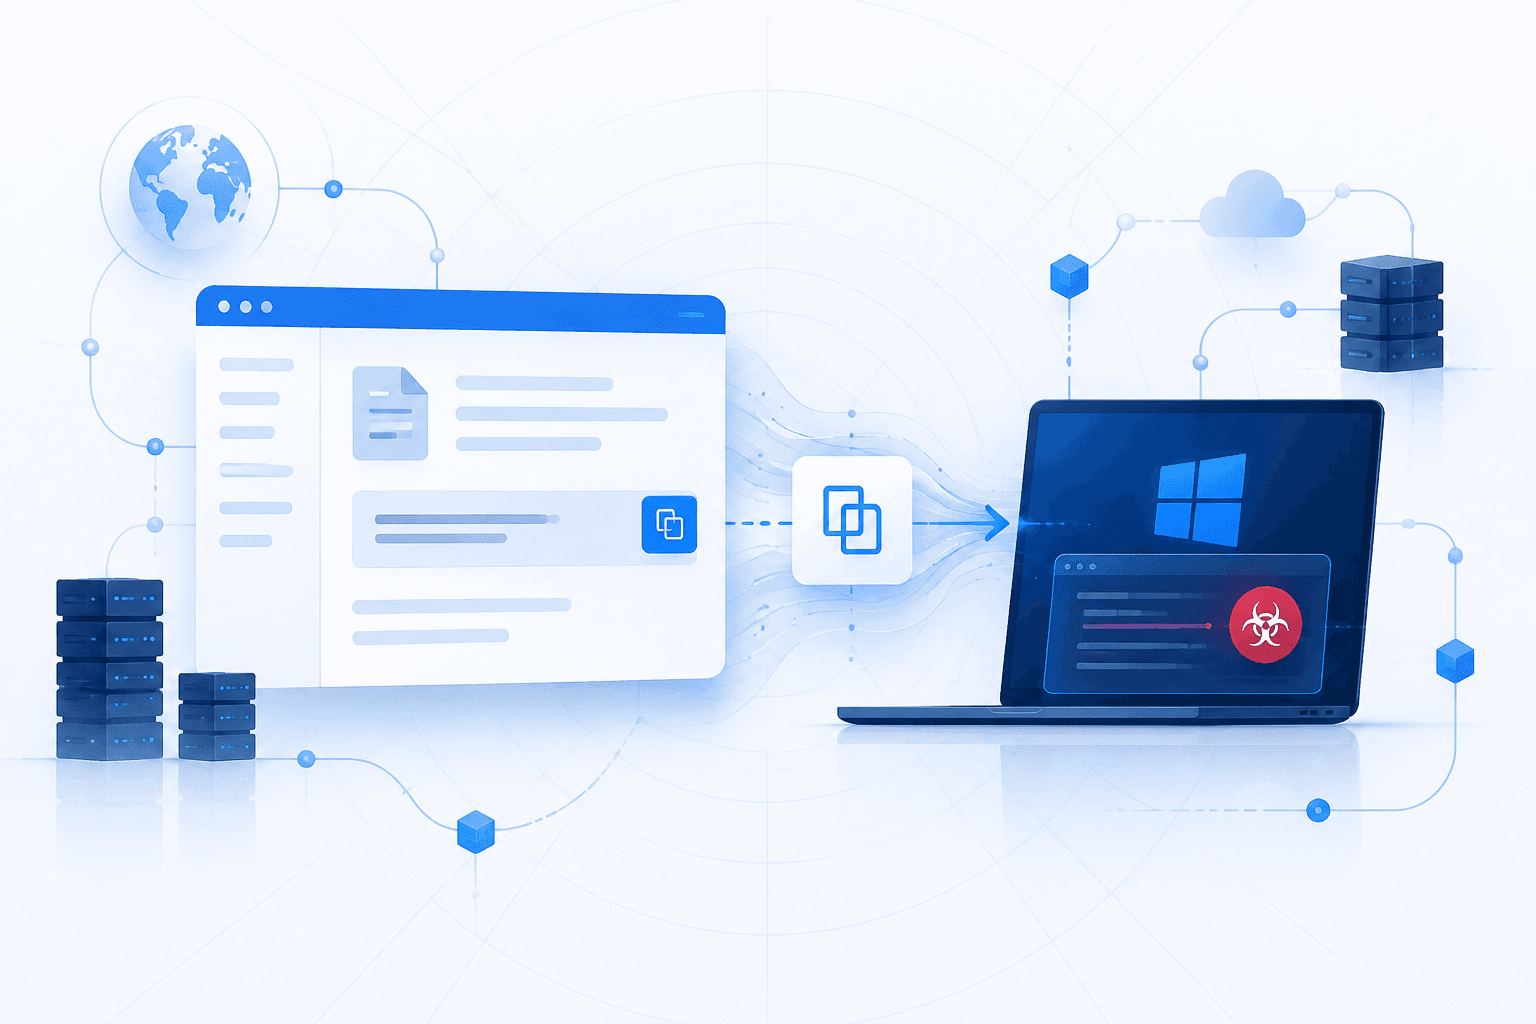
The registrant-controlled third-party[.]com domain, widely used as a placeholder in developer documentation, is serving a Windows-targeted ClickFix lure disguised as a Cloudflare verification page. Windows visitors are instructed to paste and run a clipboard-poisoned PowerShell command that reconstructs a URL at elxxvvx[.]xyz and retrieves a second-stage script; analysis indicates the script downloaded an archive and attempted to execute draw.io.exe. The site has delivered the malicious workflow since at least June 2026, while macOS and Linux visitors receive error messages or benign content.
More than 1,700 public GitHub repositories reference the domain, including AI-agent skill and MCP-server documentation, creating a risk that users may follow a formerly innocuous example link into the attack flow. There is no evidence that repositories containing the placeholder were compromised or that copied links have resulted in confirmed executions. Researchers also identified 13 other non-reserved placeholder domains, including yoursite[.]com and your-domain[.]com, serving selectively targeted macOS scareware and investment-fraud pages.