Fake Cloudflare ClickFix Pages Deliver Psychedelic Stealer to Ukrainian Users
Malware Intelligence · 5 sources · Updated 1mo ago · First seen Sep 24, 2026
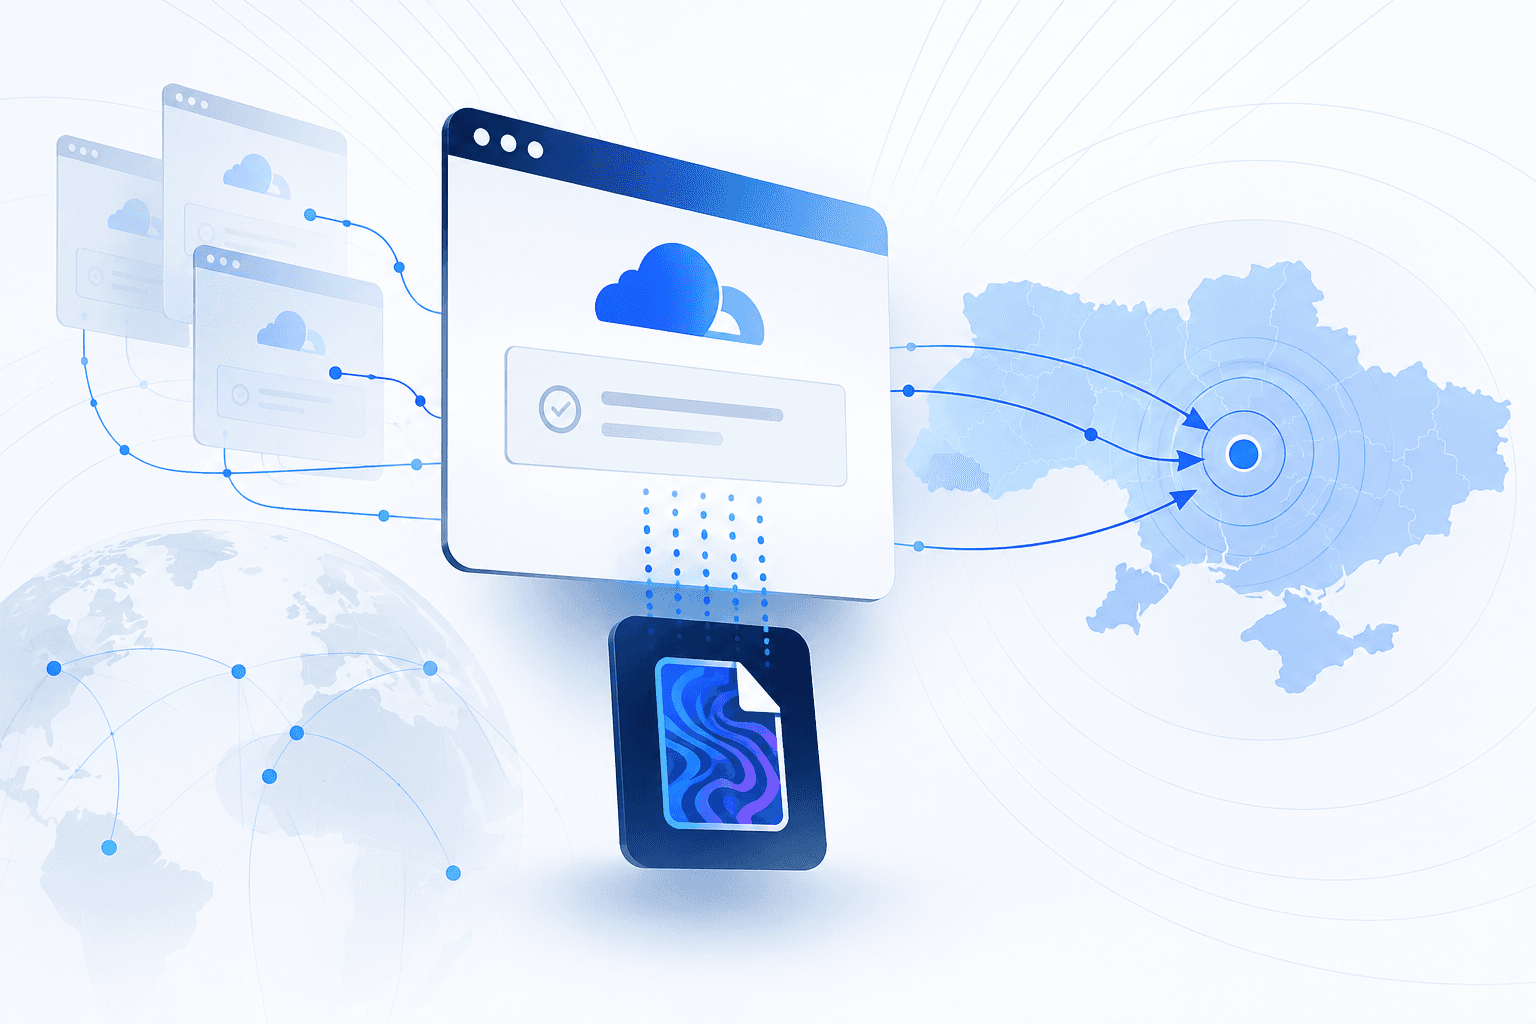
An ongoing ClickFix campaign has compromised legitimate Ukrainian business websites and injected iframes that display a Ukrainian-language counterfeit Cloudflare verification page. The page copies an msiexec command to a visitor’s clipboard and instructs them to paste it into Windows Run, downloading an MSI installer for the previously unidentified Psychedelic Stealer.
Psychedelic Stealer targets browser passwords, browser-associated tokens, and cryptocurrency-wallet data, creates scheduled-task persistence, deploys browser components, and polls command-and-control infrastructure for further instructions. An exposed Russian-branded lure-management panel logged 557 interactions across 32 countries—446 in Ukraine—although those figures do not confirm execution or compromise. Arctic Wolf Labs has not attributed the operation, while noting that Russian-language artifacts suggest but do not establish Russian involvement.