Mallory
← Back to News
critical-infrastructure-threatoperational-disruption

Study Identifies Coordinated GPS Spoofing Across Global Shipping Routes

Sector Threat Intelligence · 2 sources · Updated 2mo ago · First seen Sep 30, 2026
Study Identifies Coordinated GPS Spoofing Across Global Shipping Routes

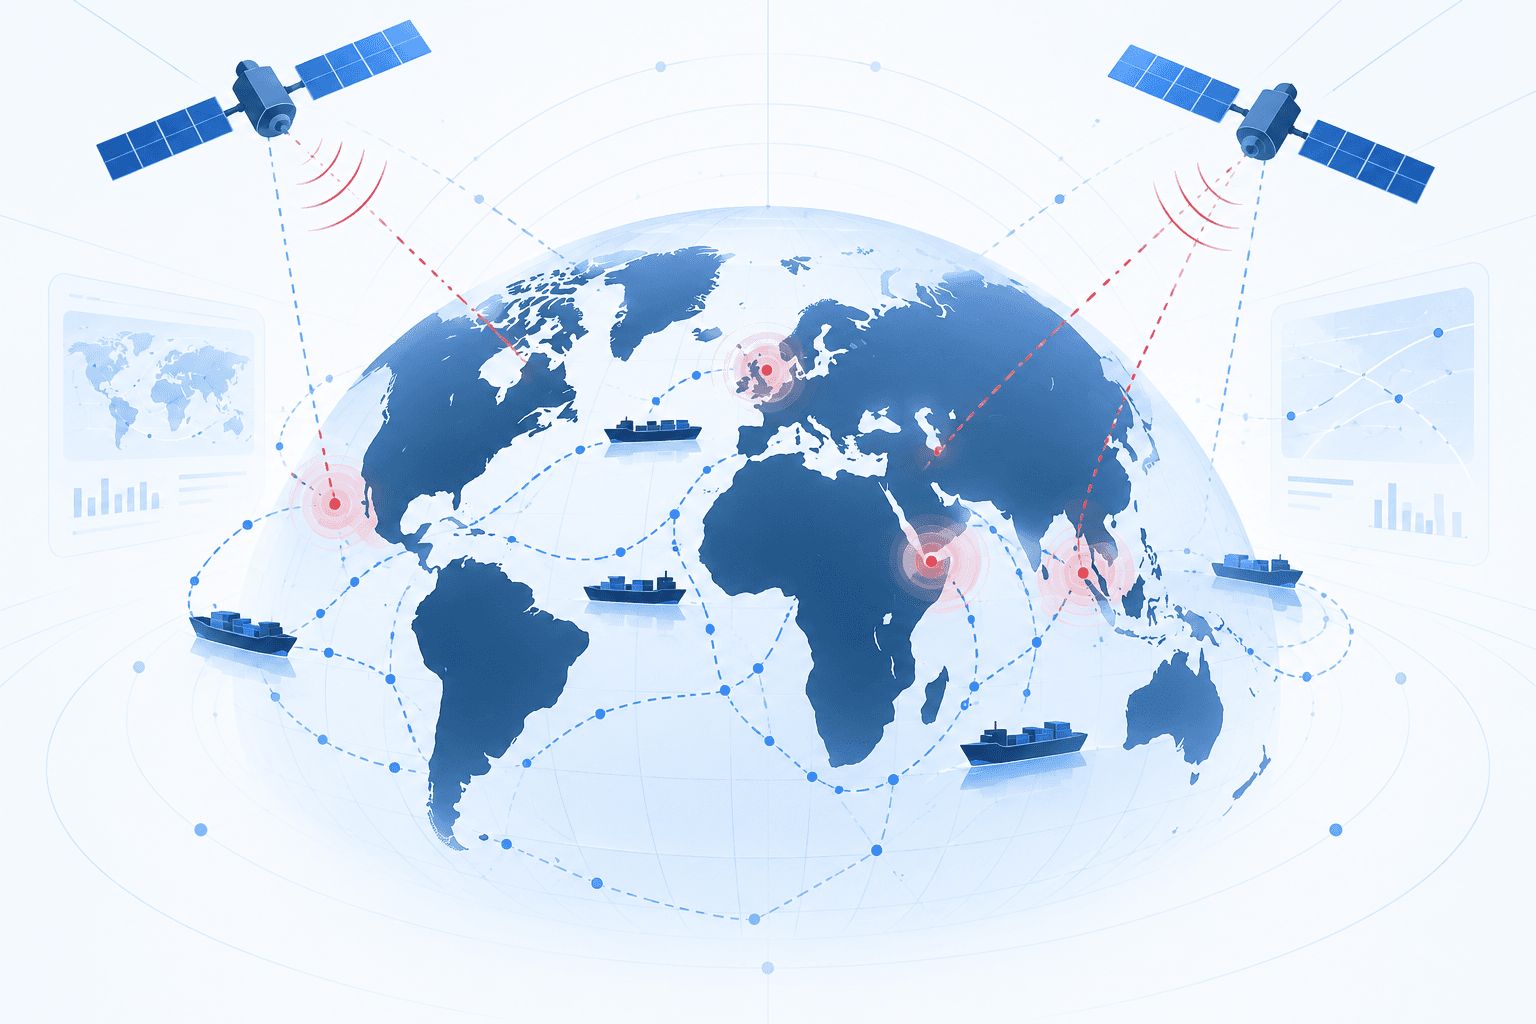
A Georgia Institute of Technology study of Automatic Identification System (AIS) broadcasts from more than 367,000 vessels identified 31 persistent maritime navigation-anomaly hotspots between late November 2024 and early February 2025. Researchers found strong or corroborated evidence of coordinated, regional GPS spoofing in at least 22 locations, documenting 17,936 anomalous episodes affecting 2,663 vessels and more than 31,000 hours of physically implausible or correlated vessel movements.

The activity appeared in heavily traveled waterways and showed geographic and temporal alignment with regional conflicts and sanctions, including persistent disruption in the Red Sea and Strait of Hormuz. Red Sea anomalies near Port Sudan in January 2025 resembled conditions associated with the May 2025 grounding of the container ship MSC Antonia. The researchers cautioned that AIS analysis cannot identify the transmitter, operator, or spoofing technology responsible and likely misses short-lived, localized, and single-vessel incidents.
Who's targeting your sector?See the actors and campaigns active against you right now.
See sector threats
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

5 events · Dec 31, 2024 – Sep 29, 2026
  1. Sep 29, 20262mo ago

    Researchers publish large-scale maritime GPS spoofing study

    Georgia Institute of Technology researchers published a study of AIS data from more than 367,000 vessels collected from late 2024 through early 2025. It identified 17,936 anomalous navigation episodes, 31 persistent hotspots, and strong or corroborated evidence of large-area GPS spoofing in 22 zones.

    367,000-Ship Study Finds Global GPS Spoofing, Red Sea Activity Before Grounding
  2. May 2025

    MSC Antonia grounds in the Red Sea after GPS spoofing incident

    The 75,000-ton container ship MSC Antonia grounded in the Red Sea following an incident attributed to GPS spoofing and remained immobilized for more than five weeks.

    367,000-Ship Study Finds Global GPS Spoofing, Red Sea Activity Before Grounding
  3. 2025

    Persistent suspected GPS spoofing observed in Strait of Hormuz

    AIS observations identified a persistent suspected GPS-spoofing zone in the Strait of Hormuz during early 2025, more than a year before the 2026 Iran war disrupted commercial shipping through the strait.

    367,000-Ship Study Finds Global GPS Spoofing, Red Sea Activity Before Grounding
  4. Jan 2025

    Coordinated false vessel tracks appear near Port Sudan

    The bulk carrier Charmous and at least 11 other vessels recorded overlapping false movements near Port Sudan, including linear displacements sharing the same latitude to five decimal places. The patterns preceded the later MSC Antonia incident by five months.

    367,000-Ship Study Finds Global GPS Spoofing, Red Sea Activity Before Grounding
  5. Dec 31, 20242y ago

    Synchronized vessel position jumps occur in Gulf of Mexico

    Nearly 200 vessels displayed synchronized GPS-position jumps in the Gulf of Mexico. Researchers later reproduced the event using public NOAA AIS data.

    367,000-Ship Study Finds Global GPS Spoofing, Red Sea Activity Before Grounding
Do you run this?See the adversaries and campaigns active against your sector right now, ranked by what they're exploiting.
See Your Sector's Threats
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.