Attackers Used SQL Server for Command Execution and File Exfiltration in Viva Aerobus-Linked Intrusion
Attack Tradecraft · 2 sources · Updated 24d ago · First seen Oct 2, 2026
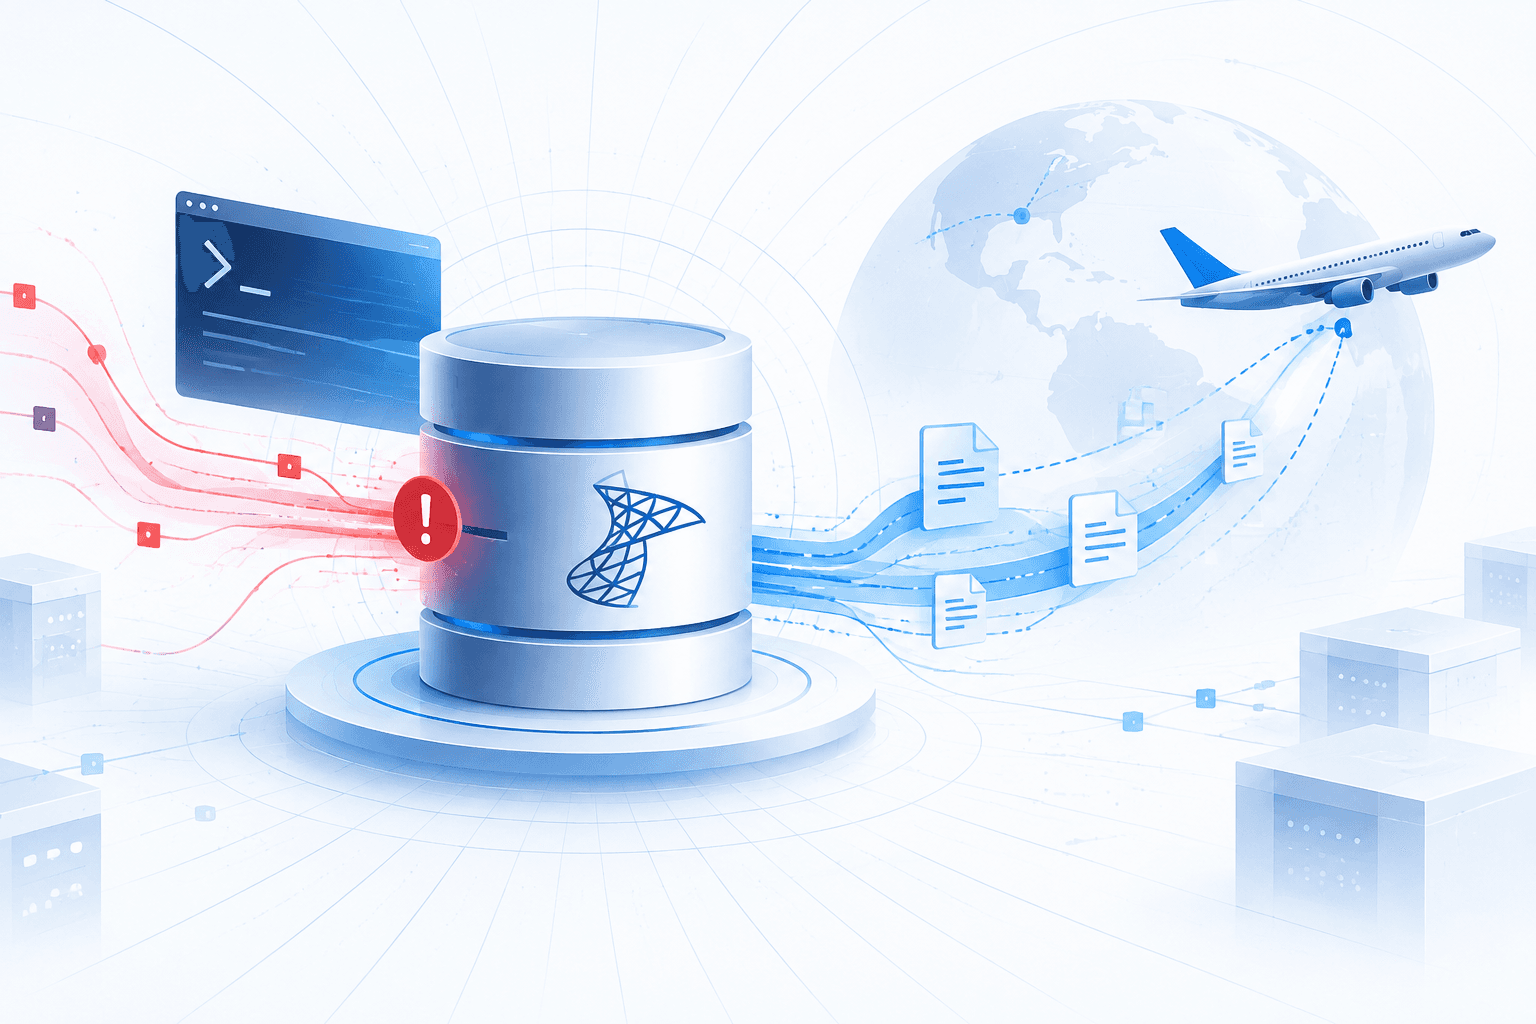
Attackers used Microsoft SQL Server as both an operating-system command execution channel and a file-exfiltration route in an intrusion linked to Mexican airline Viva Aerobus, active September 25–29, 2026. ThreatMon uncovered the activity through an attacker staging server exposed without authentication. The attackers abused SQL Server’s xp_cmdshell, used Base64-encoded PowerShell, and returned Base64-encoded file contents through SQL query output, avoiding a separate file-transfer channel. The exposed server held credential-harvesting tools, SQL credential-testing utilities, collected files, source code, and configuration artifacts supporting preparation for further SQL and SMB targeting.
Investigators did not establish the initial entry method, identify a named malware family, or confirm successful lateral movement or theft of sensitive passenger or payment data. Unrelated internet users also accessed the staging server, widening the potential exposure of its contents; ThreatMon warned that credentials and secrets present there should be considered compromised. Defenders should prioritize rotating exposed secrets, reviewing SQL Server command-execution activity, and restricting xp_cmdshell where unnecessary. Published indicators were described as automatically extracted and not independently verified, so they require validation before operational use.