Lunex Abuses Vulnerable AMD Driver to Blind Security Tools and Install Persistent Stealer
Attack Tradecraft · 3 sources · Updated 1mo ago · First seen Oct 2, 2026
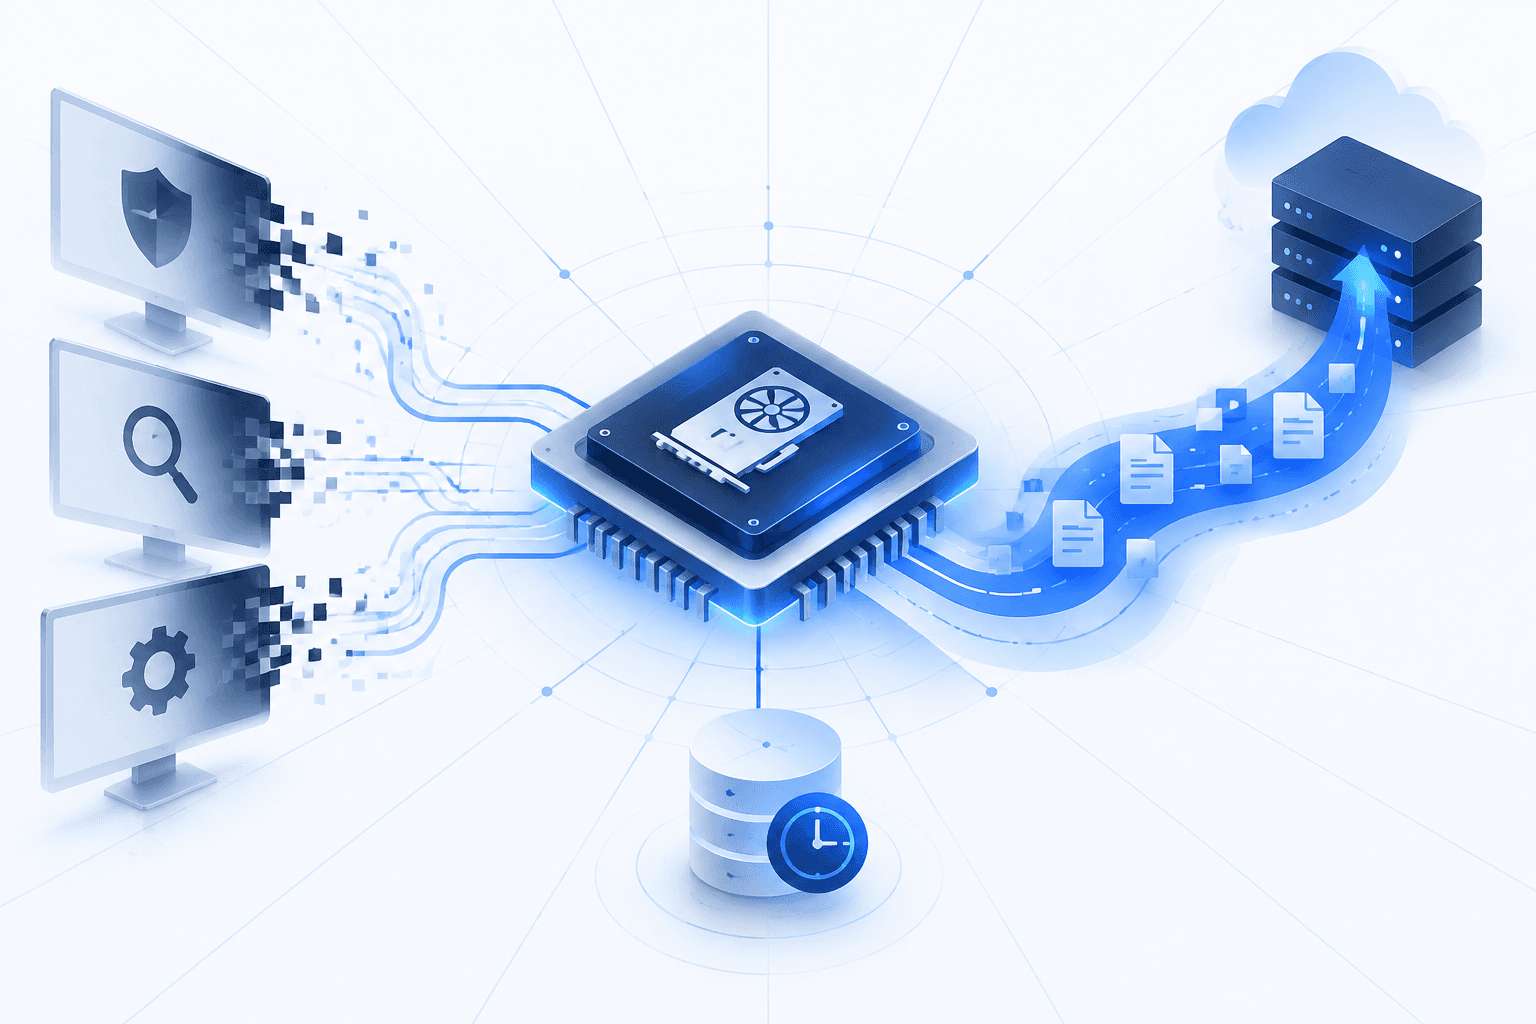
A Lunex malware campaign targets Ukrainian-speaking users with fake CAPTCHA pages that trick victims into installing a malicious MSI package. Ontinue identified a four-stage infection chain in which LunexLoader uses a bring-your-own-vulnerable-driver (BYOVD) technique to exploit AMD’s PDFWKRNL.sys driver, associated with CVE-2023-20598. The loader downloads build-specific Windows kernel symbols and selectively disables security-product callbacks while leaving endpoint security processes running, then deploys LunexStealer to steal browser credentials, cookies, authentication data, payment information, and cryptocurrency wallet data.
LunexStealer supports continued command-and-control tasking and installs Chrome and Edge Native Messaging Hosts that retain filesystem access and program-execution capabilities even after the main stealer executable is deleted. Remediation therefore requires removing the browser-based backdoor, scheduled task, and registry persistence—not just the stealer binary. Investigators identified 28 Lunex panels across 13 countries and assessed that Russian-speaking developers sell the malware-as-a-service platform to independent, financially motivated criminal operators; Ontinue attributed the analyzed operation to a CIS-aligned actor.