Telerik RadAsyncUpload Deserialization Flaw Enables Remote Code Execution
Vulnerability Disclosure · 4 sources · Updated 18d ago · First seen Dec 11, 2019
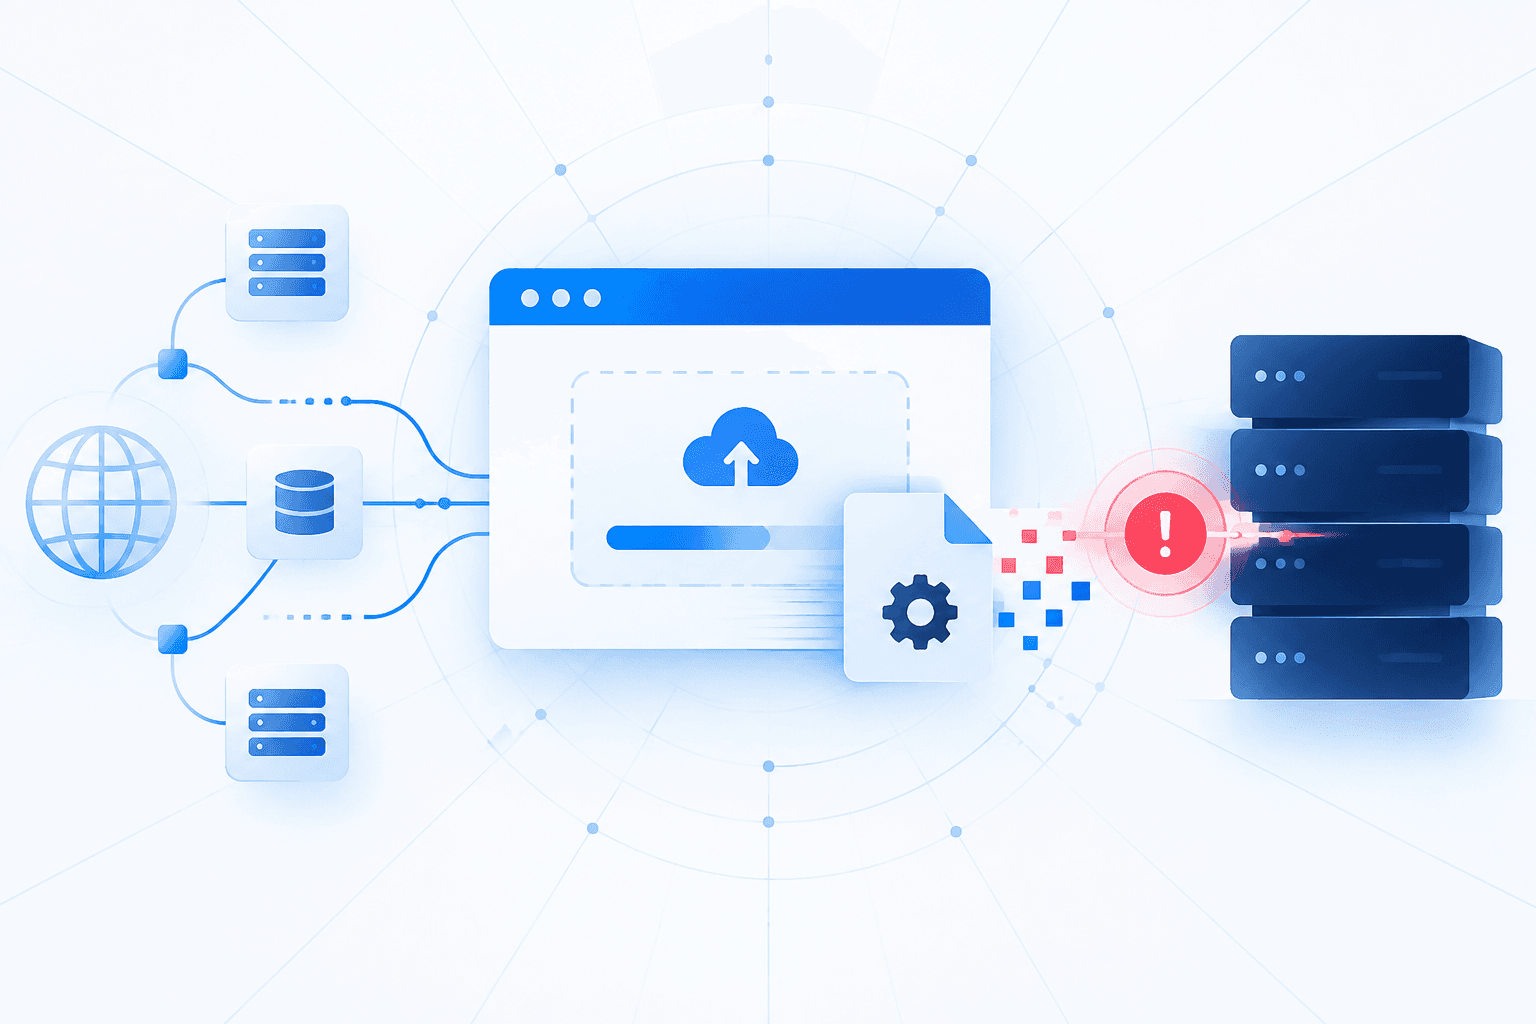
CVE-2019-18935 exposes Progress Telerik UI for ASP.NET AJAX deployments through a .NET JavaScriptSerializer deserialization flaw in the RadAsyncUpload component, affecting releases through version 2019.3.1023. Attackers who know or can break the component’s encryption keys can potentially execute malicious code on the server in the context of the IIS worker process, w3wp.exe, when type whitelisting is not enabled. Encryption keys may be obtained through CVE-2017-11317, CVE-2017-11357, or other means.
Telerik recommends upgrading to R1 2020 (2020.1.114) or later, where type whitelisting is enabled by default, and applying its recommended security settings. Version 2019.3.1023 offers a protective setting that administrators must explicitly enable; earlier versions lack that protection. Organizations should identify affected ASP.NET AJAX deployments, prioritize upgrades, and verify that type whitelisting and recommended encryption settings are configured rather than relying on encryption alone.