SSH Compression Side Channel Exposes Cross-Channel Secrets; OpenSSH 10.6 Drops LZ77
Patch & Detection Intelligence · 12 sources · Updated 20d ago · First seen Oct 6, 2026
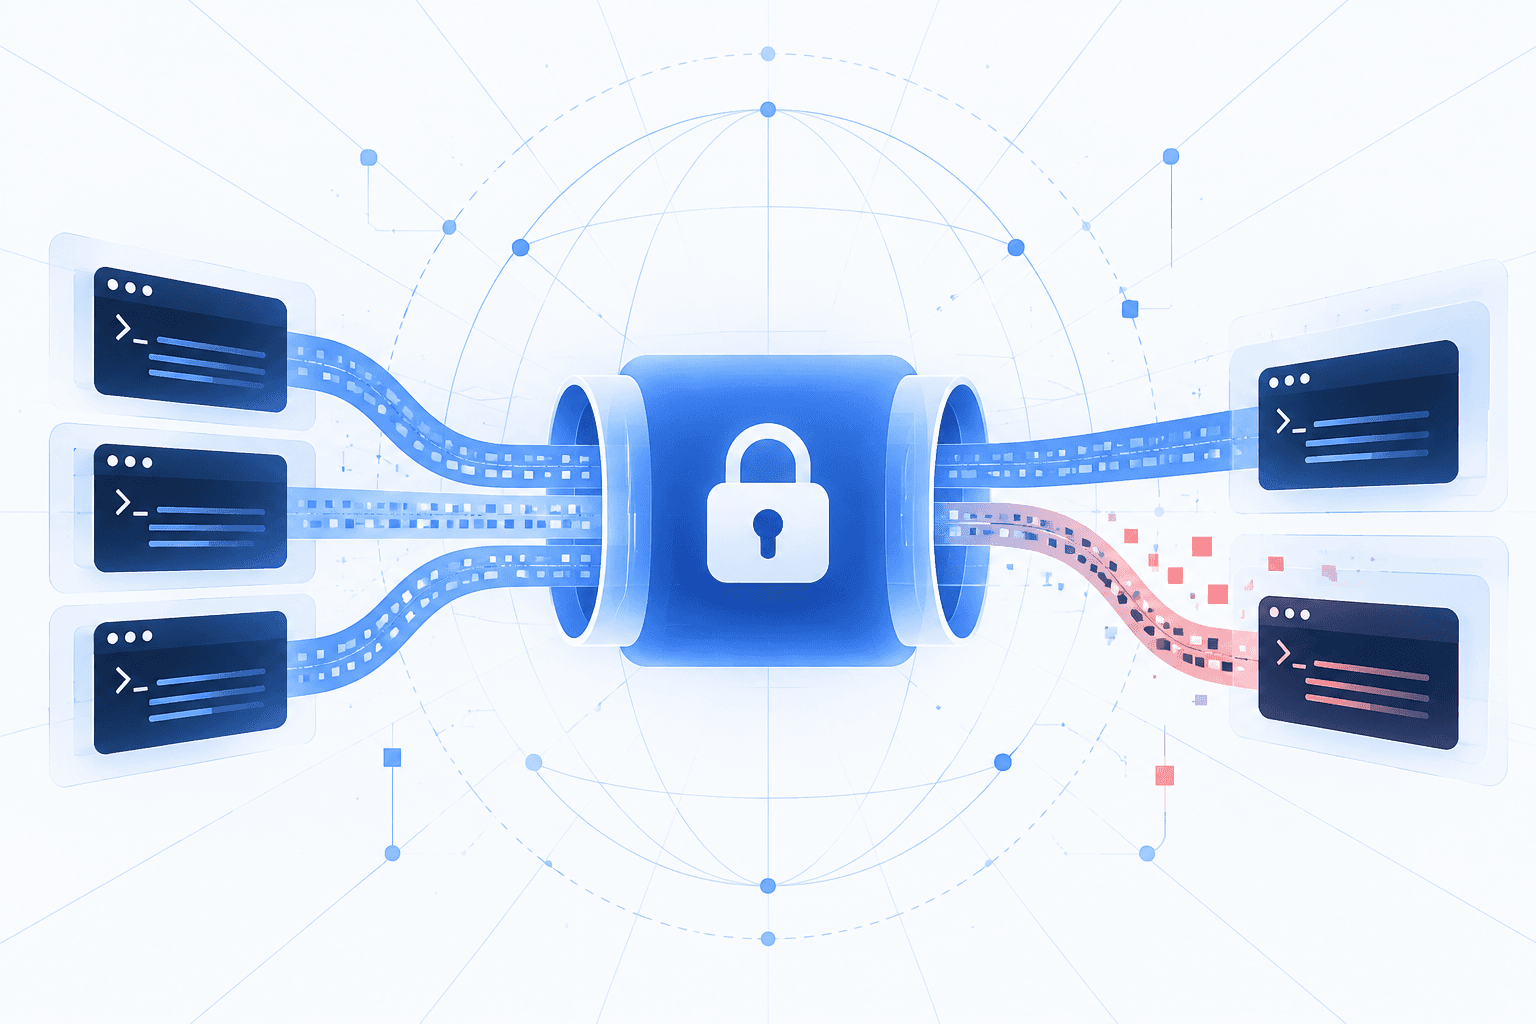
Researchers Fabian Bäumer and Marcus Brinkmann disclosed an SSH compression side channel that can recover secrets across multiplexed channels sharing a compression context. When compression is enabled, an attacker who can inject partially chosen plaintext into one channel and observe ciphertext lengths can infer secrets transmitted through another channel on the same connection. The researchers describe it as the first known compression side-channel attack against SSH. In their lowest-noise test, they recovered an eight-character secret from a 26-letter alphabet in at most 276 guesses; practical exploitability depends on application behavior, protocol noise, and implementation characteristics.
OpenSSH 10.6 reportedly removes LZ77 compression support because observable compressed-message sizes can disclose information. The release also includes security fixes involving malicious SFTP servers, GSSAPI authentication-attempt accounting, command-line username handling, access restrictions, and privilege handling, although corrupted encoding in the release report limits confidence in precise vulnerability details. Additional changes include hybrid ssh-mldsa44-ed25519 signatures, weak-cryptography warnings, and authentication improvements. Organizations should identify SSH connections using compression, disable it where feasible, and validate the release’s security changes before upgrading.