ccTLD Registry Hijacks Enable Unauthorized Certificates; Chrome Blocks Identified Certificates
Breach & Incident Intelligence · 21 sources · Updated 13d ago · First seen Oct 6, 2026
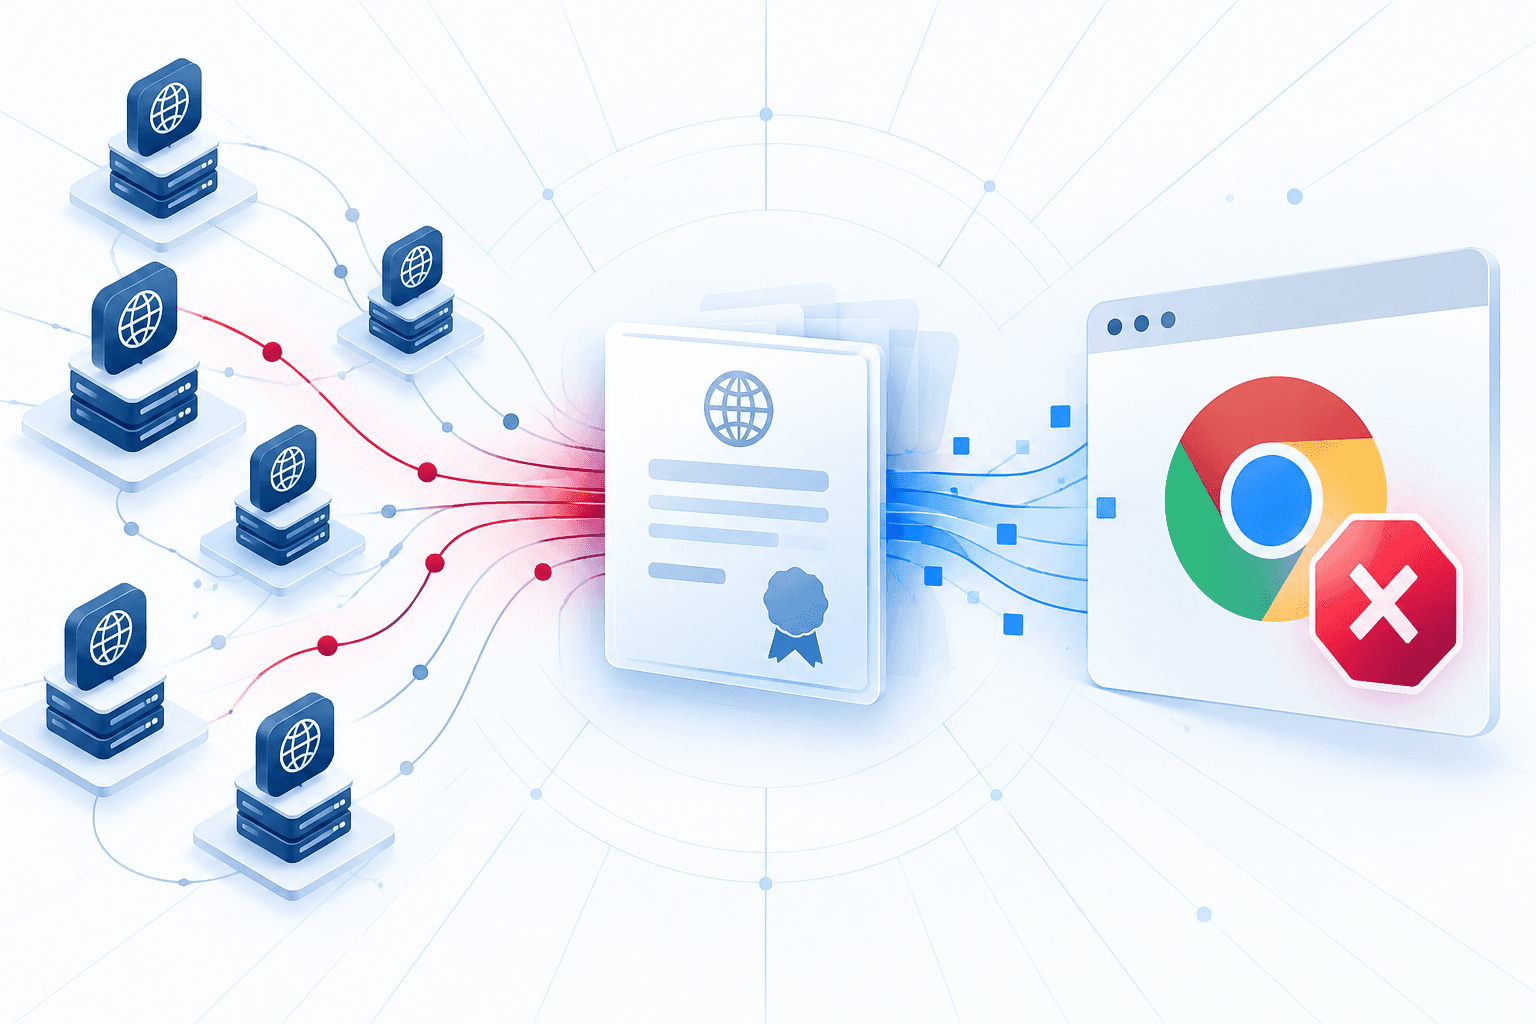
Attackers compromised third-party country-code top-level domain infrastructure for .gh (Ghana), .sl (Sierra Leone), and .as (American Samoa), altered authoritative DNS records, and obtained unauthorized HTTPS certificates for Google domains and other organizations. Google said its own systems were not compromised and that it had no reason to believe the issuing certification authorities acted improperly. It blocked identified unauthorized certificates in Chrome through CRLSets, coordinated revocation with the issuing authorities, and examined Certificate Transparency logs to identify additional affected organizations.
Chrome users need take no action, but Google warned that its browser-side protections may not cover every affected domain or protect users of other browsers. CRLSets provide rapid emergency certificate blocking and selectively include other revocations; they are not a comprehensive replacement for revocation checking, and Chrome generally does not perform online OCSP or CRL checks by default. Domain owners should monitor Certificate Transparency across their entire domain portfolios and publish restrictive Certification Authority Authorization (CAA) records, standardized in RFC 8659, with account and validation-method restrictions where supported. These issuance controls help prevent further unauthorized certificates after DNS control is restored, but do not substitute for securing registry and authoritative DNS infrastructure.