BlueKit Phishing Service Adds AI Messaging and Session-Cookie Theft for Account Hijacking
Threat Actor Intelligence · 2 sources · Updated 1mo ago · First seen Oct 7, 2026
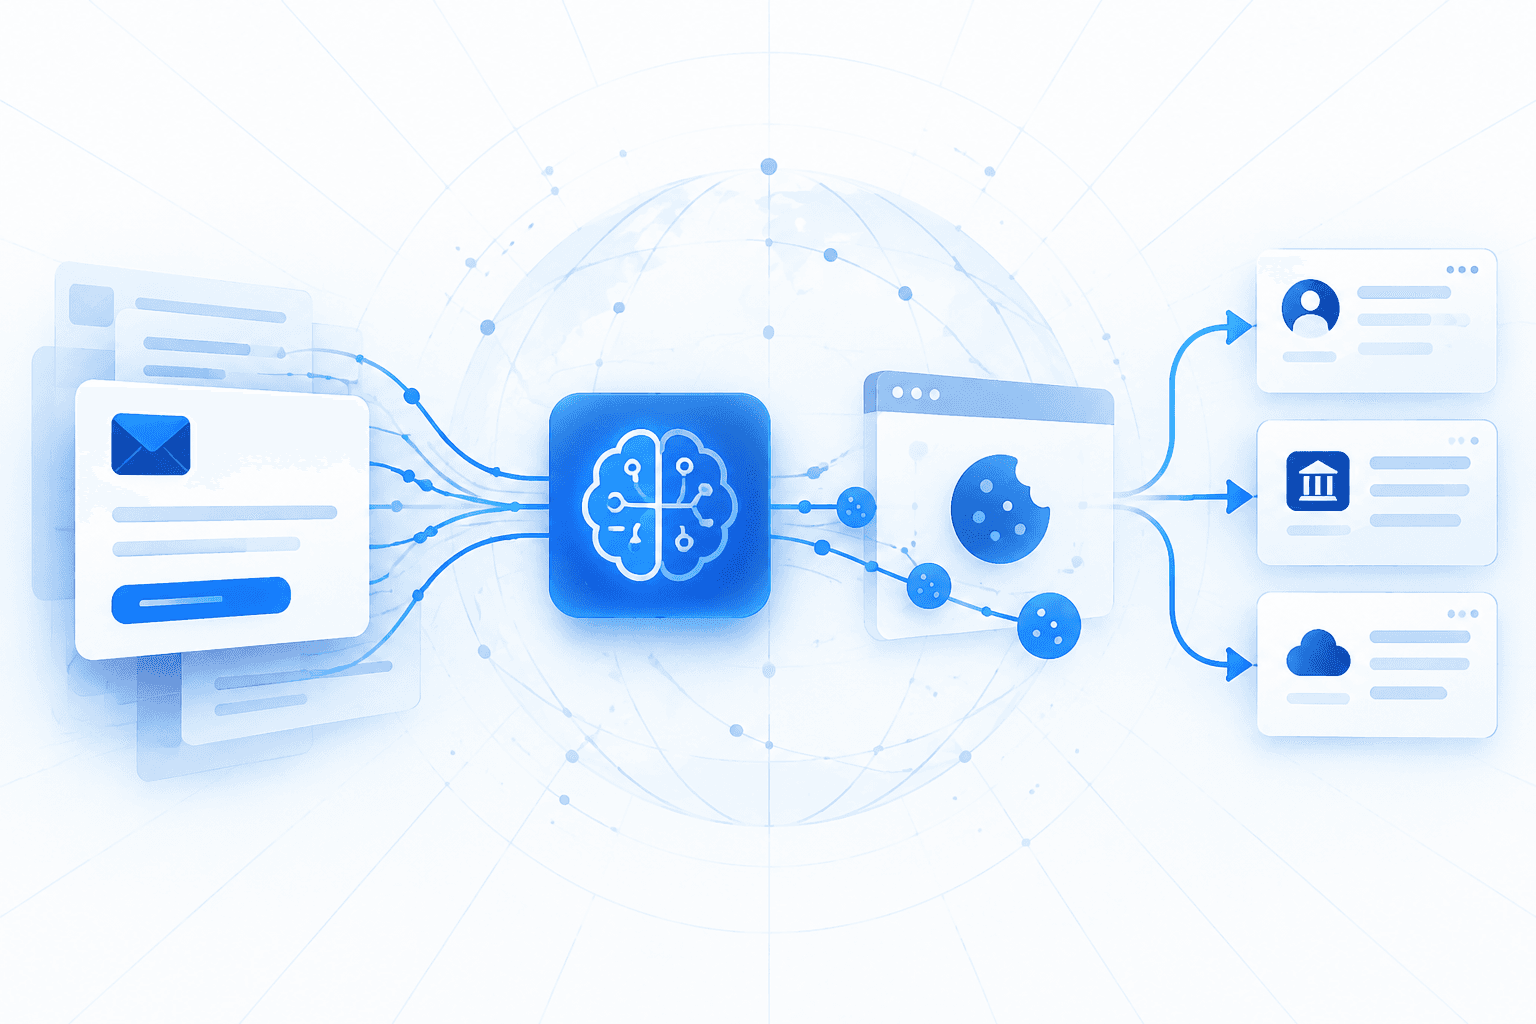
Malwarebytes tracked BlueKit, a subscription-based phishing-as-a-service toolkit marketed by the threat actor “petrushka” that combines campaign management, impersonation templates and account-access capture. First offered on a cybercrime forum in April, the service advertised 97 brands across 176 template variants by September, targeting consumer services, financial institutions, cryptocurrency platforms and corporate login gateways, including single sign-on services. Its operators advertise deployment in approximately 10 minutes, with subscriptions priced from $250 for seven days to $940 for 30 days.
BlueKit’s capabilities include session-cookie capture, device fingerprinting and an integrated SMS sender, alongside an advertised unrestricted AI assistant for generating fraudulent messages. These features lower the technical barrier to phishing and can facilitate account hijacking through stolen sessions, making credential-only defenses insufficient. Security teams should prioritize phishing-resistant authentication, monitoring for suspicious session reuse and rapid session revocation after suspected compromise. The operators claimed more than 1,000 customers on August 29, but that claim is not independently verified, and published revenue estimates are hypothetical rather than confirmed earnings.