
Loading story…
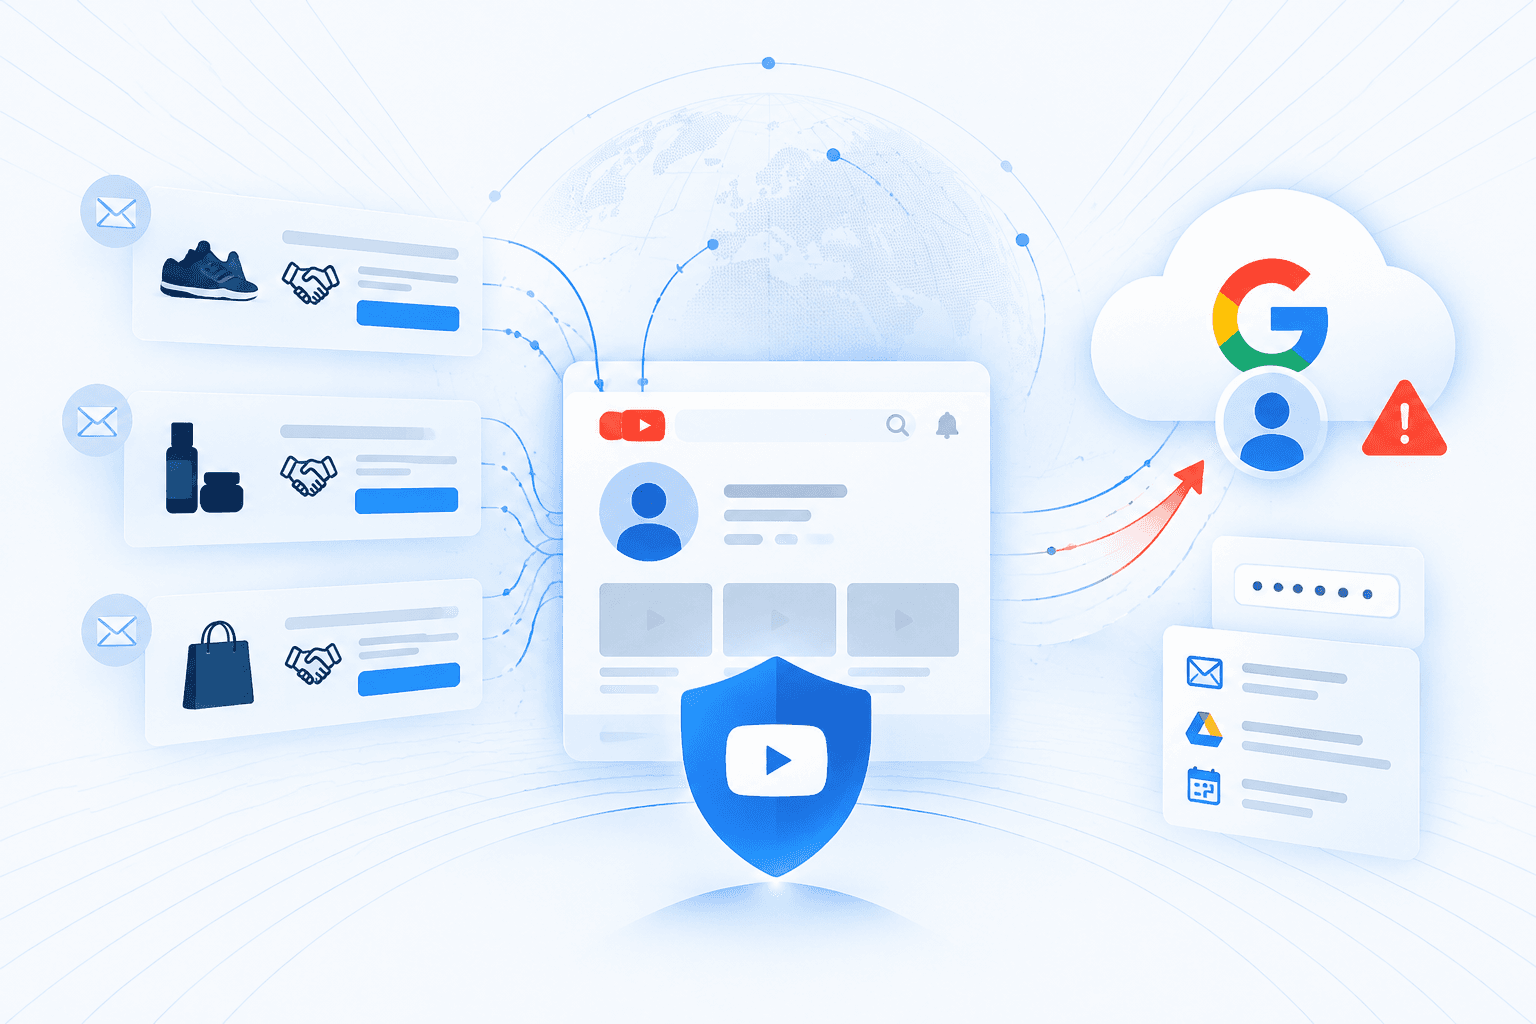
A phishing campaign is targeting YouTube creators with personalized sponsorship offers impersonating brands including Hollyland, Nike, and Spotify. Attackers negotiate collaboration rates before directing creators to fraudulent partnership platforms that retrieve public YouTube channel information and display campaign metrics, income calculators, and purported contract and payment features to build credibility. The platforms then steer victims toward Google sign-in: fraudulent login pages can capture passwords and one-time codes, while excessive permissions granted through genuine authentication could expose channel-management capabilities.
One victim reported that attackers took over her Google account and changed recovery details and backup codes to obstruct recovery. Shared website code, branding elements, and functionality across changing domains suggest a modular campaign targeting creators internationally. Creators and organizations managing YouTube channels should independently verify sponsorship offers through official brand contacts, scrutinize sign-in destinations and requested permissions, and treat a polished partnership portal or accurate channel information as insufficient proof of legitimacy.
Get the infrastructure and lures behind it.
7 events from the most recent confirmed update back to the earliest known activity.
AndaSeat warned about sponsorship offers involving Creoventura at creoventura[.]com and explicitly denied any affiliation or partnership with the agency. The denial contradicted the website’s claimed brand relationships, which also listed Hollyland and Maono.
ESET’s analysis identified shared functionality, favicons, meta descriptions, and source-code components across the fraudulent platforms, alongside variants impersonating Nike and Spotify. It also described counterfeit Google login pages that can steal passwords and one-time codes, distinguishing them from genuine authentication flows that may request excessive permissions.
Hollyland issued a public warning about attackers impersonating the company in sponsorship offers to creators.
The campaign’s domains and names changed repeatedly between June and August, although the source does not specify the year. Variants included Scouty-branded platforms and matchyjoin[.]com, which retrieved public channel information and redirected targets to a Google login page.
A creator reported losing control of her Google account after falling for a version of the sponsorship scam. Attackers replaced her phone number and recovery email and added their own backup codes to obstruct recovery.
After the journalist replied with her rates, the attacker directed her to joinmatchy[.]com/hollyland. The sender claimed the site would verify channel performance and handle the agreement and payment.
A sender calling herself “Brandi” and claiming to represent Hollyland’s Creator Partnerships team emailed a journalist in Peru. The message referenced specific YouTube videos and offered a device and potential long-term collaboration, but came from a domain unrelated to Hollyland.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. View all 9 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
Get the infrastructure, lures, and IOCs behind this campaign, ready to push into your email and identity stack.
2 references tracked. Mallory keeps watching after this page renders.
Map indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Attackers are running a large-scale phishing campaign that impersonates recruiters from more than 30 major brands to steal **Google account credentials**, primarily from job seekers and marketing professionals. The emails use real recruiters’ names and photos and direct victims to fake interview scheduling or career pages, including a confirmed fake **McKinsey & Company** careers site hosted on Netlify, before presenting a browser-in-the-browser **Google sign-in** prompt designed to capture Gmail logins. The operation relies on a nested redirect chain through legitimate business services including **PeopleForce**, **Salesforce Marketing Cloud** infrastructure on `exct.net`, and **Wise Agent** to make the phishing flow appear trustworthy and evade detection. Researchers said the campaign has been active for at least five months and spans brands across consulting, technology, retail, travel, hospitality, entertainment, and consumer goods, while noting that abuse of those platforms does not necessarily indicate the services themselves were compromised.
Jul 9, 2026
A sophisticated cybercriminal campaign has significantly expanded its reach by leveraging Google Ads and YouTube to distribute malware disguised as free access to TradingView Premium, a popular financial trading analysis service. Security researchers from Bitdefender Labs have tracked this operation for over a year, noting its evolution from initially exploiting Facebook Ads to now targeting a broader audience through Google’s advertising ecosystem and YouTube. The attackers employ highly organized tactics, utilizing more than 500 unique website addresses and deploying thousands of malicious ads daily in multiple languages, including English, Vietnamese, and Thai. To enhance credibility and evade detection, the threat actors hijack legitimate, verified business accounts on Google and YouTube, such as a Norwegian design agency’s Google advertiser account. They also compromise verified YouTube channels, erasing original content and rebranding them to closely mimic the official TradingView channel, complete with authentic logos, banners, and mirrored playlists. These fake channels use unlisted videos, which are promoted through paid ads, to lure victims with promises of secret methods for obtaining TradingView Premium for free. One such video amassed over 182,000 views in just a few days, demonstrating the campaign’s aggressive reach. Users who click on these ads are redirected to malware-laden downloads designed to steal credentials and compromise accounts. The campaign’s expansion to Google and YouTube exposes a much larger pool of content creators and regular users to credential theft and account compromise. The use of hijacked, verified accounts and sophisticated impersonation techniques makes the scam particularly convincing and difficult for users to detect. Researchers emphasize that the campaign’s persistence and adaptability, including its ability to quickly shift platforms and tactics, pose a significant threat to the financial and personal security of targeted individuals. The operation’s global scale and multilingual approach indicate a well-resourced and coordinated threat actor. Security experts recommend heightened vigilance, especially when encountering offers for free premium services through ads, and urge platforms to strengthen verification and monitoring processes to prevent account hijacking. The campaign’s technical sophistication, including the abuse of advertising infrastructure and social engineering, highlights ongoing challenges in combating malvertising and credential theft. Organizations and individuals are advised to verify the authenticity of offers and channels before engaging with advertised content. The incident underscores the need for continuous monitoring of advertising platforms for signs of compromise and malicious activity. Bitdefender’s ongoing research into the campaign provides valuable insights into the evolving tactics of cybercriminals targeting the financial sector. The expansion of this scam to major platforms like Google and YouTube marks a significant escalation in the threat landscape for both content creators and everyday users.
Jun 29, 2026
Cybercriminals are increasingly exploiting social media and video platforms such as Facebook and YouTube to distribute scam advertisements, deepfakes, and malware. Former Meta executives have launched a nonprofit initiative to address the growing lack of transparency and stagnation in anti-scam ad technology, highlighting the persistent evolution of scam tactics and the use of AI to create convincing fraudulent content. Meanwhile, YouTube faces a surge in scams and malware campaigns, with attackers leveraging the platform’s recommendation algorithms, hijacked accounts, and AI-generated videos to reach wide audiences. Notable operations include the "YouTube Ghost Network," which used thousands of videos on compromised channels to lure users into downloading malware or visiting phishing sites, and scams that migrated from Facebook Ads to YouTube and Google Ads, exploiting trusted brands and hijacked ad accounts. The sophistication of these scams is amplified by the use of deepfakes and synthetic identities, making it increasingly difficult for both users and traditional moderation systems to detect fraudulent activity. Security researchers emphasize the need for advanced detection technologies, such as light spectrum analysis and cryptographic verification, to combat these threats. The ongoing arms race between scammers and platform defenders underscores the urgent need for industry-wide improvements in transparency, technology investment, and layered verification standards to restore trust in online advertising and content platforms.
Jun 29, 2026