BlueMoon Exploit Kit Chains Chrome and Windows Flaws to Deliver Espionage Malware
Active Exploitation · 2 sources · Updated 1mo ago · First seen Aug 28, 2026
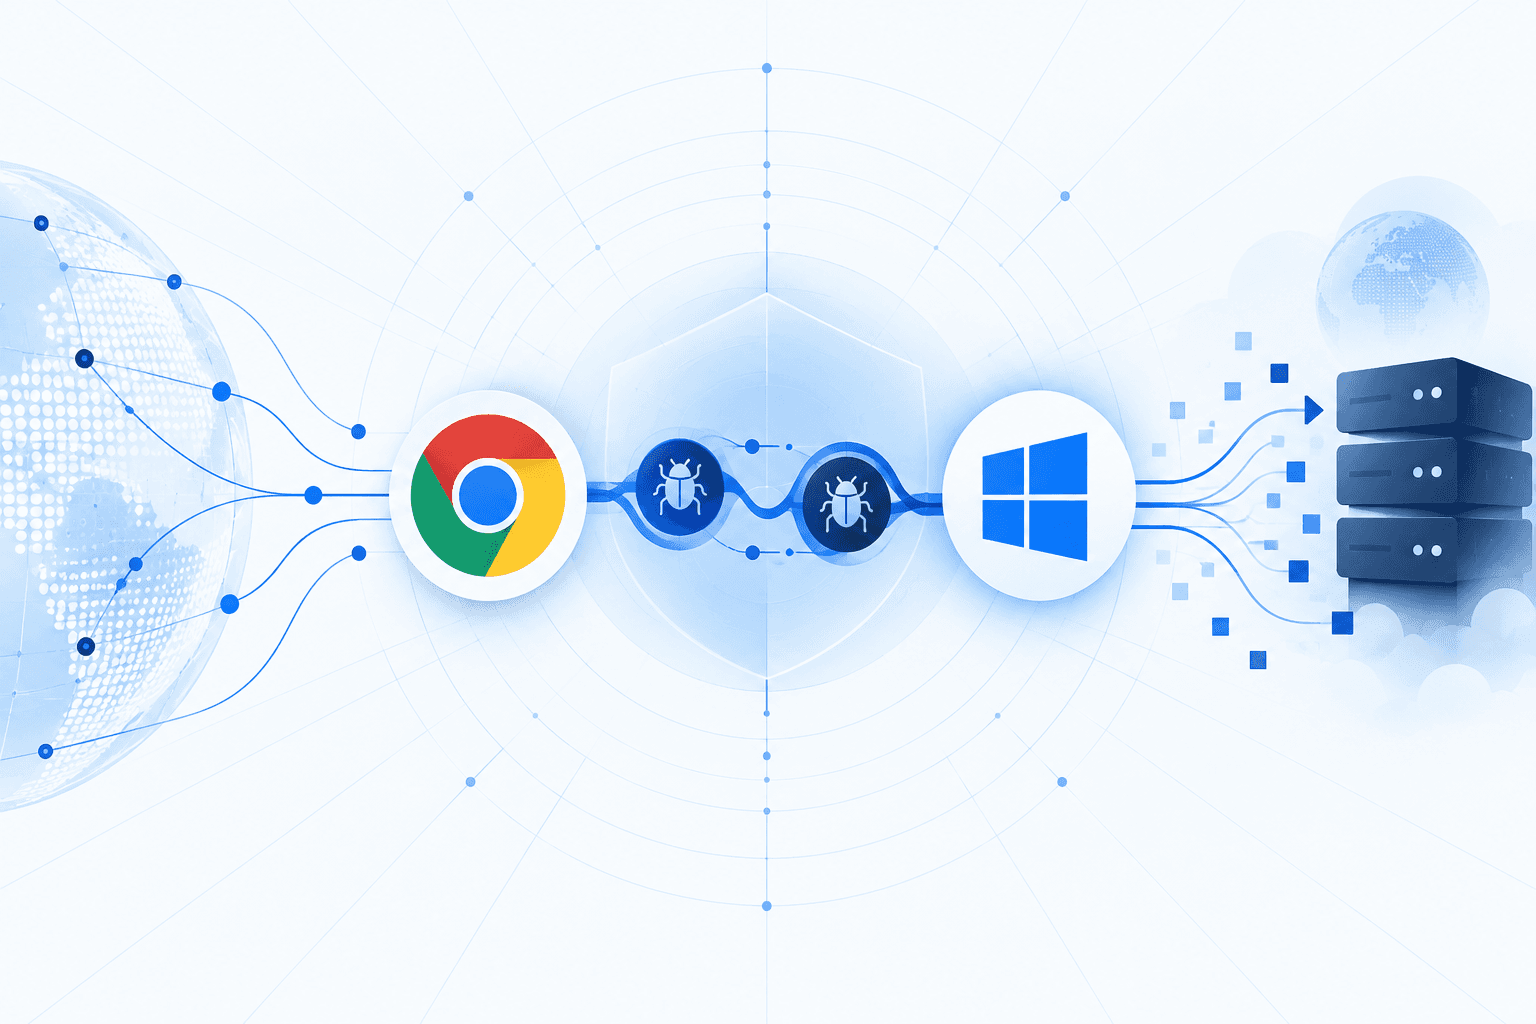
The BlueMoon Exploit Kit is reportedly being used by four espionage-focused threat clusters to deliver Windows malware through spearphishing links to attacker-controlled websites. First observed on August 28, 2026, the kit targets Chrome and other Chromium-based browsers, chaining CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880 for V8 type confusion, V8 sandbox escape, and Windows kernel privilege escalation, ultimately executing payloads outside the browser renderer sandbox. Some exploit pages redirect victims to legitimate websites after the attack.
Reported campaigns targeted organizations across multiple industries in the United States and Southeast Asia; several participating clusters have a suspected China nexus. Observed payloads included GemStone, ShadowPad, a Rust loader, and custom malware with an in-memory .NET stage, using distinct persistence and command-and-control mechanisms. Successful exploitation requires both a vulnerable browser and a Windows build supported by the kernel exploit, which was limited to older builds. Defenders should prioritize remediation of the three flaws, identify vulnerable browser and Windows combinations, and investigate spearphishing-linked browser activity followed by unexpected process execution.