BlackByte Ransomware Uses ProxyShell Exploitation and Double Extortion
Active Exploitation · 2 sources · Updated 21d ago · First seen Dec 8, 2021
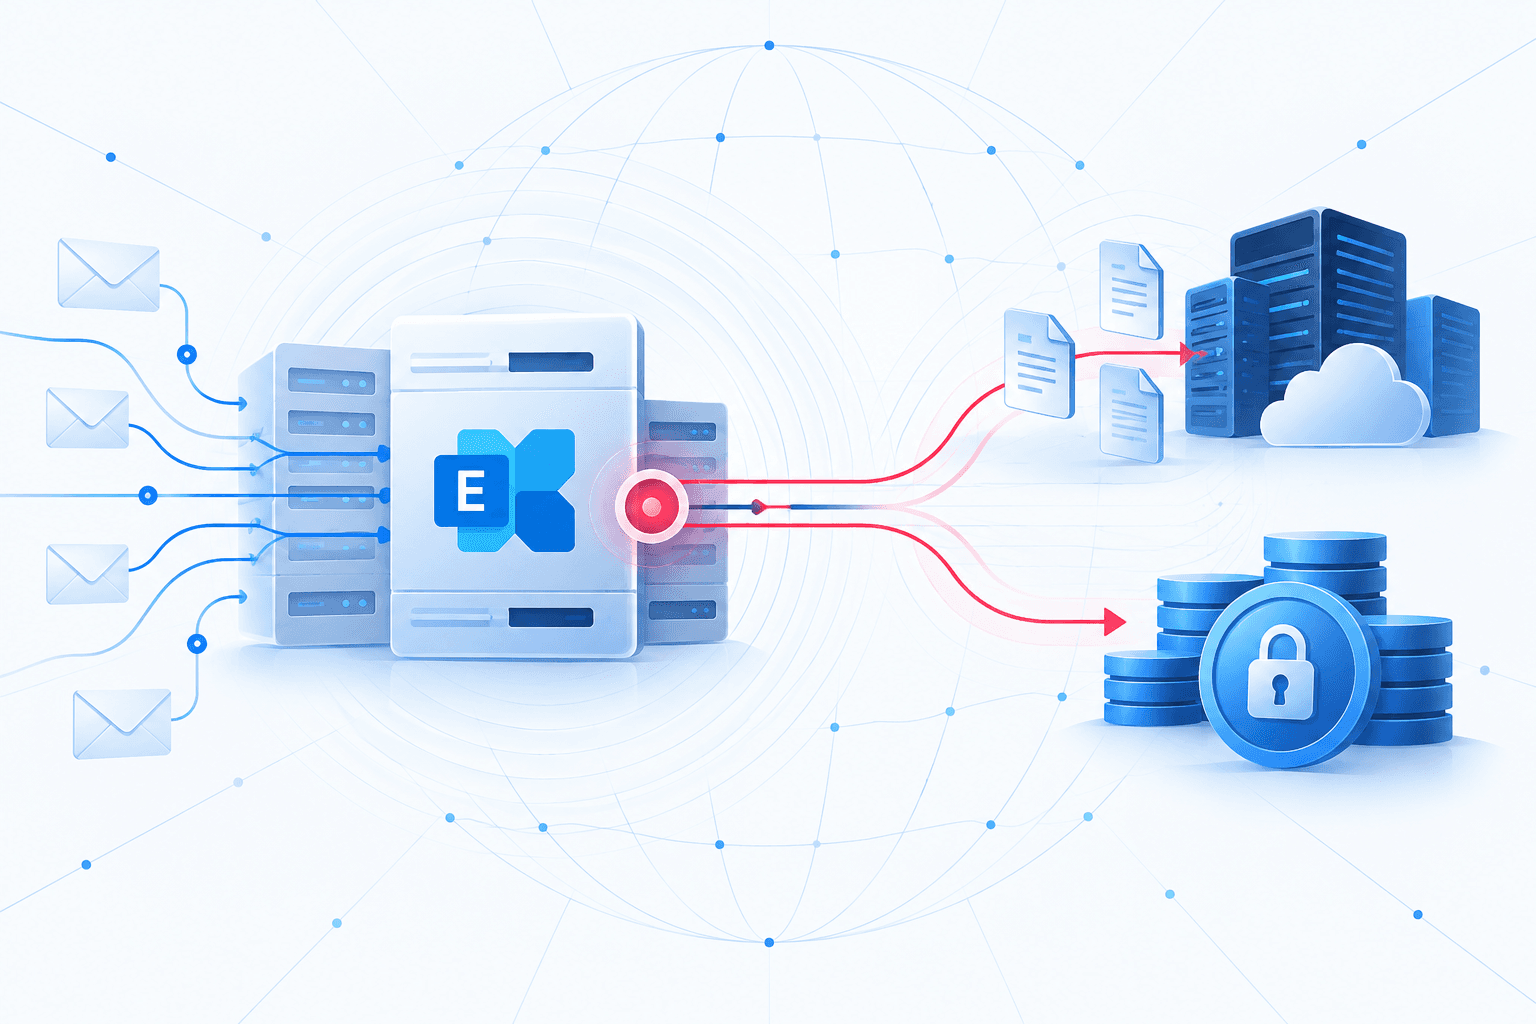
BlackByte ransomware intrusions have exploited vulnerabilities in public-facing systems, with Red Canary reporting a November 2021 attack involving ProxyShell exploitation of Microsoft Exchange. The ransomware-as-a-service operation uses double extortion, combining file encryption with threats to expose stolen data. ReliaQuest also documented Cobalt Strike beacons in earlier intrusions, highlighting the need to investigate supporting attacker activity rather than only the ransomware payload.
The FBI and U.S. Secret Service issued a joint advisory containing BlackByte indicators of compromise, reported in ReliaQuest’s February 13, 2022 update. Recommended defenses include patching exposed systems, blocking anonymous file-upload services used by BlackByte, maintaining endpoint security coverage and offline backups, and enforcing strong passwords and multifactor authentication. Early BlackByte variants reused encryption keys, making some files encrypted before October 2021 potentially recoverable; that recovery possibility should not be assumed to apply to later infections.