Critical TeamCity Deserialization Flaw Exploited to Execute Unauthenticated Commands
Active Exploitation · 2 sources · Updated 21d ago · First seen Aug 24, 2026
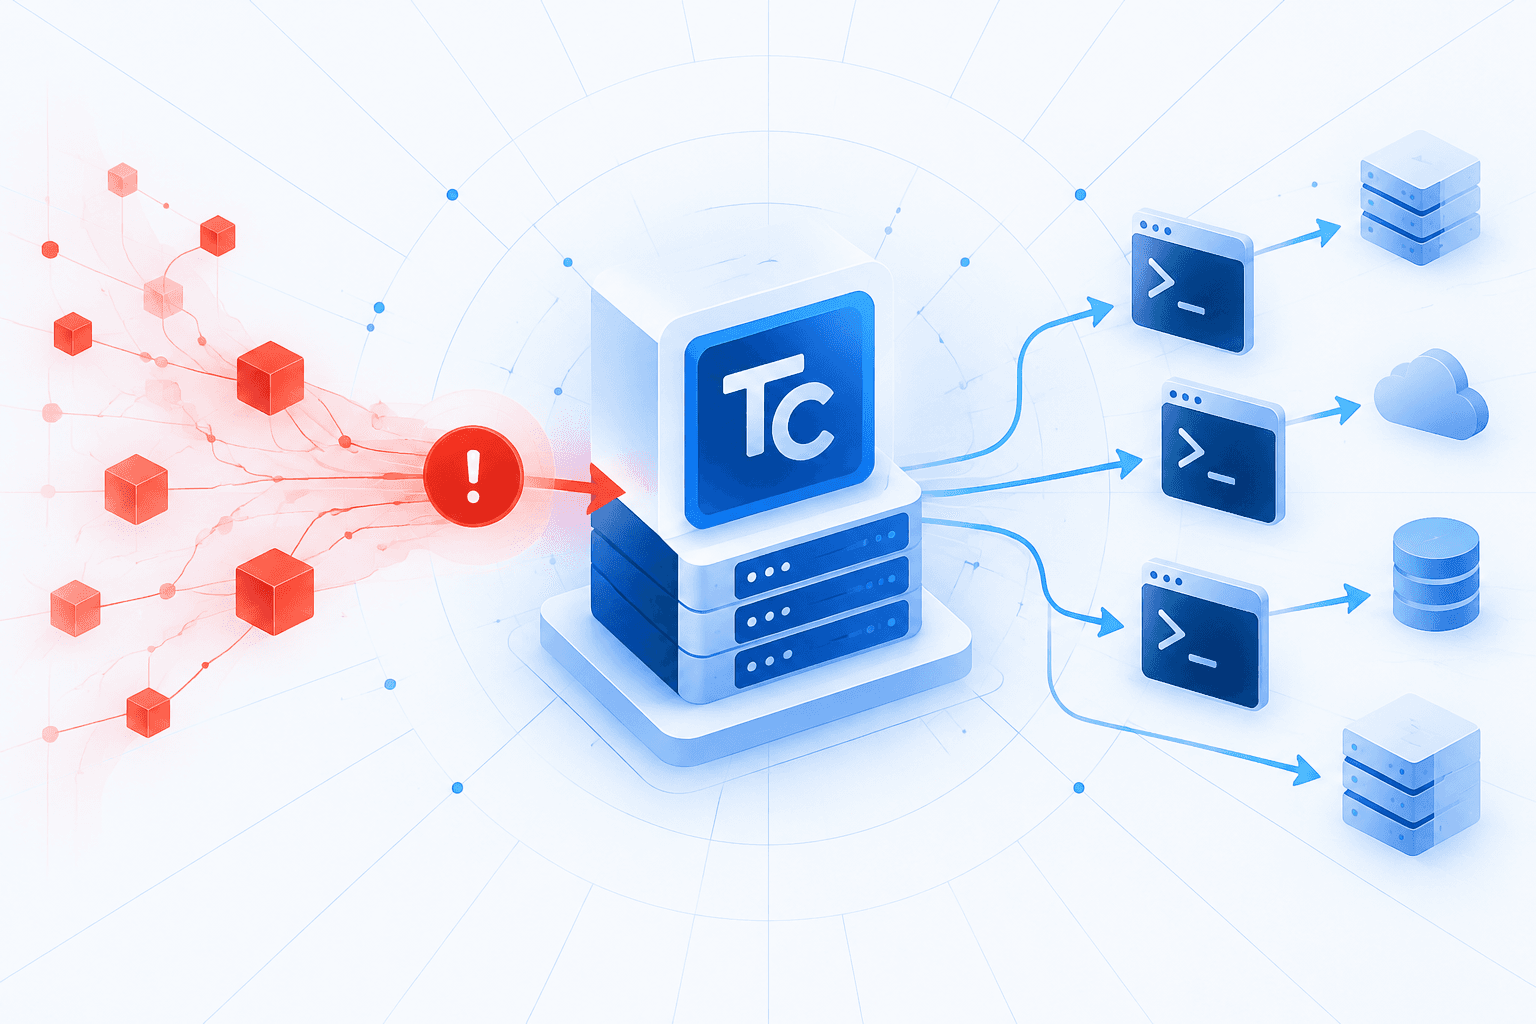
Attackers are actively exploiting CVE-2026-63077, a critical unsafe deserialization vulnerability in JetBrains TeamCity On-Premises, with exploitation confirmed in Australia by the Australian Signals Directorate’s Australian Cyber Security Centre (ASD’s ACSC). The flaw carries a CVSS score of 9.8 and allows unauthenticated attackers with HTTP or HTTPS access to abuse the agent polling protocol, bypass authentication, and execute operating system commands with the privileges of the server process. JetBrains disclosed the vulnerability on July 27, 2026, initially reporting no known exploitation; CISA subsequently added it to its Known Exploited Vulnerabilities catalog on August 5. Previdian also reports observed exploitation attempts.
JetBrains released fixes in TeamCity versions 2025.11.7 and 2026.1.3. ASD’s ACSC reported no evidence that attackers were targeting a particular industry or sector and urged organisations to assess their exposure, reconsider internet-facing access, follow vendor mitigation guidance, and patch as soon as practicable. Security teams should prioritise remediation of exposed TeamCity servers and monitor for suspicious activity using vendor-released indicators of compromise, given the potential for server-level command execution to compromise build infrastructure.