Agent Tesla Phishing Campaign Exploits Office Flaw Through Fake Quotation Requests
Active Exploitation · 2 sources · Updated 1mo ago · First seen Jul 28, 2023
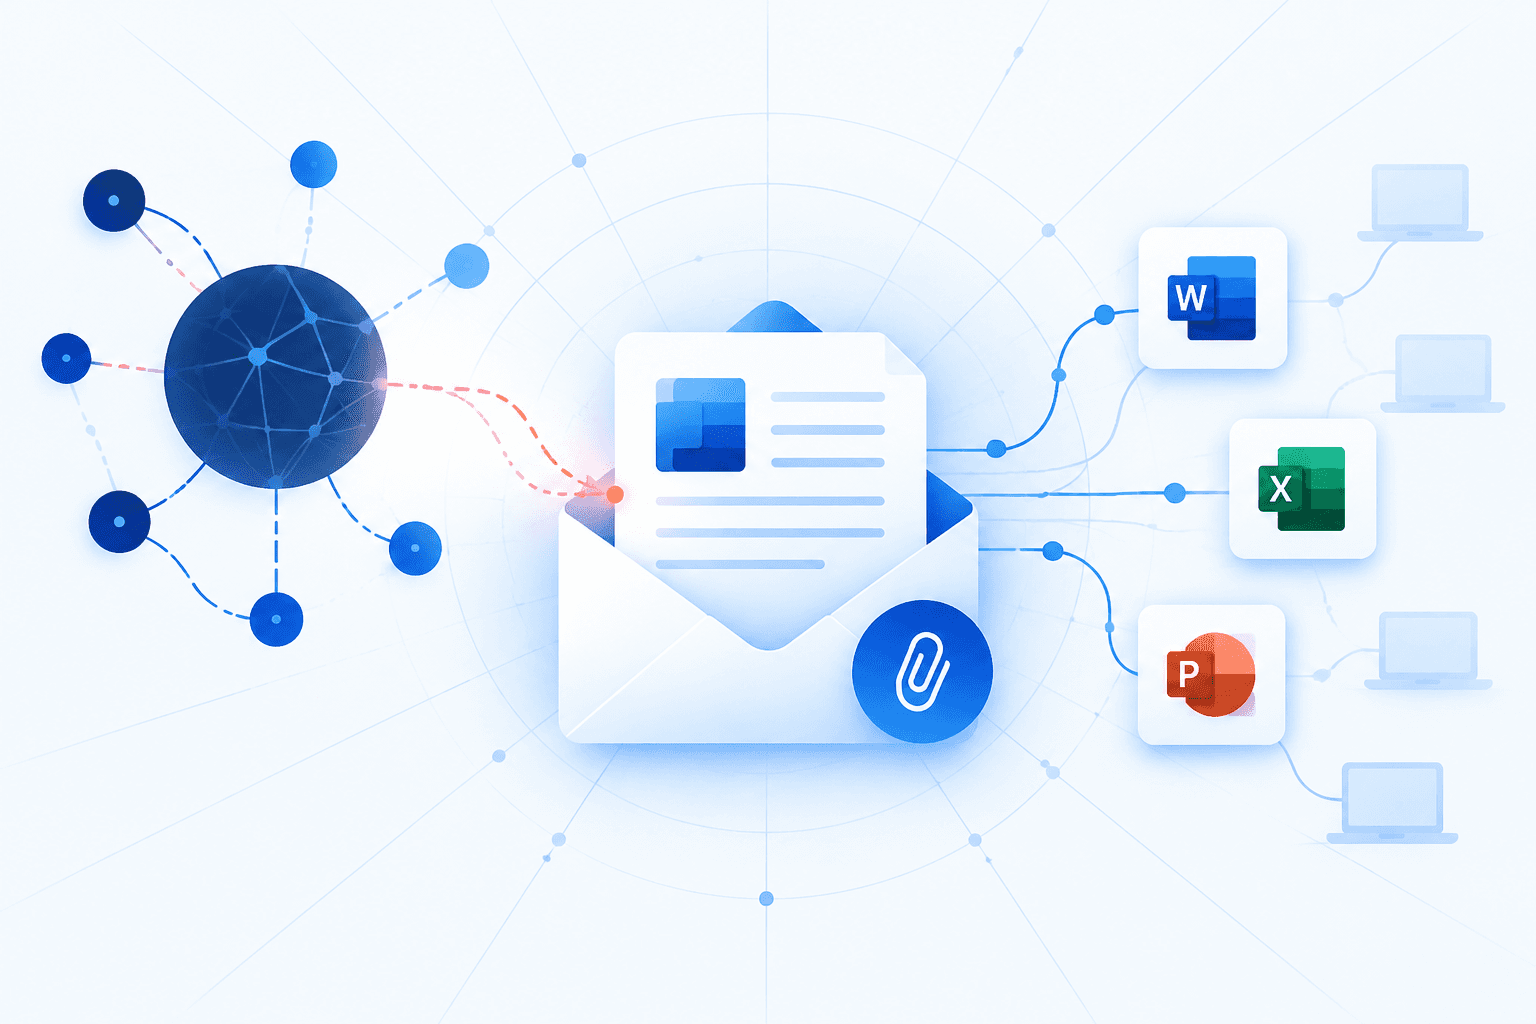
Bitdefender Labs identified a phishing campaign distributing Agent Tesla through malicious RTF attachments disguised as price quotation requests. The emails claim to represent a South Korean mining and metals company, while the sending domain impersonates an oil and gas group in Kazakhstan. The attachment exploits CVE-2018-0802 and references an external resource that initiates the malware download. Messages were distributed globally; 42% of observed attacks originated from IP addresses in the Netherlands and 38% from the United States. These figures describe sending infrastructure, not attacker attribution.
Once deployed, Agent Tesla collects sensitive information and exfiltrates it through SMTP to attacker-controlled email accounts or through Telegram. Organizations should prioritize Office patching, scrutinize unsolicited quotation attachments, and investigate unexpected outbound SMTP or Telegram activity. Microsoft’s advisory for the separate Office memory-corruption vulnerability CVE-2017-11882 also highlights the importance of addressing legacy Office flaws; the campaign report specifically identifies CVE-2018-0802 as the exploited vulnerability.