Mallory
← Back to News
actively-exploited-vulnerabilitydata-exfiltration-methodperimeter-device-exposurethreat-infrastructure-tracking

FortiManager Exploitation Linked to Payload Downloads and Suspected Configuration Theft

Active Exploitation · 2 sources · Updated 1mo ago · First seen Jan 1, 2026
FortiManager Exploitation Linked to Payload Downloads and Suspected Configuration Theft

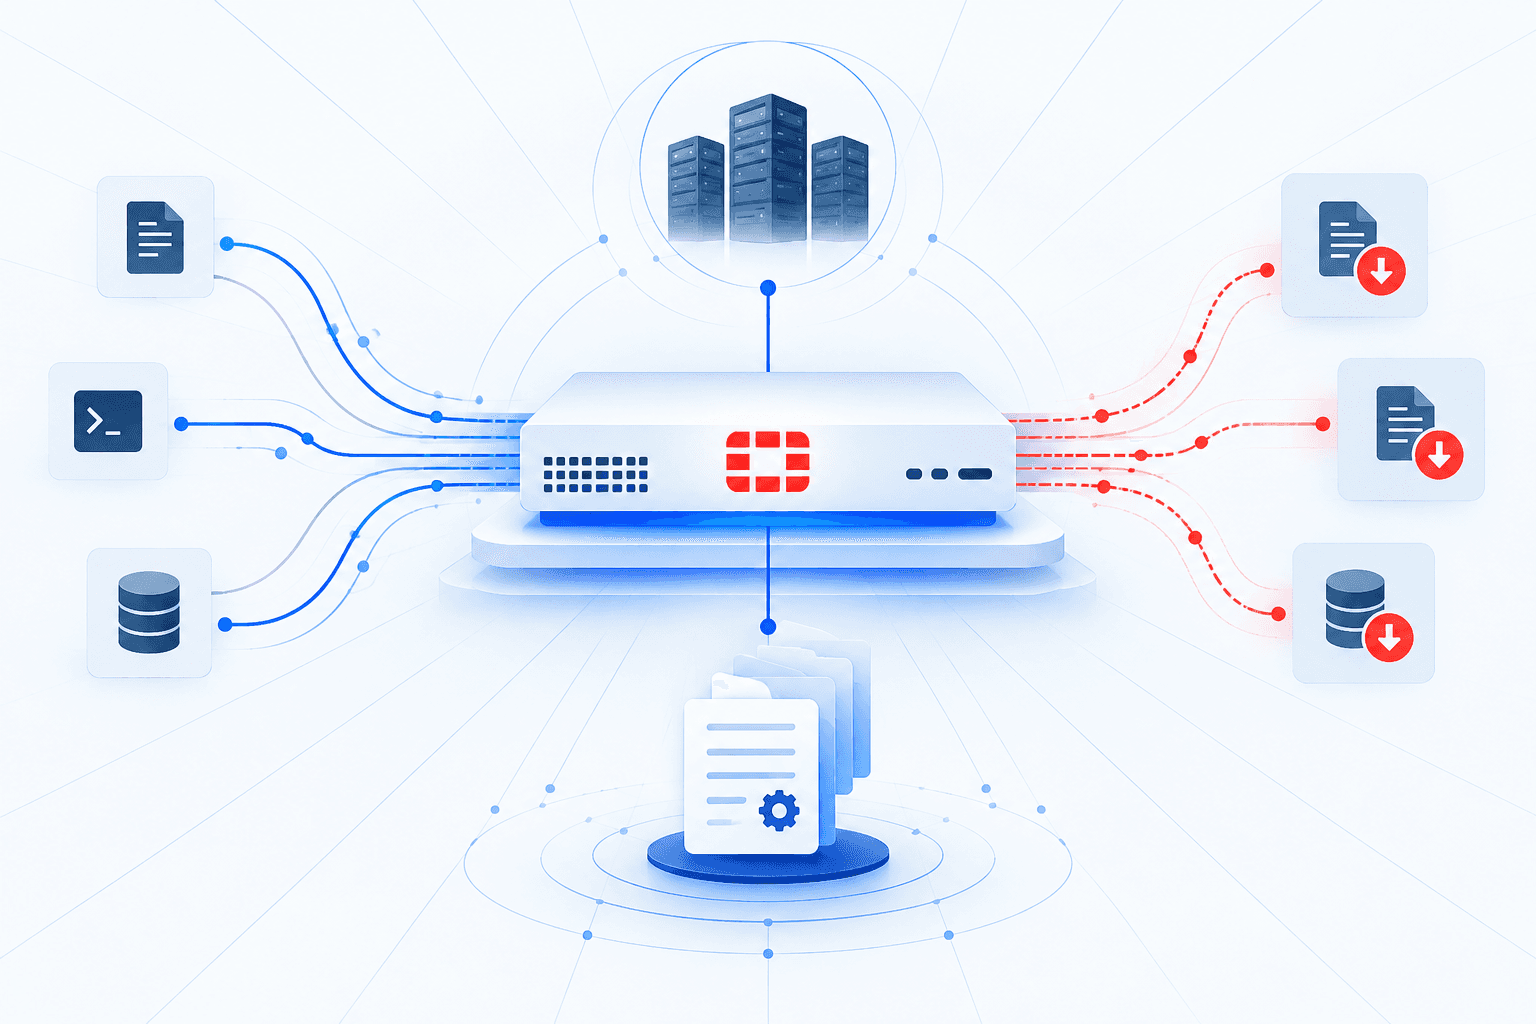
Malicious activity targeting Fortinet appliances involved payload retrieval and suspected configuration-data exfiltration, with September 2024 traffic likely linked to exploitation of CVE-2024-47575. The missing-authentication vulnerability permits remote command execution on FortiManager and was separately the subject of a Mandiant zero-day exploitation report. Darktrace observed attackers connecting to likely FortiManager devices on port 541, retrieving JavaScript content from 45.32.41[.]202/dom.js, and sending apparent compressed configuration archives to external /file endpoints. Encrypted traffic prevented confirmation of the exploit mechanism.

Darktrace also identified June 2024 activity using overlapping infrastructure but different connection patterns and a shell-script payload named ver.sh. Those differences suggest potentially separate campaigns or actors sharing infrastructure, rather than a conclusively linked operation. Suspected theft of configuration data creates a risk beyond the initial compromise: any exposed credentials could enable renewed access or persistence after patching. Organizations should prioritize remediation of vulnerable FortiManager systems, investigate suspicious management-port connections and outbound transfers, and assess whether configuration exposure requires credential rotation.
This is being exploited nowSee which actors are running it and whether you're in range.
Check your exposure
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

5 events · Jun 2024 – Sep 2024
  1. Reported Jan 1, 202611mo ago

    Darktrace opens an investigation while reviewing Fortinet vulnerability updates

    Darktrace began investigating Fortinet exploitation while reviewing October vulnerability updates concerning CVE-2024-23113. Its retrospective analysis identified potentially distinct June and September 2024 activity clusters with overlapping infrastructure.

    Post-Exploitation Activities on Fortinet Devices: A Network-Based Analysis
  2. Reported Jan 1, 202611mo ago

    Fortinet PSIRT discloses vulnerabilities affecting the FGFM daemon

    Fortinet's Product Security Incident Response Team disclosed vulnerabilities affecting the daemon implementing the FortiGate to FortiManager protocol. The reference discusses CVE-2024-23113, a format-string vulnerability permitting remote command execution, and CVE-2024-47575, a missing-authentication vulnerability affecting FortiManager.

    Post-Exploitation Activities on Fortinet Devices: A Network-Based Analysis
  3. Sep 2024

    September FortiManager intrusions retrieve JavaScript and apparently steal configurations

    Between September 22 and September 23, 2024, Darktrace observed anomalous activity involving incoming connections to likely FortiManager devices on port 541, retrieval of 45.32.41[.]202/dom.js, and apparent compressed-data uploads to external /file endpoints. Darktrace assessed that the activity likely involved CVE-2024-47575 exploitation and configuration-data theft, although encrypted traffic prevented confirmation of the exploit.

    Post-Exploitation Activities on Fortinet Devices: A Network-Based Analysis
  4. Jun 2024

    A different June activity cluster retrieves the ver.sh shell script

    Darktrace observed another June 2024 pattern involving incoming connections from 158.247.199[.]37, outbound requests containing apparent victim public IP addresses, and retrieval of ver.sh from 45.32.41[.]202. The differing behavior potentially indicated a separate campaign or another actor sharing infrastructure.

    Post-Exploitation Activities on Fortinet Devices: A Network-Based Analysis
  5. Jun 2024

    Fortinet devices receive suspicious connections and apparently exfiltrate data

    Between June 23 and June 25, 2024, Darktrace observed connections from 45.32.41[.]202 to Fortinet devices on ports 541 or 443, followed by callbacks and apparent data exfiltration through HTTP POST requests. The uploads targeted /file endpoints on 158.247.199[.]37 and 195.85.114[.]78.

    Post-Exploitation Activities on Fortinet Devices: A Network-Based Analysis
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Vulnerabilities

1 linked

Affected products

1 linked
Fortimanager

Observables

4 linked

Indicator values are masked on this page. See the values in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Correlate live exploitation activity against the software you actually run, and see where you're exposed.
See Who's Exploiting This
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.