Actively Exploited Flo Forms Flaw Lets Low-Privilege Users Inject Stored XSS
Active Exploitation · 2 sources · Updated 14d ago · First seen Mar 16, 2021
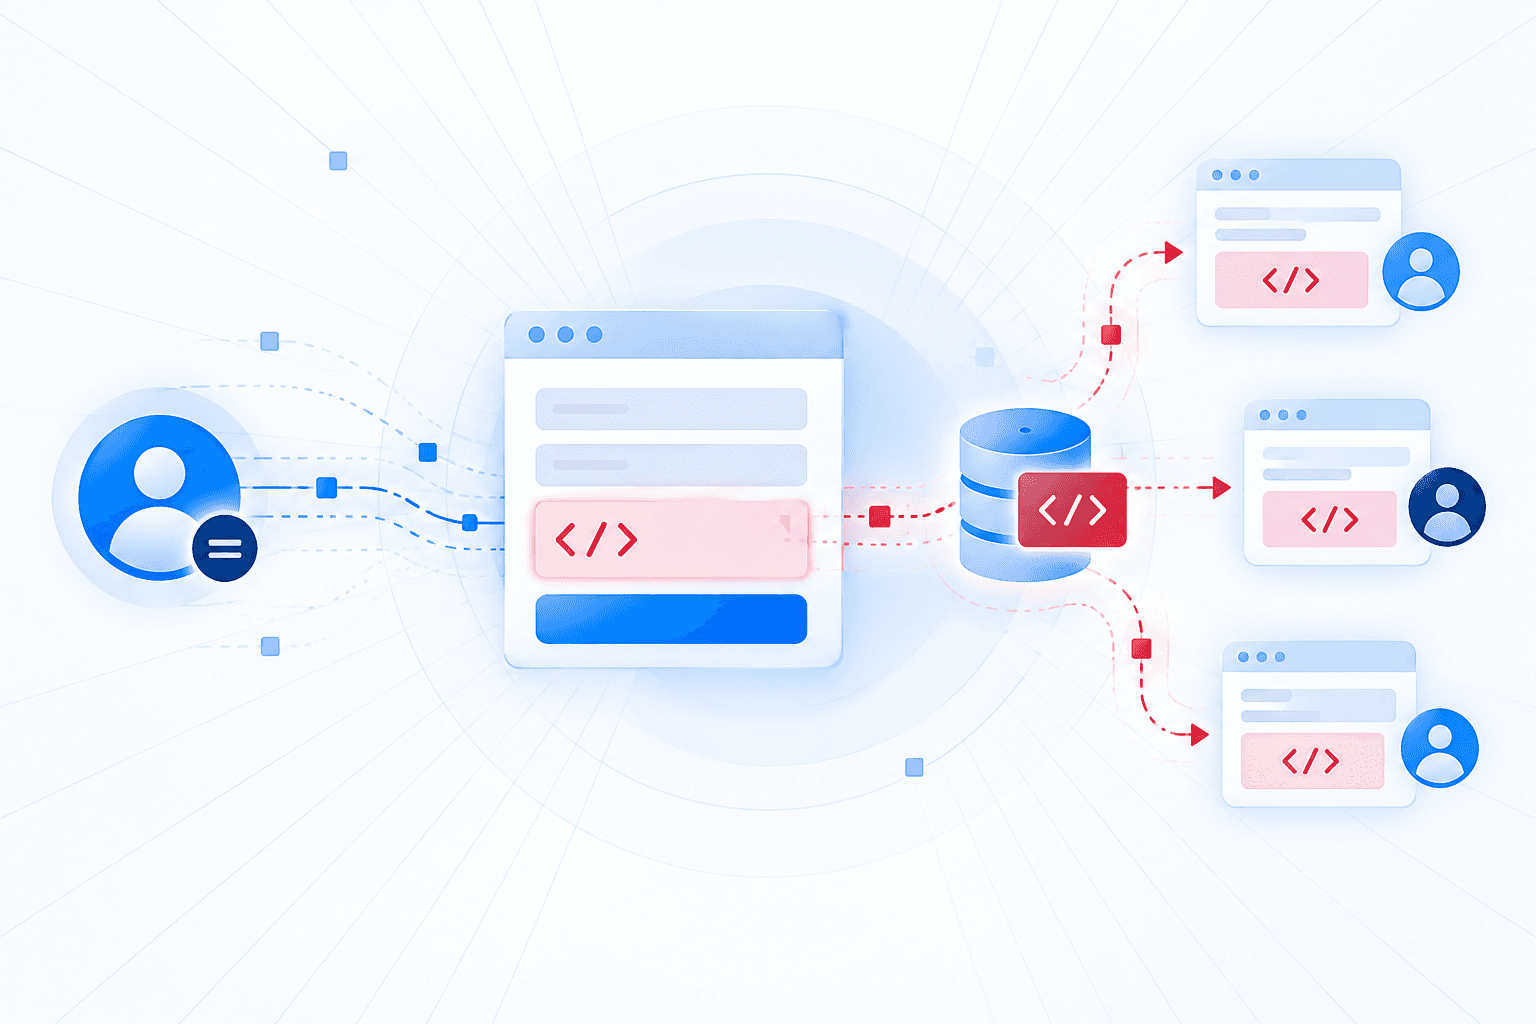
A critical broken access control vulnerability in the WordPress Flo Forms plugin allowed authenticated, low-privilege users to change plugin options and inject malicious JavaScript into the administrative backend. Tracked as CVE-2021-4367, the flaw affects versions earlier than 1.0.36 and involves the flo_import_forms_options AJAX action. WPScan lists the vulnerability as actively exploited, with a CVSS score of 9.9; NinTechNet also reported a zero-day fix for the plugin.
Version 1.0.36 fixes the vulnerability. Organizations running affected versions should upgrade to that release or a newer supported version and review imported form options for unauthorized changes or injected JavaScript. Because exploitation requires authentication but not administrator privileges, sites with untrusted low-privilege accounts are exposed. Stored scripts in the backend could execute when an administrator views affected content, putting privileged sessions at risk.