Censys Finds 14,004 Internet-Exposed Healthcare Hosts as Hacking Dominates U.S. Breaches
Sector Threat Intelligence · 4 sources · Updated 18d ago · First seen Feb 21, 2024
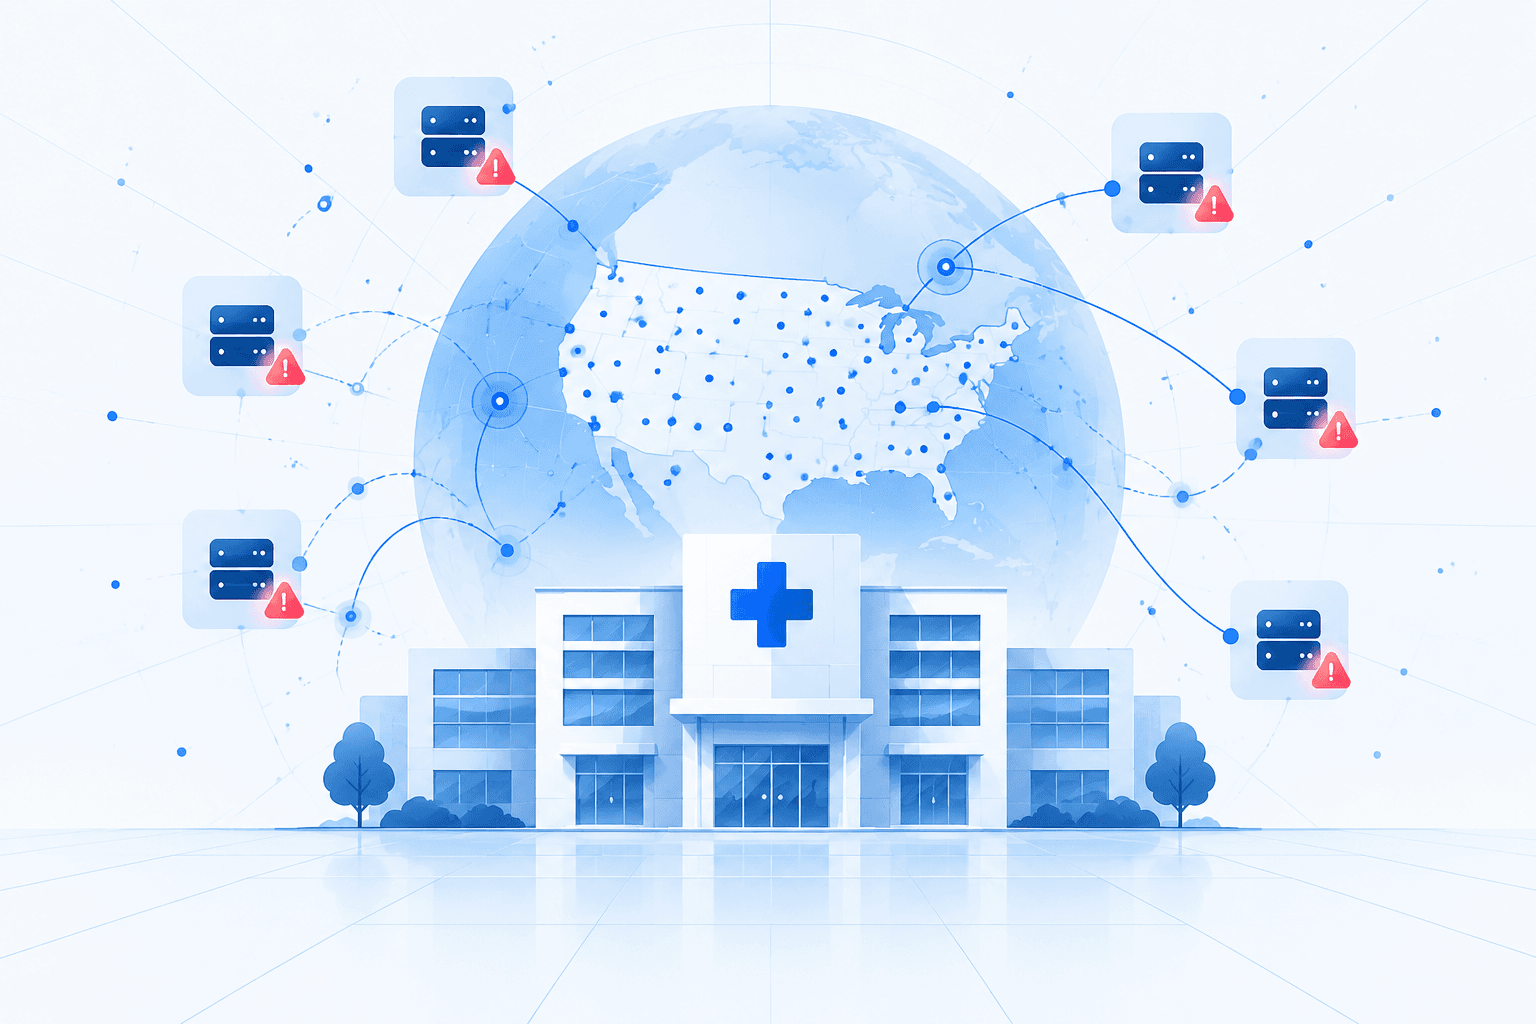
Censys identified 14,004 unique public IP addresses exposing healthcare devices and data systems, including 6,884 in the United States and 1,476 in India. Its survey found 5,100 DICOM hosts, 4,031 electronic medical or health record interfaces, 2,530 PACS login portals, and 2,520 Mirth Connect login pages. Many observed Orthanc servers permitted unauthenticated access to medical imaging databases. Other exposed services presented login gateways to sensitive information. The research measured internet exposure, not confirmed vulnerabilities, and did not assess whether EMR/EHR interfaces enforced multifactor authentication or other controls.
HIPAA Journal’s analysis of HHS breach reports affecting at least 500 records shows hacking accounted for 79.7% of reported breaches in 2023, while 2024 had fewer breaches but substantially more affected individuals, largely because of the Change Healthcare ransomware incident. That attack disrupted pharmacy and prescription processing; UnitedHealth’s CEO later told Congress that attackers used compromised credentials to access a Citrix portal lacking MFA, superseding the cited article’s initial unconfirmed speculation about an RDP vulnerability and LockBit involvement. The references do not establish a connection between the Censys findings and that attack. Censys recommended stronger access controls, appropriate firewall and VPN restrictions, encryption reviews, and continuous external attack-surface monitoring; the breach statistics also highlight growing regulatory attention to risk analysis.