Velvet Ant Exploits Cisco NX-OS Zero-Day and F5 Appliances for Persistent Access
Active Exploitation · 3 sources · Updated 1mo ago · First seen Aug 24, 2024
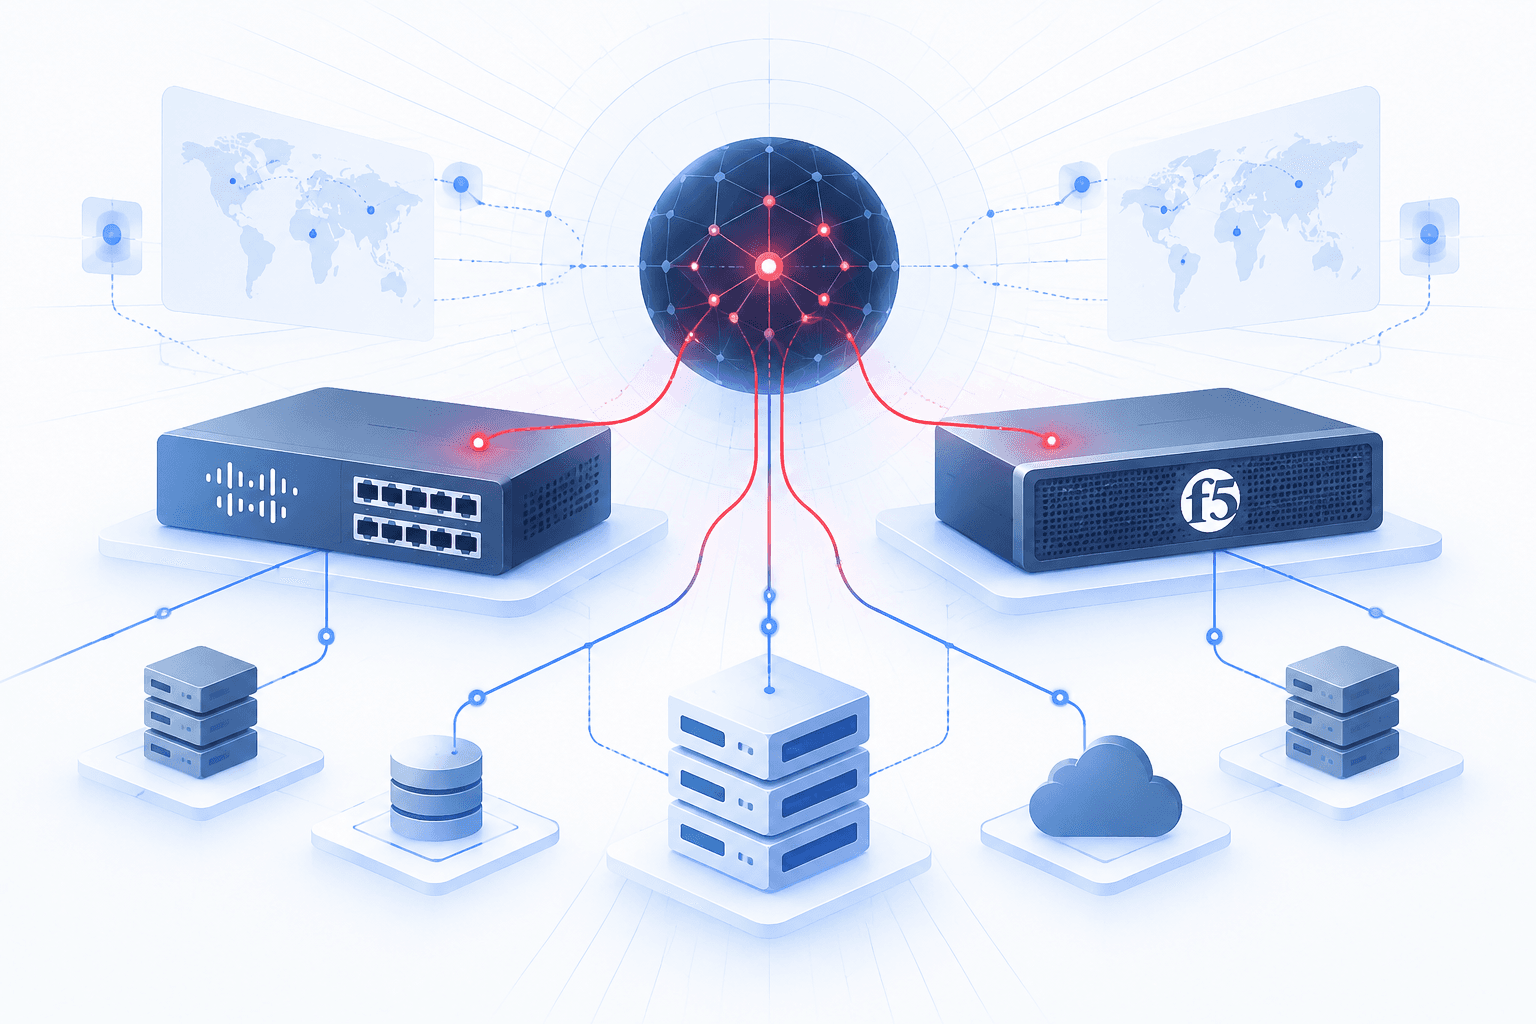
Velvet Ant, a threat group identified by Sygnia as based in China, exploited CVE-2024-20399 as a zero-day to compromise Cisco Nexus switches running NX-OS. The command-injection vulnerability requires existing administrator-level access and lets attackers escape the NX-OS management layer to execute code in the underlying Linux operating system. Subsequent research identified the VelvetShell malware toolkit, which provides remote access, file transfers, and tunneling or proxying of network communications.
The switch compromises followed findings that Velvet Ant used compromised internet-facing F5 load balancers for persistence and command-and-control access to internal systems during a prolonged intrusion at a large organization. Cisco released patches for CVE-2024-20399 on July 1, 2024, and CISA added it to its Known Exploited Vulnerabilities catalog the following day. Defenders should prioritize patching affected switches, investigate privileged-access activity, and assess F5 appliances and other network infrastructure for persistent compromise rather than relying solely on endpoint monitoring.