Commvault Azure Intrusion Linked to Patched Flaw May Have Exposed M365 Credentials
Active Exploitation · 3 sources · Updated 21d ago · First seen May 1, 2025
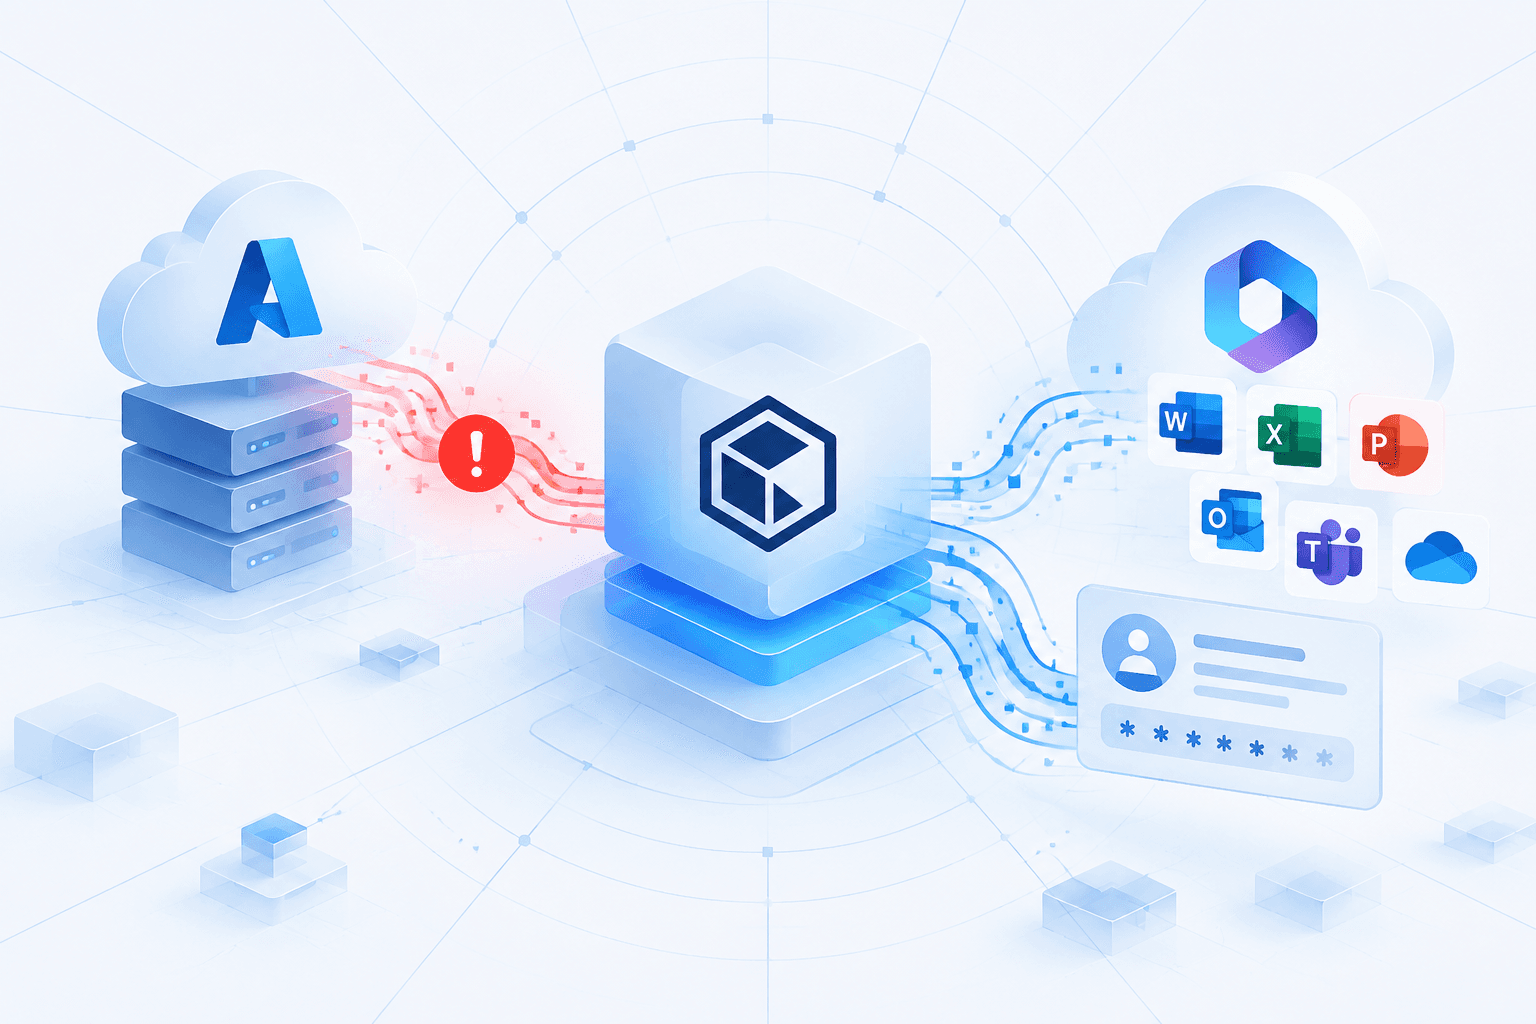
Commvault disclosed unauthorized activity in its Azure environment attributed to a suspected nation-state threat actor after Microsoft notified the company on February 20, 2025. Its investigation identified exploitation of a subsequently patched zero-day and unauthorized access affecting a handful of customers. A later update said the actor may have accessed a subset of application credentials that certain customers use to authenticate to Microsoft 365. Commvault contacted affected customers, rotated affected credentials, strengthened monitoring, and engaged cybersecurity experts and law enforcement. The company reported no unauthorized access to customer backup data it stores and protects, and no material impact on operations or service delivery.
Commvault identified CVE-2025-3928 as the known vulnerability associated with its advisory. The flaw affects all supported software versions and allows authenticated attackers to create and execute webshells, potentially compromising webservers. Exploitation requires an internet-accessible environment, compromise through an unrelated avenue, and legitimate Commvault credentials; unauthenticated access is not exploitable. Software customers should immediately install the resolved maintenance release on CommServe, Web Servers, and Command Center; client computers are unaffected, and Commvault deploys SaaS patches automatically. Customers using custom Microsoft 365 applications were also advised to rotate credentials, validate application permissions, enforce conditional access and least privilege, and review Entra ID audit logs.