Tortilla Exploits Exchange ProxyShell Flaws to Deploy Babuk Ransomware
Active Exploitation · 5 sources · Updated 1mo ago · First seen Oct 12, 2021
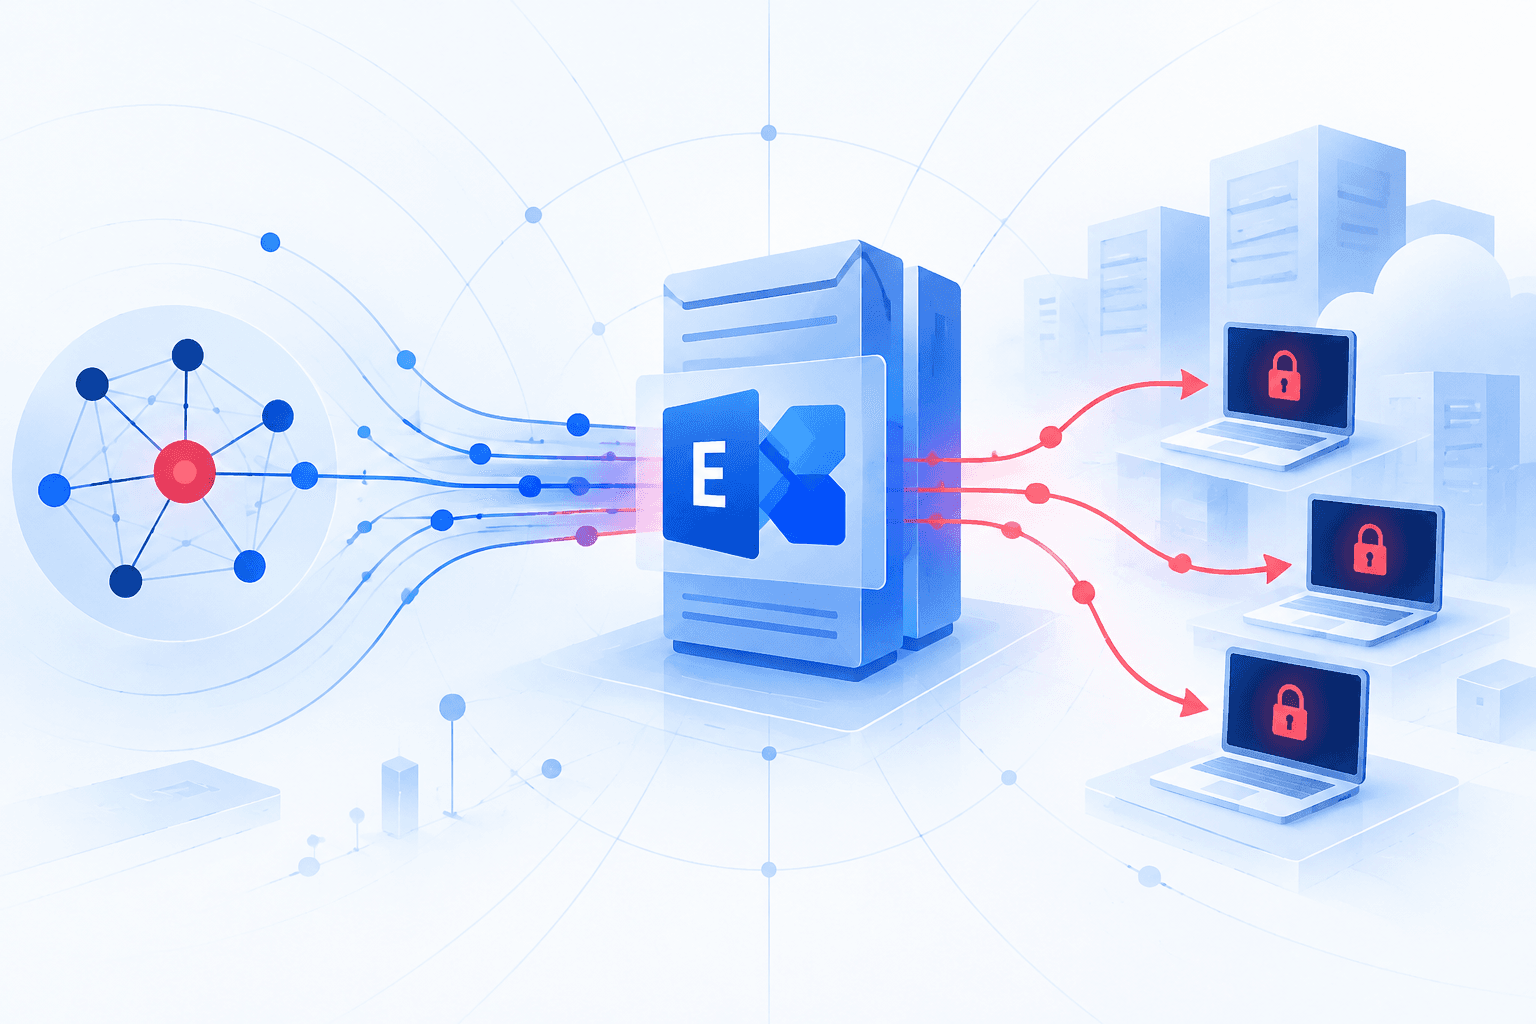
The Tortilla threat actor targeted vulnerable Microsoft Exchange servers to deploy a Babuk ransomware variant in a campaign Cisco Talos first observed on October 12, 2021. Infections primarily affected U.S. victims, with additional cases in seven other countries. Talos assessed with moderate confidence that the attackers gained initial access by exploiting ProxyShell vulnerabilities and deployed the China Chopper webshell. The campaign used the Babuk ransomware family, which McAfee Labs had documented earlier that year.
The infection chain downloaded an intermediate unpacker from pastebin.pl, decrypted the ransomware in memory, and injected it into the AddInProcess32 process to encrypt files on the server and mounted drives. At the time of reporting, the available free Babuk decryptor did not support this variant, limiting recovery options for victims. Researchers recommended patching Exchange, enabling behavioral protections, and monitoring for backup disruption and suspicious system activity. Defenders investigating affected servers should also look for China Chopper webshells and evidence of the reported unpacker and process-injection chain.