LapDogs Threat Hunt Finds Suspected ASUS Router Relays and Energy-Sector Exposure
Threat Actor Intelligence · 2 sources · Updated 20d ago · First seen Sep 24, 2025
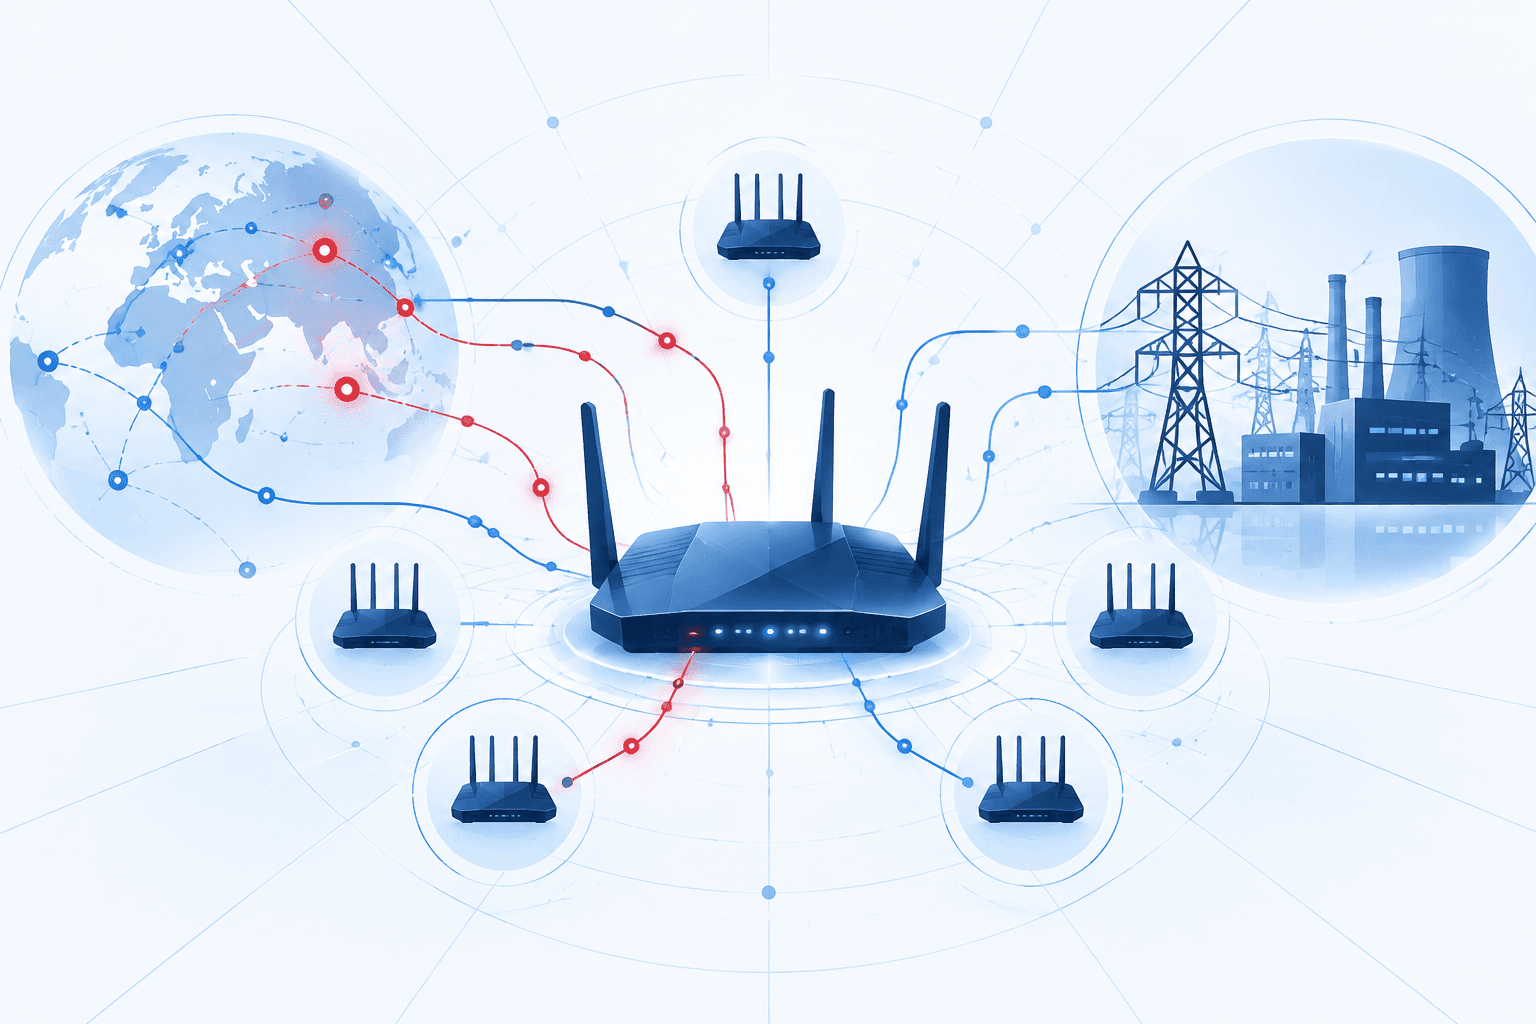
Expel identified customer authentication traffic originating from third-party devices associated with LapDogs, an Operational Relay Box network that uses the ShortLeash backdoor and self-signed TLS certificates impersonating the Los Angeles Police Department. The hunt uncovered a possible relay node in Hong Kong and apparently infected ASUS routers in the United States, expanding the suspected device footprint beyond previously reported Ruckus and Buffalo Technology AirStation targets. One user authenticating through an affected router worked for a supplier of components used in U.S. energy-sector critical infrastructure. SecurityScorecard attributed the network’s use to Chinese threat actors with moderate confidence, citing Mandarin-language documentation and victim analysis.
GreyNoise separately reported a stealthy backdoor campaign affecting thousands of ASUS routers, but the supplied reporting does not establish a connection to LapDogs. Expel observed activity consistent with normal user behavior and did not confirm exploitation of specific ASUS vulnerabilities or actual data exfiltration. Investigators notified affected customers and the Department of Energy about potential exposure. Defenders should patch SOHO routers, disable unnecessary externally accessible services such as ASUS AiCloud, and monitor for the network’s distinctive certificate metadata and unusual HTTP responses on ephemeral ports.