Google Play Spyware Exploits Android Binder Flaw, Tentatively Linked to SideWinder
Active Exploitation · 3 sources · Updated 1mo ago · First seen Jan 6, 2020
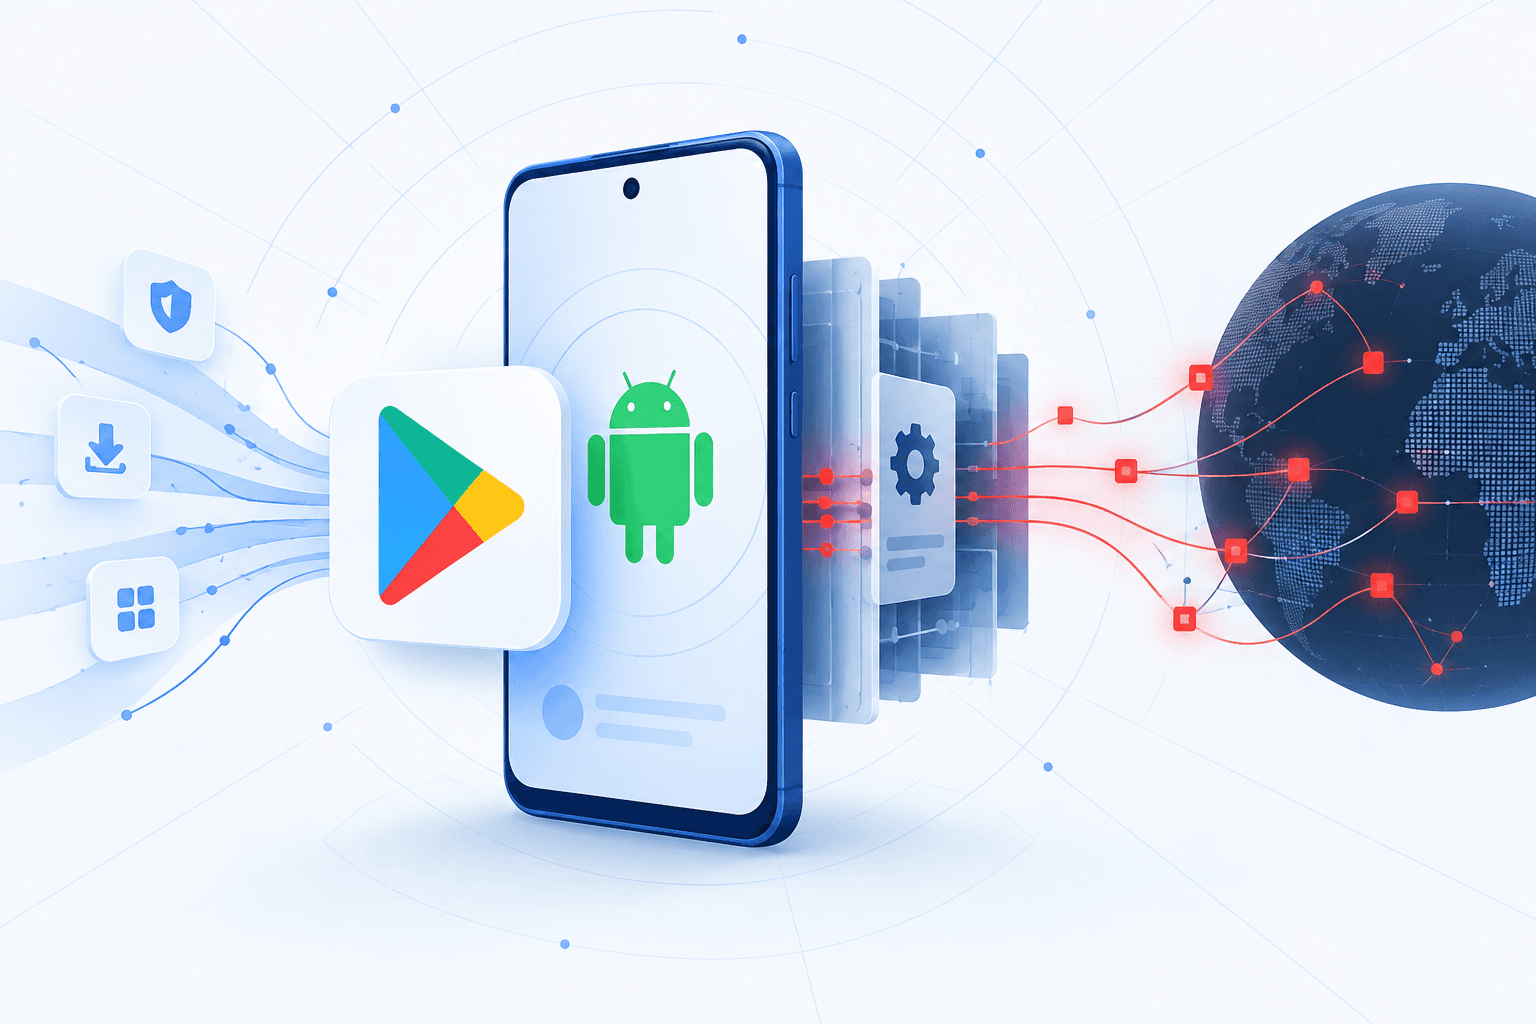
Trend Micro identified three malicious Google Play apps—Camero, FileCrypt Manager, and callCam—that worked together to compromise Android devices and steal information. Camero obtained root privileges using the Android Binder use-after-free vulnerability CVE-2019-2215 or MediaTek-SU exploits. FileCrypt Manager instead abused accessibility permissions to install the callCam spyware while concealing activity behind an overlay. The payload collected device details, files, screenshots, account information, and data from multiple applications, then encrypted the stolen information before transmitting it to command-and-control servers. Google subsequently removed the apps from its store.
Trend Micro tentatively attributed the campaign to SideWinder based on suspected infrastructure overlap; the attribution was not conclusive. Kaspersky had identified SideWinder among emerging Asian threat actors in its Q1 2018 reporting. Google Project Zero separately documented an in-the-wild Android Binder exploit in November 2019, preceding Trend Micro’s January 2020 report on the malicious apps. The campaign demonstrates how attackers can combine privilege-escalation exploits with accessibility abuse to deliver spyware through an official app marketplace. Defenders should check for the named apps, apply vendor security updates addressing CVE-2019-2215, and restrict unnecessary accessibility permissions.