Telegram Android EvilVideo Flaw Disguises Malicious APKs as Video Attachments
Vulnerability Disclosure · 2 sources · Updated 28d ago · First seen Jul 11, 2024
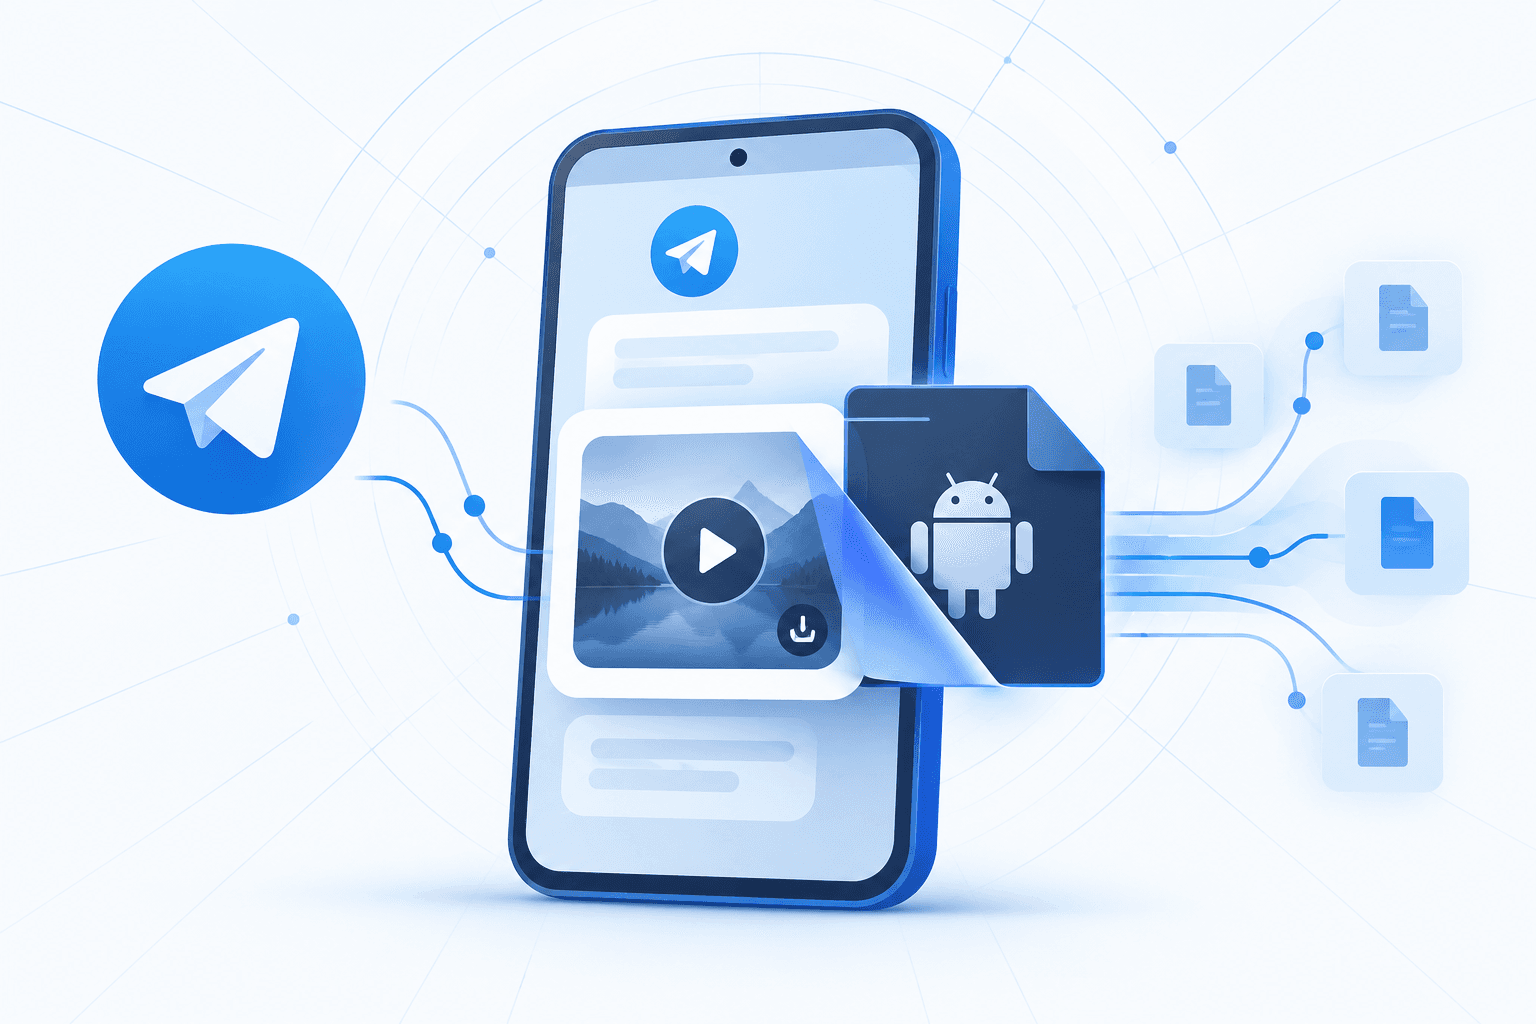
ESET discovered EvilVideo, a zero-day vulnerability in Telegram for Android versions 10.14.4 and earlier, after an exploit was advertised on an underground forum. The exploit disguised malicious Android applications as video attachments shared through Telegram channels, groups, and chats. Trying to play an attachment triggered a legitimate Telegram prompt to use an external player, steering users toward installing the malicious APK. Downloading the attachment alone did not install the malware; the attack depended on further user interaction.
ESET verified the seller’s sample, detected as Android/Spy.SpyMax.T, but could not independently recreate the exploit. Tests did not reproduce the attack on Telegram Web or Telegram Desktop for Windows. Telegram fixed the vulnerability in version 10.14.5, released July 11, 2024, following ESET’s disclosure. The initial-access mechanism aligns with MITRE ATT&CK’s mobile Exploitation for Initial Access (T1664) technique. Organizations should ensure Android devices run a current Telegram release and warn users against installing applications presented as players for chat attachments.