Loading story…
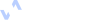
Trojans and infostealers accounted for 54.2% of 37,898 macOS malware samples processed by Point Wild in Q3 2026, outpacing potentially unwanted applications and backdoors. Its threat report identifies social engineering—particularly ClickFix lures that persuade users to paste malicious commands into Terminal—as a leading delivery mechanism. Infostealers including Odyssey, Atomic macOS Stealer (AMOS), MacSync, SHub, and ClickLock target browser passwords, cryptocurrency wallets, cloud credentials, SSH keys, and developer assets. Campaigns use trusted-brand and developer-tool impersonation, compromised brands, and malicious installers to reach developers, creatives, and knowledge workers, potentially extending access from individual Macs into corporate environments. Point Wild also highlighted developer-focused supply-chain attacks and DPRK-linked social engineering involving blockchain-based command-and-control.
Point Wild reported active exploitation of CVE-2026-65400, described as a critical unauthenticated macOS Screen Sharing flaw, to gain root access and deploy the XMRig cryptocurrency miner. It also described a chain of legitimate macOS behaviors that could disable Kandji and CrowdStrike Falcon protections without administrator credentials or a kernel exploit; the Kandji issue was assigned CVE-2026-39118. Apple’s macOS Tahoe 26.4 Terminal-paste warning offers only partial protection because fake installers and malicious applications remain viable delivery routes. Recommended enterprise defenses include stronger credential management, scrutiny of Terminal-based installation instructions, monitoring impersonation infrastructure, and applying security controls consistently across Mac fleets.
See which actors are running it and whether you're in range.
17 events from the most recent confirmed update back to the earliest known activity.
A hijacked verified HBO Max Reddit account reportedly ran paid advertisements directing users to a fake macOS application. The campaign delivered an infostealer through ClickFix.
Attackers reportedly uploaded malicious versions of three Rust packages to crates.io. The packages delivered a macOS RAT and credential stealer that collected developer credentials, wallet data, browser profiles, and host information, with persistence established through a LaunchAgent.
Apple patched CVE-2026-65400, a pre-authentication Screen Sharing/VNC flaw that reportedly allowed unauthenticated attackers to obtain root-level remote code execution. The report identifies macOS Tahoe 26.6.1, Sequoia 15.7.9, and Sonoma 14.8.9 as the fixed versions.
Apple patched Screen Sharing vulnerabilities CVE-2026-43760 and CVE-2026-43777 in July 2026. Point Wild reported that neither vulnerability had been confirmed exploited.
XCSSET reportedly began spreading through legitimate Xcode projects from April 2026 onward. Its capabilities included credential theft, browser hijacking, clipboard monitoring, and data exfiltration.
ClickFix techniques emerged in 2024, using deceptive workflows to persuade users to execute commands or install malware. The techniques subsequently gained momentum in 2025 and 2026.
Point Wild's Q3 2026 Mac Malware Trend Report reported processing 37,898 macOS malware samples from July through September, with trojans and infostealers accounting for 20,524 samples, or 54.2%. Potentially unwanted applications accounted for 40.8%, while backdoors accounted for 2.9%.
Point Wild reported that standard macOS users could chain legitimate operating-system behaviors to disable Kandji and CrowdStrike Falcon without administrator credentials or a kernel exploit. The Kandji case was assigned CVE-2026-39118.
Apple's macOS Tahoe 26.4 reportedly introduced a warning that blocks or warns on suspicious clipboard-triggered Terminal pastes. Point Wild characterized it as a partial ClickFix mitigation that does not protect against trojanized installers or fake application campaigns.
Point Wild's Zulfikar Ramzan cited the ChainDrop incident as a large-scale npm supply-chain attack affecting more than 400 packages.
Sapphire Sleet reportedly targeted finance, cryptocurrency, and blockchain organizations through fake job interviews, recruiter outreach, and fraudulent technical-fix requests.
Point Wild linked an EtherHiding macOS implant to DPRK Contagious Interview tradecraft with moderate confidence. The implant resolved its command-and-control address from a Polygon smart contract using eth_call and used a LaunchAgent for persistence.
ImpersonAlly documented impersonation involving Cursor and observed similar patterns involving ChatGPT Atlas, Ahrefs, and Google Ads. The article also described a malicious website copying GitHub's design, explicitly noting that no GitHub account was compromised.
ClickLock Stealer reportedly infected more than 100 victims across 33 countries within two months. Its delivery relied on ClickFix pages hosted on compromised WordPress sites.
Point Wild described a campaign using more than 85 phishing domains impersonating Homebrew, TradingView, and LogMeIn. The sites delivered Odyssey Stealer or AMOS through base64-encoded Terminal commands.
According to Point Wild, Dutch NCSC and Microsoft confirmed active exploitation of CVE-2026-65400. Attackers reportedly obtained root access, installed SSH keys, erased logs, modified firewall rules, and deployed XMRig cryptomining malware.
The three malicious Rust packages reportedly remained available on crates.io for approximately two hours before removal.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. See the values in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
Correlate live exploitation activity against the software you actually run, and see where you're exposed.
3 references tracked. Mallory keeps watching after this page renders.
Map indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Attackers are increasingly compromising macOS systems through **ClickFix** and related social-engineering lures that trick users into pasting malicious commands into Terminal, often behind fake Cloudflare checks, bogus troubleshooting steps, fraudulent support messages, or compromised websites. A large campaign tied to hundreds of hacked WordPress sites served platform-specific payloads and used the **Polygon** blockchain to hide command-and-control locations, while the macOS payload ran largely in memory, harvested Keychain data, browser information, SSH keys, screenshots, and other files, then staged stolen data in `/tmp/osalogging.zip` before exfiltrating it. Researchers said the technique does not rely on a macOS software flaw, but on convincing victims to execute attacker-supplied commands themselves. Threat reporting indicates the tactic has become a dominant initial-access method against Mac users, especially cryptocurrency holders and developers, and that recent Apple paste warnings in Terminal have already been bypassed through Script Editor abuse. Separate intrusion research linked cryptocurrency-focused activity to malware families including **DEEPBREATH**, **SUGARLOADER**, and **CHROMEPUSH**, showing how post-compromise tooling on macOS can escalate from social engineering to broad credential and data theft by targeting `TCC.db`, Keychain contents, Chromium-based browsers, Telegram data, and Apple Notes. Security teams are being urged to prioritize behavioral detection, cross-platform response, and user controls that prevent unverified command execution on Macs.
Jul 16, 2026
Microsoft reported that **information-stealing malware activity is expanding from Windows to macOS**, driven by campaigns observed since late 2025 that rely on social engineering and cross-platform tooling. The activity includes **ClickFix-style prompts** and **malicious DMG installers** that deliver macOS-focused infostealer families such as **Atomic macOS Stealer (AMOS)**, **MacSync**, and **DigitStealer**, with operators leveraging **fileless execution**, **native macOS utilities**, and **AppleScript automation** to evade defenses and automate collection. Initial access commonly starts with **malicious search ads (e.g., Google Ads)** that redirect users to fake sites impersonating legitimate tools and then trick victims into running “fix” steps or installing trojanized software. The malware is assessed to target high-value data including browser credentials and session cookies, **iCloud Keychain** contents, crypto wallet data, and **developer secrets**; Microsoft also highlighted growing use of **Python-based stealers** distributed via phishing for rapid adaptation across heterogeneous environments, citing **PXA Stealer** (linked to Vietnamese-speaking actors) as an example used in late-2025 campaigns with persistence mechanisms such as registry `Run` keys or scheduled tasks and **Telegram** used for command-and-control.
Jun 29, 2026
Researchers reported multiple social-engineering campaigns targeting macOS users with **fake CAPTCHA** and **ClickFix** lures that trick victims into copying and pasting malicious commands into Terminal, shifting execution to the user and bypassing traditional app-download protections. One campaign delivered **Atomic macOS Stealer (AMOS)** through trojanized cracked applications and malicious Terminal instructions, stealing credentials, browser data, cryptocurrency wallets, Telegram data, VPN profiles, keychain contents, Apple Notes, and files from common user folders before compressing and exfiltrating them over HTTP/HTTPS. Trend Micro separately documented multistage fake CAPTCHA attacks that also led to infostealers and remote-access trojans, underscoring the broader use of human-verification themes to launch malware chains. A separate July 2026 macOS campaign used a fake **TrustKey** verification page on Cloudflare Pages, a Cloudflare Worker, and an AppleScript-based loader to install a persistent backdoor named **`bmodule`** via LaunchAgent persistence. The malware dynamically resolved live command-and-control infrastructure from a **Polygon** smart contract using an **EtherHiding** technique, then fingerprinted hosts, phished macOS login passwords, and fetched tasks to deploy AMOS variants, an interactive shell, or an **XMRig** cryptominer. Apple said **macOS Sequoia** has updated runtime protections, while incident reporting shows Terminal-based social-engineering chains remain effective because they rely on users to execute the malicious commands directly.
Aug 28, 2026