TargetCompany Linux Ransomware Targets VMware ESXi and Exfiltrates Victim Data
Malware Intelligence · 1 source · Updated 1mo ago · First seen Jun 5, 2024
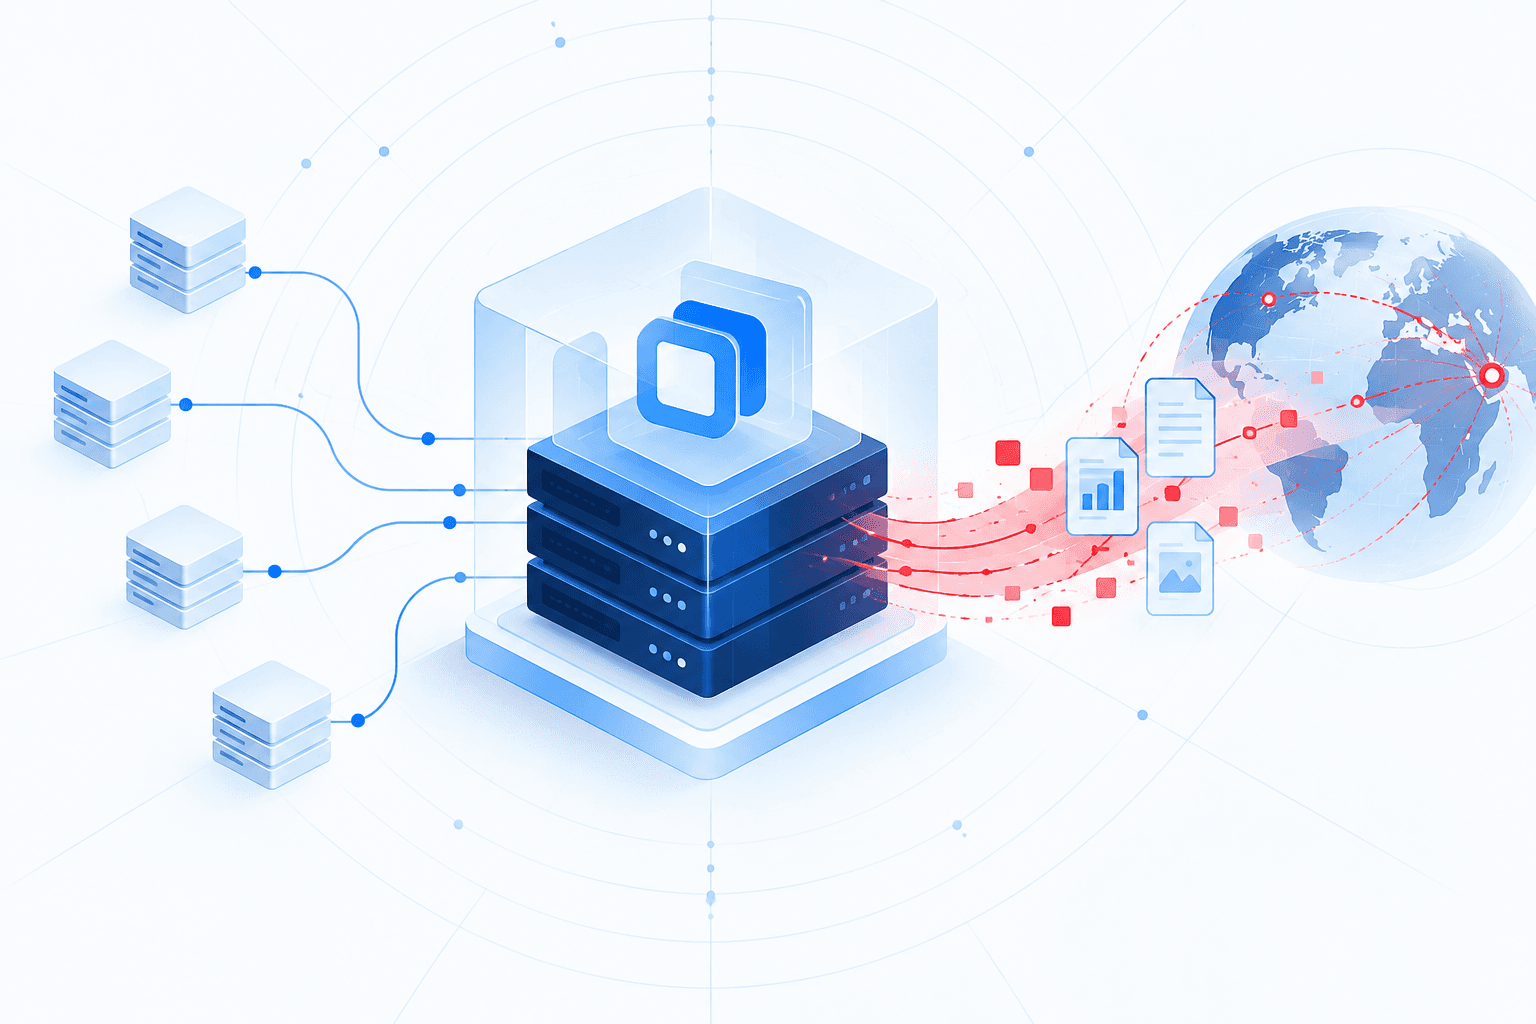
Trend Micro identified a new Linux variant of TargetCompany ransomware targeting VMware ESXi environments. The malware requires root privileges and checks for the system name vmkernel to identify ESXi hosts. A custom shell script delivers and executes the payload, which encrypts files, appends the .locked extension, and drops a ransom note named HOW TO DECRYPT.txt. Researchers associated the sample with the affiliate known as vampire.
Both the ransomware payload and its delivery script exfiltrate victim information to two different servers, potentially giving the attackers redundancy. The script deletes the ransomware executable after execution, reducing evidence available to investigators. Targeting virtualized infrastructure could amplify operational disruption and pressure victims to pay; defenders should prioritize securing ESXi administrative access, monitoring unexpected root-level script execution and outbound connections, and maintaining isolated, tested backups of virtual machines.