
Loading story…
Varonis Threat Labs discovered AvisLoader, a Windows malware loader, on an exposed staging server containing a ClickFix lure, supporting tools, and an operator management panel called Command Center. The lure impersonated a DocuSign signing request and presented fake Cloudflare verification to persuade visitors to execute a command that retrieved code through a Cloudflare Quick Tunnel. AvisLoader uses the encrypted Tox peer-to-peer network for operator commands and payload delivery, reducing its reliance on fixed command-and-control domains or server addresses and making infrastructure-based disruption more difficult.
The recovered Command Center supports host profiling, targeted shell tasks, and file distribution. Other recovered files showed evidence of shortcut-based persistence, a helper referencing a User Account Control bypass technique, and a process-hiding DLL; successful privilege elevation and deployment of that DLL were not established. Defenders should prioritize detecting suspicious command execution associated with verification prompts, unexpected shortcut modifications, and Tox traffic on endpoints where the application has no approved business use.
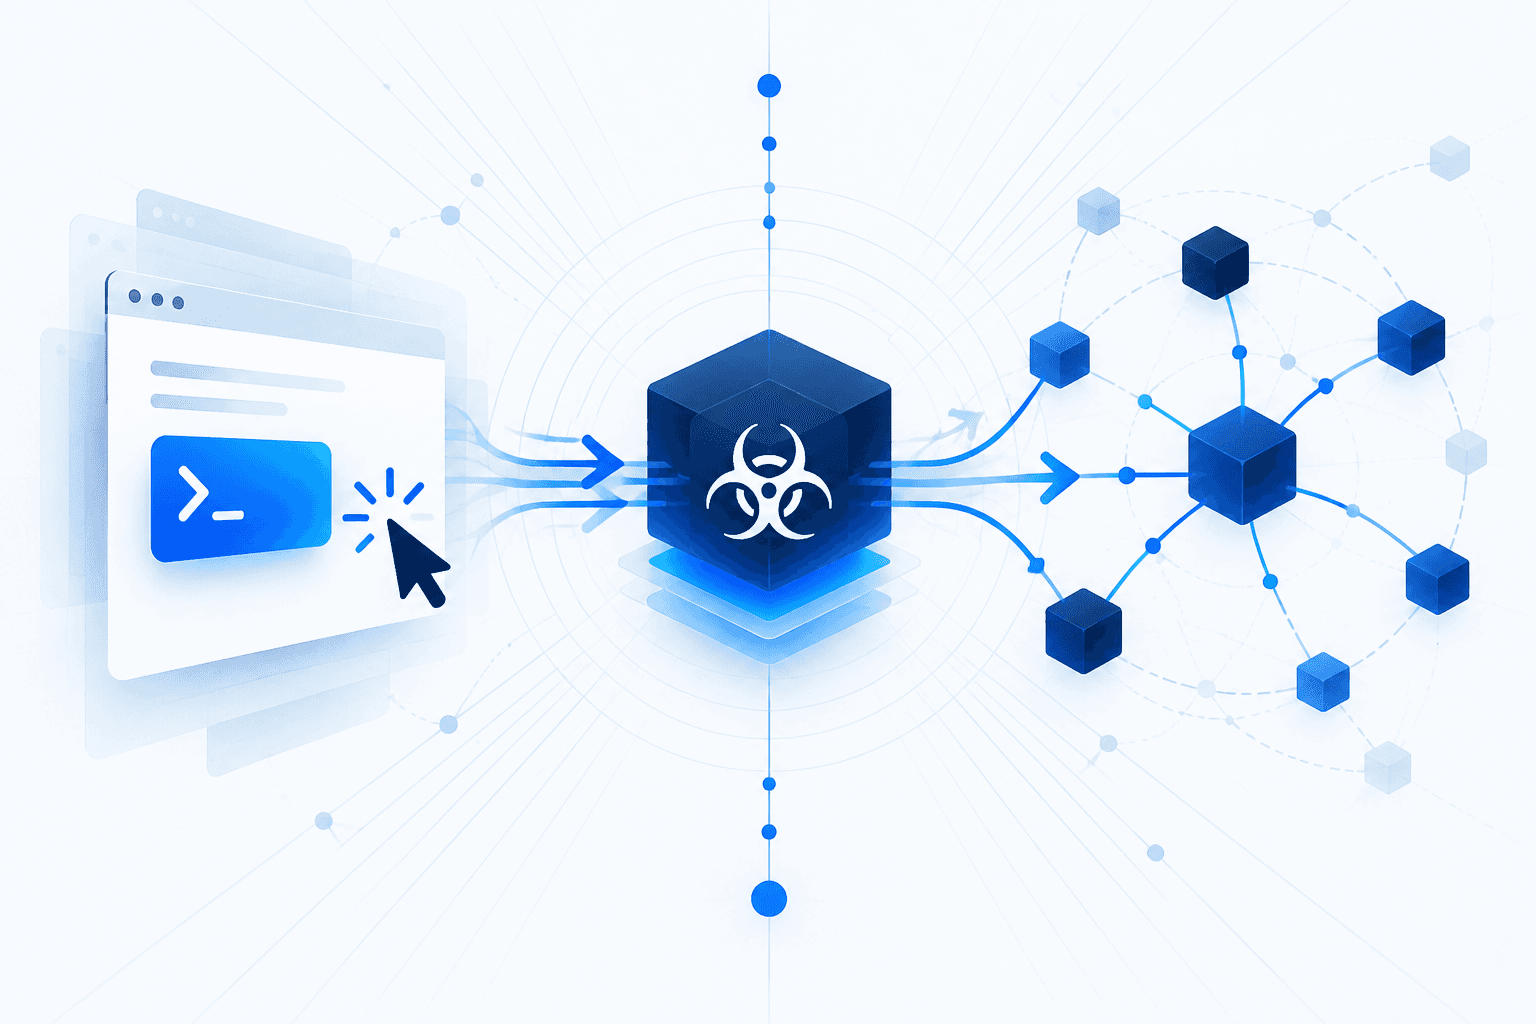
Pull IOCs and campaign context straight into your stack.
2 events from the most recent confirmed update back to the earliest known activity.
Varonis Threat Labs discovered AvisLoader on an exposed staging server alongside supporting tools, its Command Center, and a DocuSign-themed lure that used fake Cloudflare verification to prompt execution of code retrieved through a Cloudflare Quick Tunnel. Analysis found that the Windows loader used encrypted Tox peer-to-peer communications for commands and payload delivery, with recovered files indicating shortcut-based persistence and potential elevation and process-hiding capabilities whose successful use was not established.
A seller advertised the Windows malware loader AvisLoader on a cybercrime forum. The seller claimed operators could relocate its controller by copying a Tox save file while preserving its identity and client connectivity without a domain.
Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.
Pull the IOCs, campaigns, and victimology behind this family, ready to push into your SIEM and EDR.
2 references tracked. Mallory keeps watching after this page renders.
Map indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
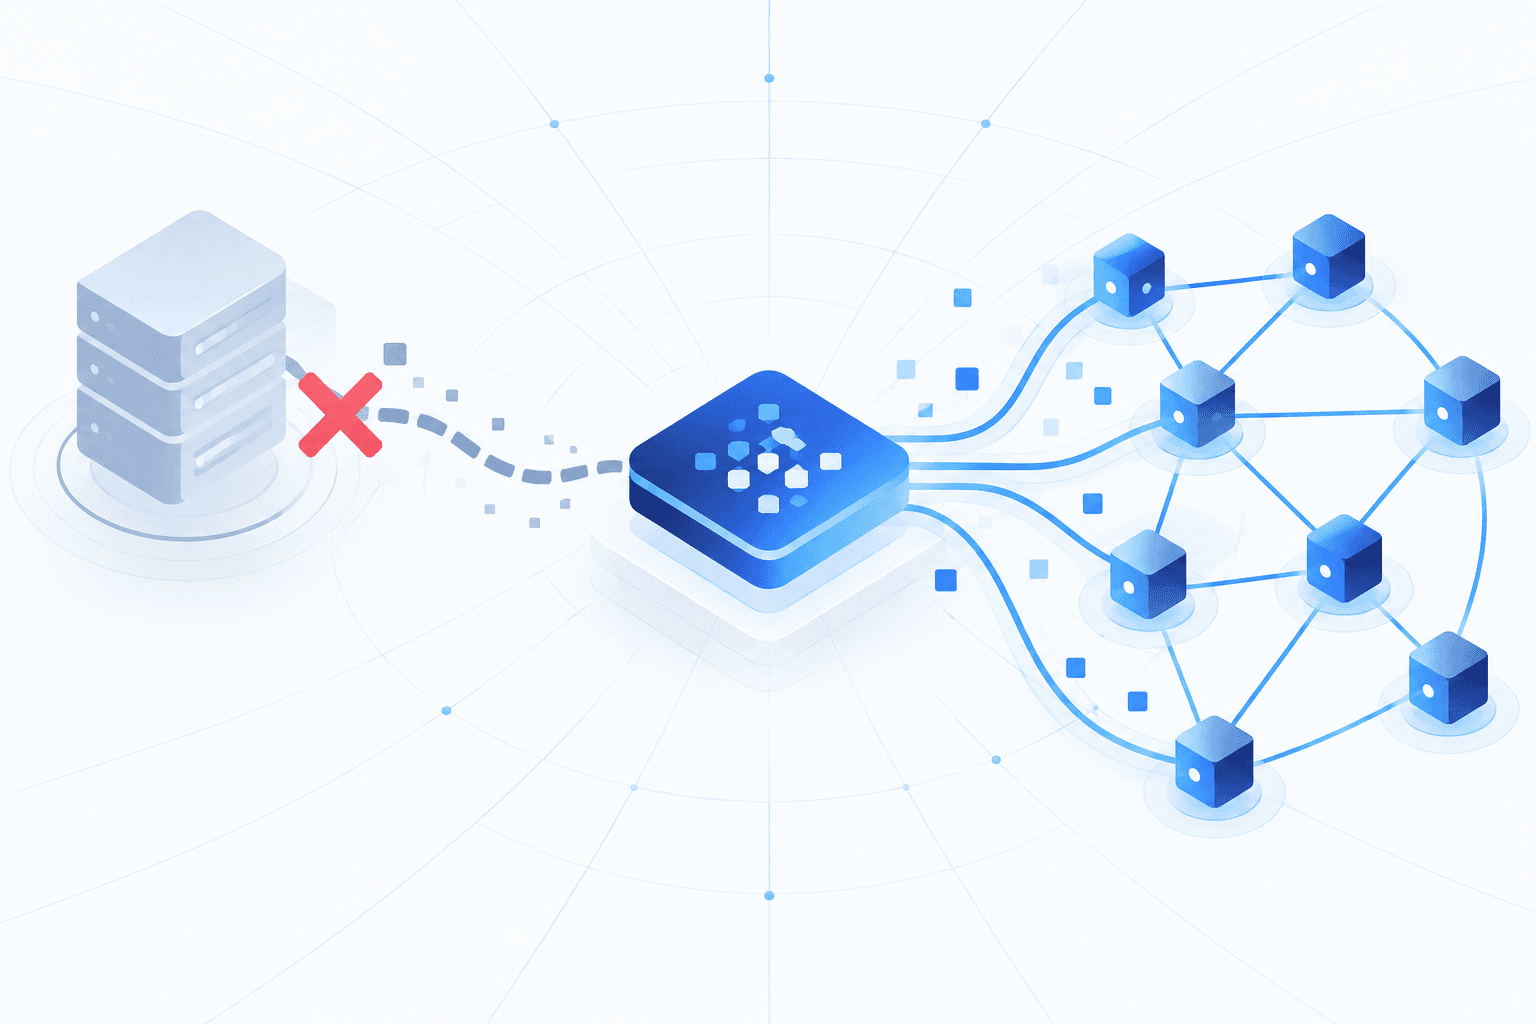
Varonis Threat Labs identified **AvisLoader**, a 64-bit Windows loader spread through a ClickFix lure impersonating a DocuSign signature request. Victims are instructed to paste an attacker-controlled command into a terminal, which retrieves code through a Cloudflare Quick Tunnel and bypasses normal browser download controls. AvisLoader statically links `c-toxcore` and uses the encrypted, decentralized Tox peer-to-peer network for command-and-control and payload delivery, eliminating dependence on a fixed server or domain and complicating takedowns. Its command center supports host inventory, attribute-based tasking, shell-command execution, and file staging; recovered components also indicate possible shortcut-based persistence, UAC bypass, and process hiding, although successful deployment of those capabilities was not confirmed.
Sep 28, 2026
Researchers linked **PavinLoader**, a multi-stage `.NET` malware loader, to several intrusion chains that used **ClickFix lures, fake software downloads, and malicious RenPy packages** to infect victims. Across the campaigns, operators relied on trojanized and heavily obfuscated `.NET` DLLs, along with abuse of **MSBuild** through `.csproj` and `.bat` files, to execute later stages while complicating analysis and detection. The loader retrieved command-and-control details using **EtherHiding**, including Binance Smart Chain RPC calls to pull infrastructure data from blockchain-hosted content, and then fetched additional payloads. In observed cases, PavinLoader delivered **Amatera Stealer** and at times **HijackLoader**, while also using anti-analysis and anti-forensics measures such as AMSI/ETW-related evasion strings, virtualization checks, locale filtering, and infrastructure-provider checks; shared artifacts and builder-like scripts led researchers to assess that it may be operated as a **Loader-as-a-Service**, though no commercial panel or offering was confirmed.
Aug 25, 2026
Multiple threat reports describe **ClickFix-style social engineering** and related Windows loader chains that trick users into launching malicious PowerShell or staged binaries, culminating in **memory-resident malware**. In one campaign, a fake CAPTCHA coerces victims into running PowerShell that fetches a first-stage script, injects a .NET loader into `powershell.exe`, and launches a **Donut 0.9.3** shellcode package entirely in memory to deploy an infostealer targeting Firefox data, Chromium cookies, and screenshots. Separate reporting also tied ClickFix activity to **HijackLoader**-based stealer delivery and to a campaign abusing signed **Mozilla Firefox** binaries for **DLL sideloading** of **KongTuke**, with Rust-based DLL variants handling loading, persistence, and command-and-control. Another analyzed infection chain used a heavily obfuscated batch-script loader that rebuilt embedded payloads, renamed PowerShell to `HDVz.exe`, staged files under `C:\ProgramData\IntelDriver`, and created a scheduled task for logon persistence before injecting Donut shellcode into `explorer.exe`. That malware tampered with **AMSI** and **ETW**, used a custom memory marker `DE AD BE CA FE BA EF` to avoid duplicate injection, and sent execution notifications through the **Telegram Bot API** while attempting outbound communication to `167.88.167.9:8356`. Across the reporting, the common pattern is the use of **trusted binaries, in-memory execution, shellcode loaders, and evasive tradecraft** to steal data or maintain access while minimizing disk artifacts and frustrating endpoint detection.
Aug 15, 2026