Danfoss Refrigeration Controller Flaws Enable Authentication Bypass and Remote Code Execution
Vulnerability Disclosure · 7 sources · Updated 17d ago · First seen Aug 9, 2026
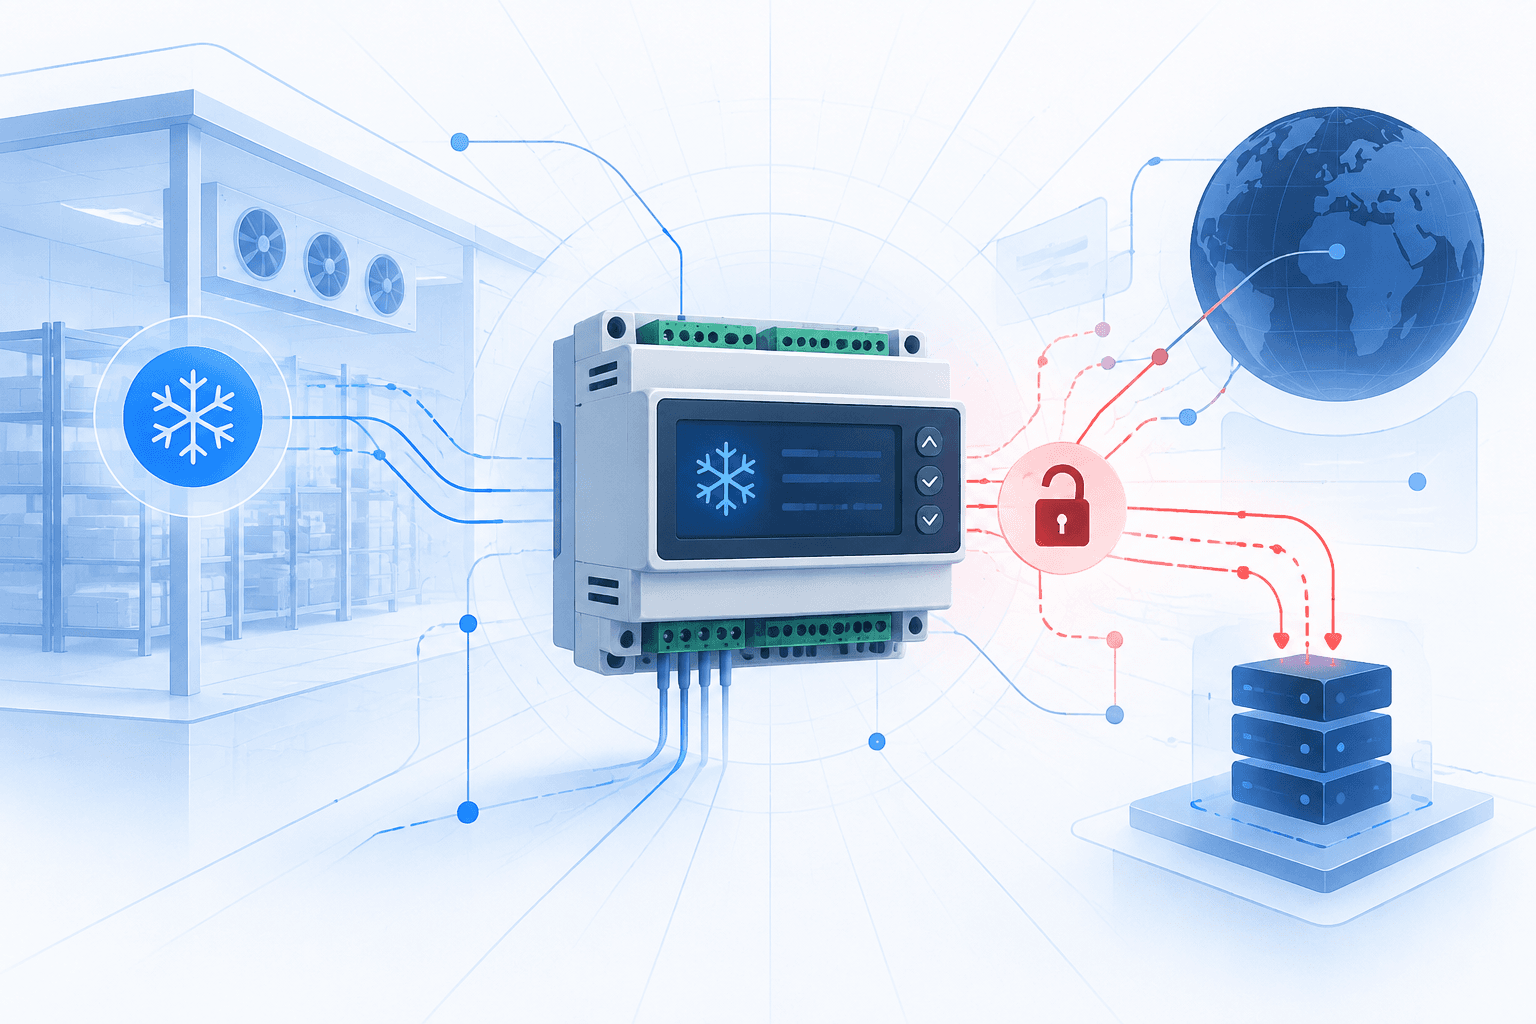
Claroty Team82 discovered three vulnerabilities in the embedded web management interface of Danfoss AK-SM 800A refrigeration controllers that could let attackers bypass administrator authentication, execute commands, and disrupt management access. CVE-2025-41450 exposes a hidden, date-based authentication mechanism that bypasses administrator passwords. CVE-2025-41451 enables remote code execution through command injection in SMTP configuration, while CVE-2025-41452 allows authenticated attackers to inject Nginx configuration directives, manipulate web routing, and cause denial of service to the management interface.
Team82 identified 2,765 publicly exposed devices through Censys, highlighting the potential attack surface for refrigeration infrastructure; that count does not establish that every device was vulnerable or compromised. Following coordinated disclosure, Danfoss addressed the flaws in firmware R4.3.1 and published security advisory DSA-2025-08-01. Operators should upgrade affected controllers and restrict management access to trusted networks or VPNs, reducing opportunities for unauthorized access and disruption of these cyber-physical systems.