Avada Fusion Builder Flaw Lets Unauthenticated Attackers Trigger WordPress Action Hooks
Vulnerability Disclosure · 3 sources · Updated 21d ago · First seen Oct 13, 2026
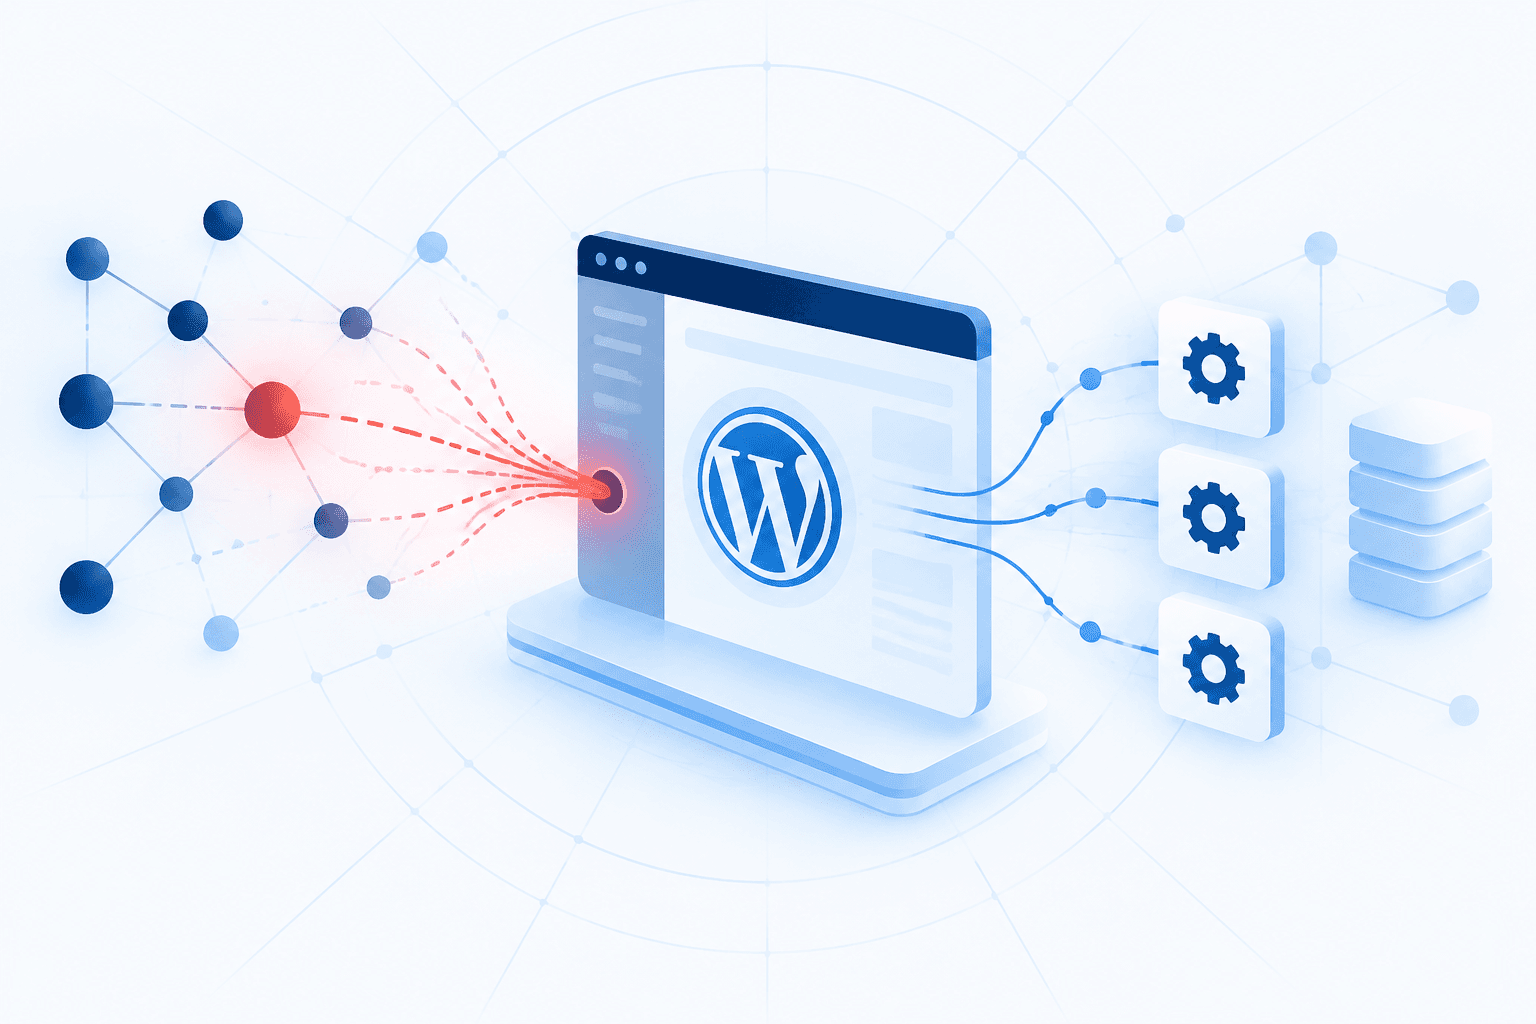
A critical authorization-bypass vulnerability, CVE-2026-97670, affects Avada’s Fusion Builder WordPress plugin through version 3.16.1, allowing unauthenticated visitors to invoke existing WordPress action hooks through crafted public form submissions. Exploitation requires a public AJAX form whose notification template processes submitted fields, including the default [all_fields] setting described by Wordfence. Wordfence verified permanent deletion of trashed posts, pages, and comments already eligible for removal under WordPress retention rules; it did not demonstrate deletion of live content or premature removal of newly trashed items.
Fusion Builder 3.16.2 fixes the vulnerability, delivered with Avada’s September 30 security update for version 7.16.2, ahead of Wordfence’s October 9 disclosure. Bhutan’s Computer Incident Response Team also published an advisory on the authorization bypass. Administrators should update affected installations and review public AJAX forms and notification templates for exposure. The available reporting does not confirm an exploitation campaign.